Legit Security Launches Agentic Remediation for Open-Source Dependency Vulnerabilities
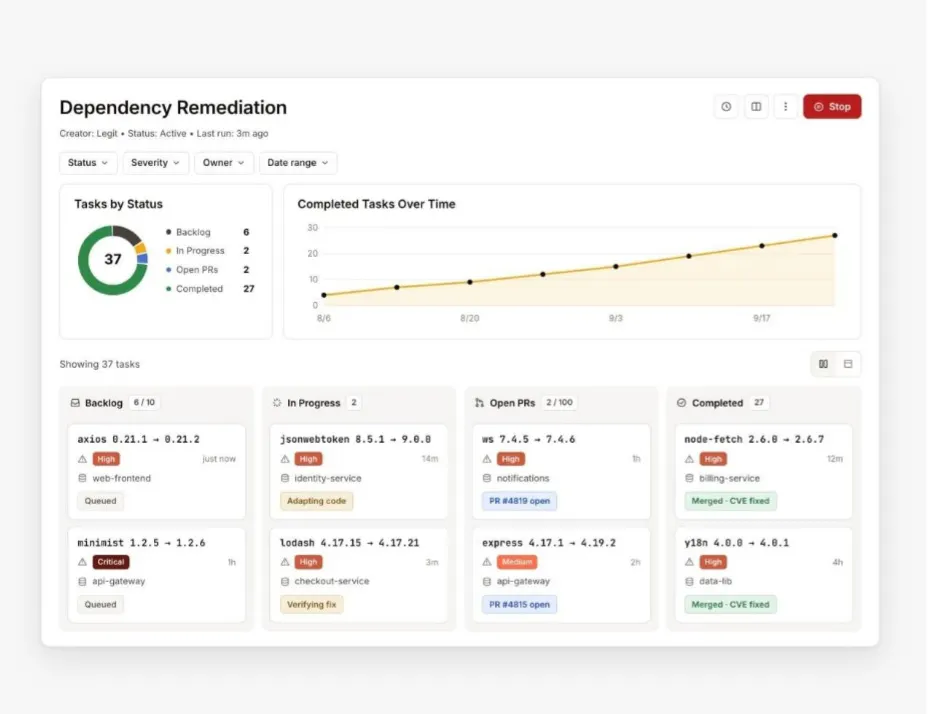
Tel Aviv, Israel, September 30th, 2026/CyberNewswire/--Legit Security today announced an expansion of its Agentic Remediation capability to cover vulnerabilities found in open-source dependencies, not just first-party code – enabling development teams to move from vulnerability detection to a verified fix without manual triage.
The expansion addresses a growing gap in application security: as AI-generated code accelerates software delivery, most modern codebases are made up largely of open-source dependencies, and every new package introduces potential exposure to known vulnerabilities.
Traditional find-it, fix-it AppSec workflows, which rely on human teams working down a backlog, can’t keep pace with that volume – particularly when the vulnerable code isn’t in a company’s own codebase but several layers deep in a third-party package.
Legit’s Agentic Remediation previously focused on fixing static analysis findings in code written by a company’s own engineers. With this release, the same agent now takes on vulnerabilities introduced through dependencies...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE