Securing the Last Mile: Privacy and Compliance in Mobile Payments
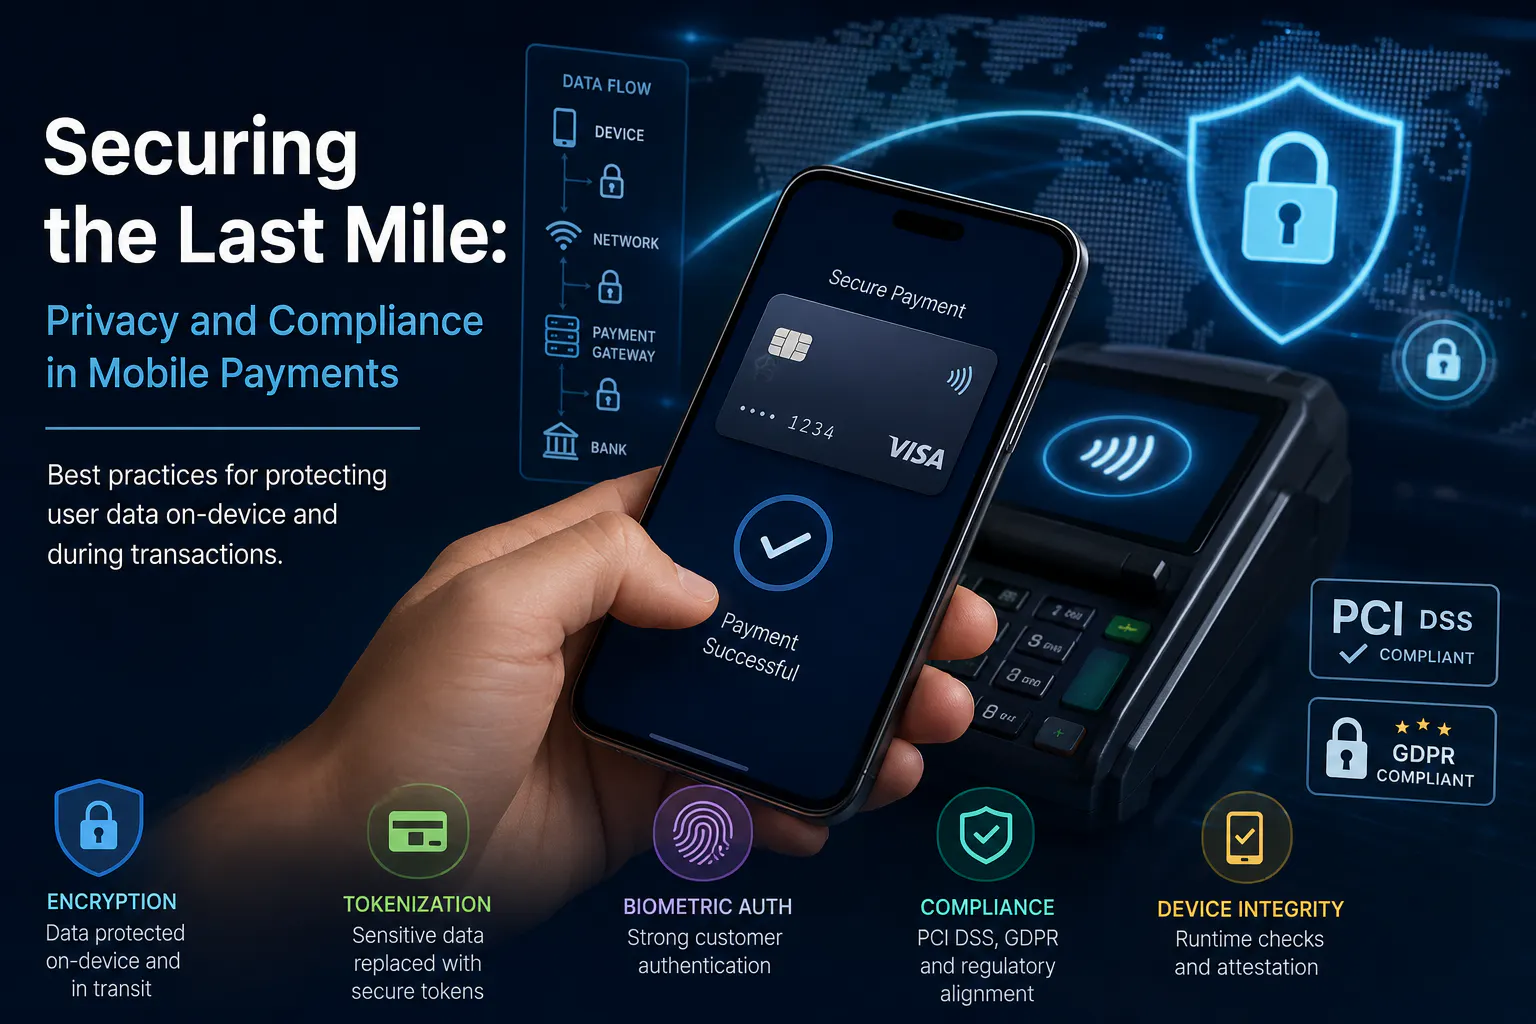
In the modern mobile payment ecosystem, the “last mile” of a transaction – the moment sensitive data is handled on-device and transmitted to a payment terminal or backend – is critical. Ensuring user privacy and regulatory compliance at this stage demands rigorous protections for on-device data and secure channels for network communication.
Mobile wallets and payment apps must avoid common pitfalls like storing card data in plaintext or sending information over unprotected connections. Instead, industry guidelines insist on end-to-end encryption, tokenization, and adherence to standards such as PCI DSS and data protection laws (e.g., GDPR).
For instance, the PCI Security Standards Council explicitly emphasizes that “the same PCI principles apply to mobile for secure coding best practices and protection of account data”. In practice, this means treating a mobile app much like any other payment acceptance endpoint, cryptographically hardening storage and transit layers, minimizing data collection, and following privacy by...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE