TECH NEWS
Bloom Security Found a Supply-Chain Vulnerability Exposing 1,500 npm Packages to Malicious Takeover
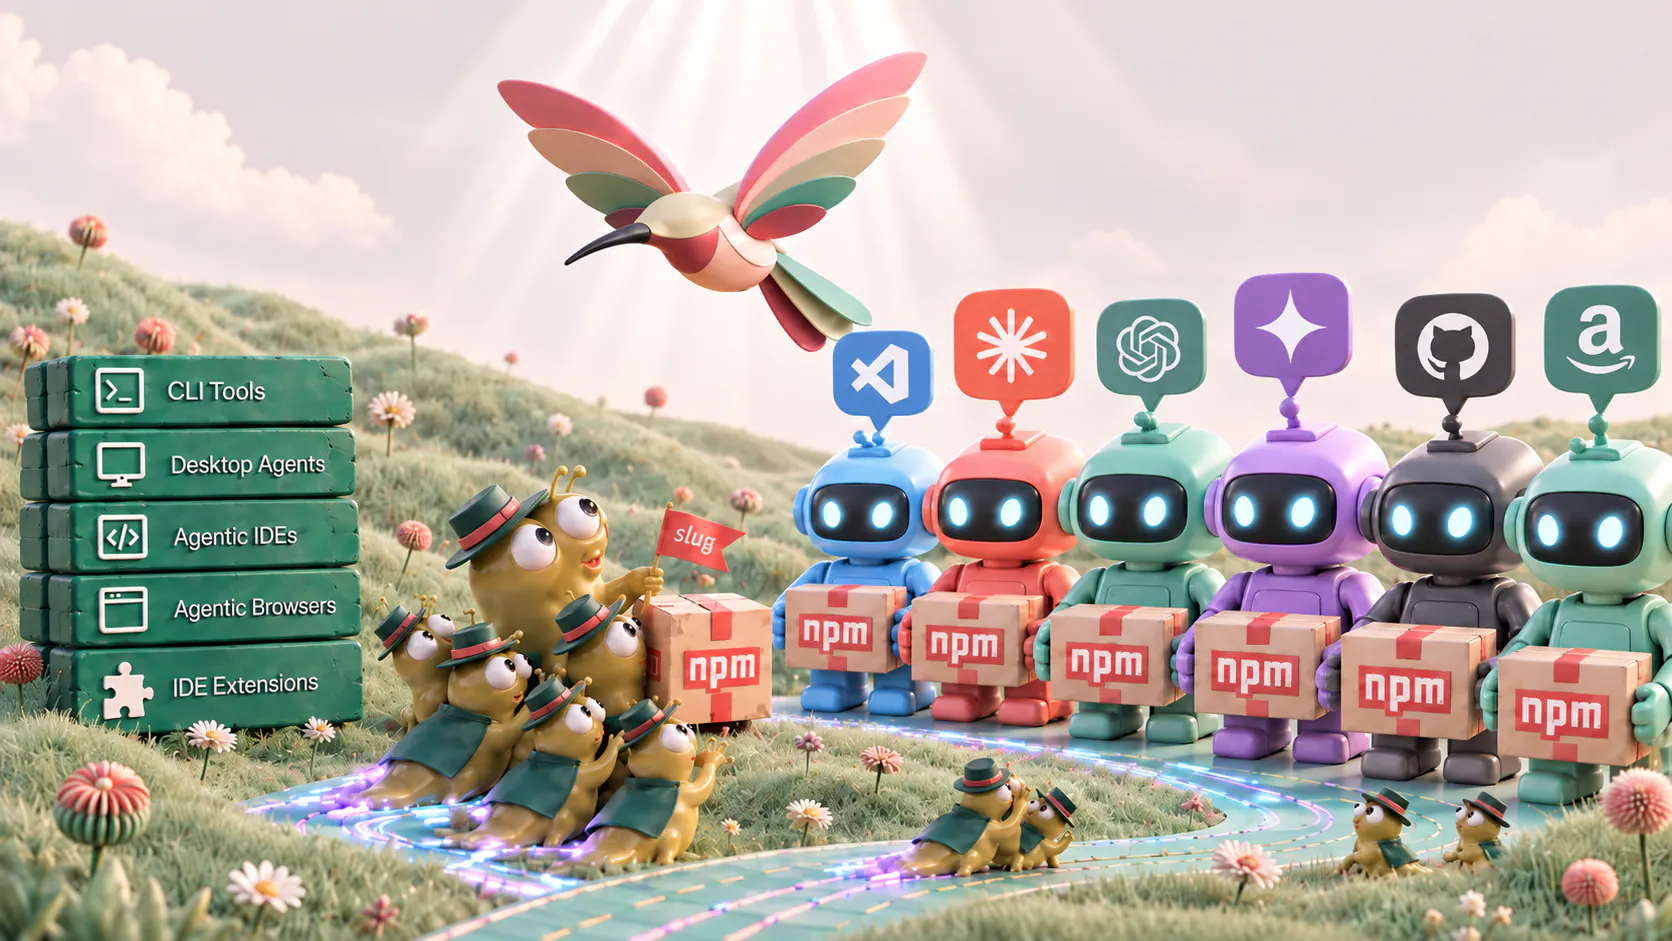
AI coding agents are changing how software gets built, but their growing autonomy is also creating new challenges for software supply-chain security. Tools that automatically select, install, and run dependencies can introduce packages into development environments without the same manual scrutiny traditionally associated with software installation. Research from Bloom Security