Bloom Security Found a Supply-Chain Vulnerability Exposing 1,500 npm Packages to Malicious Takeover
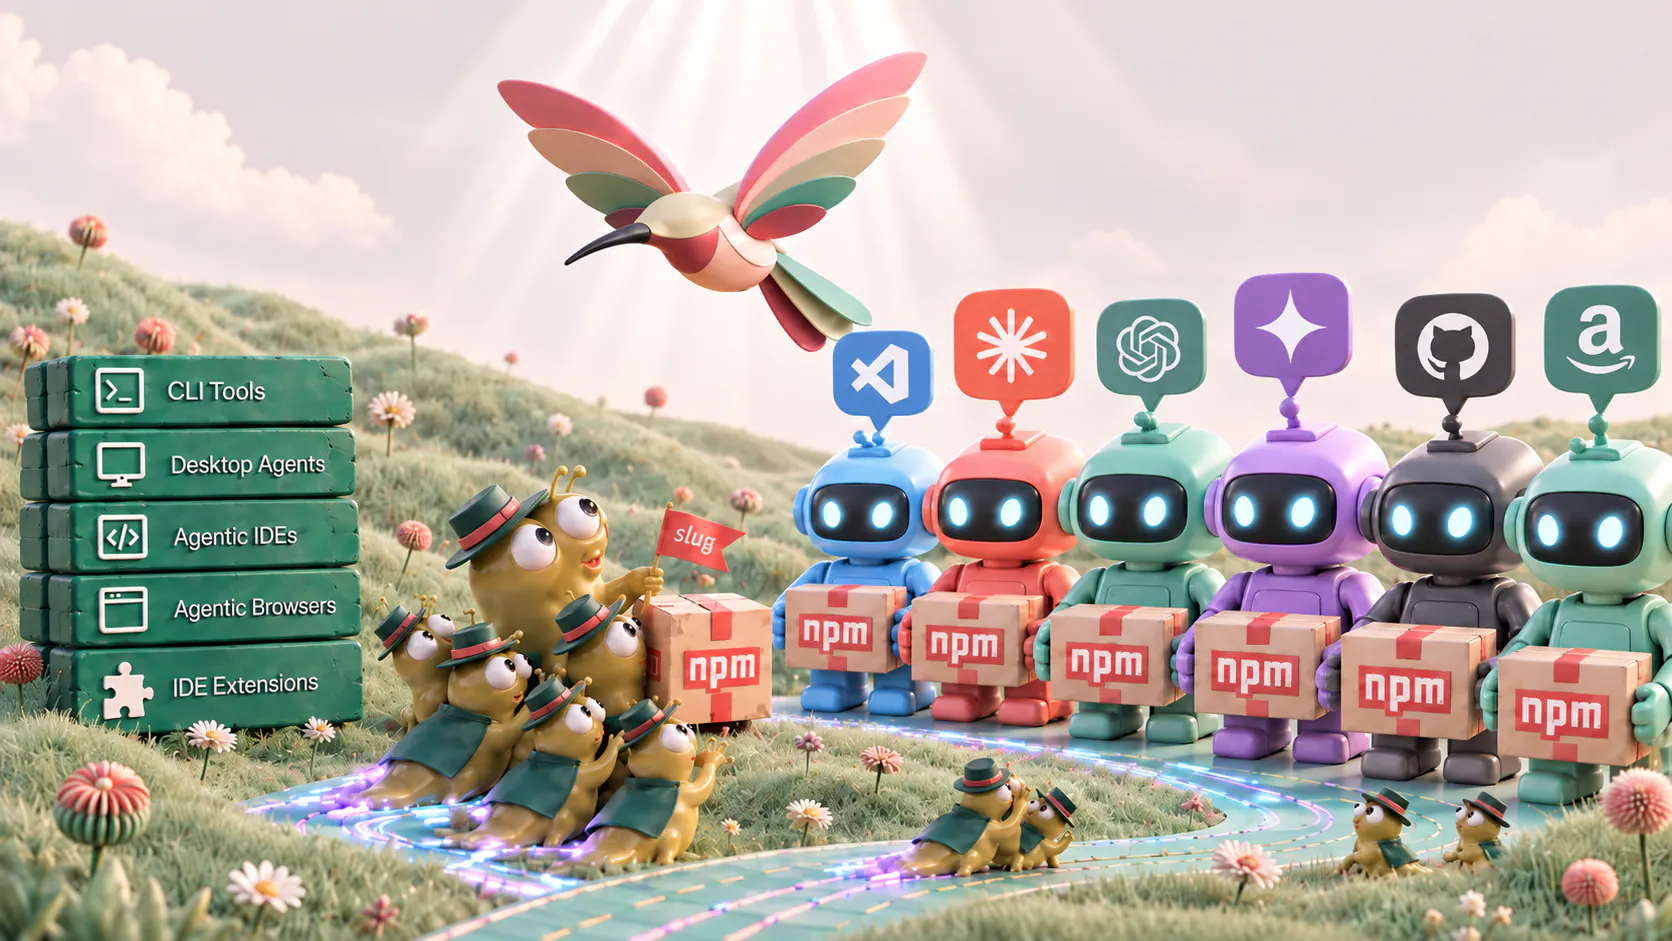
AI coding agents are changing how software gets built, but their growing autonomy is also creating new challenges for software supply-chain security. Tools that automatically select, install, and run dependencies can introduce packages into development environments without the same manual scrutiny traditionally associated with software installation.
Research from Bloom Security highlights how this shift intersects with a vulnerability in npm Trusted Publishing, potentially allowing attackers to publish malicious versions of legitimate packages by reclaiming abandoned GitHub repository addresses. The investigation, dubbed SlugFest, identified more than 1,500 vulnerable npm packages with over 10 million combined downloads, demonstrating how a relatively narrow weakness in a publishing mechanism could create a broader supply-chain risk.
How AI Agents Are Changing Software Supply-Chain Exposure
Bloom Security studied the behavior of millions of AI agents across large enterprises and found that the average endpoint receives approximately 70 agent-installed packages per month. On developer machines, the number...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE