How MSPs Can Vet Outsourced Technical Support Providers for ISO 27001, SOC 2 and Client Access
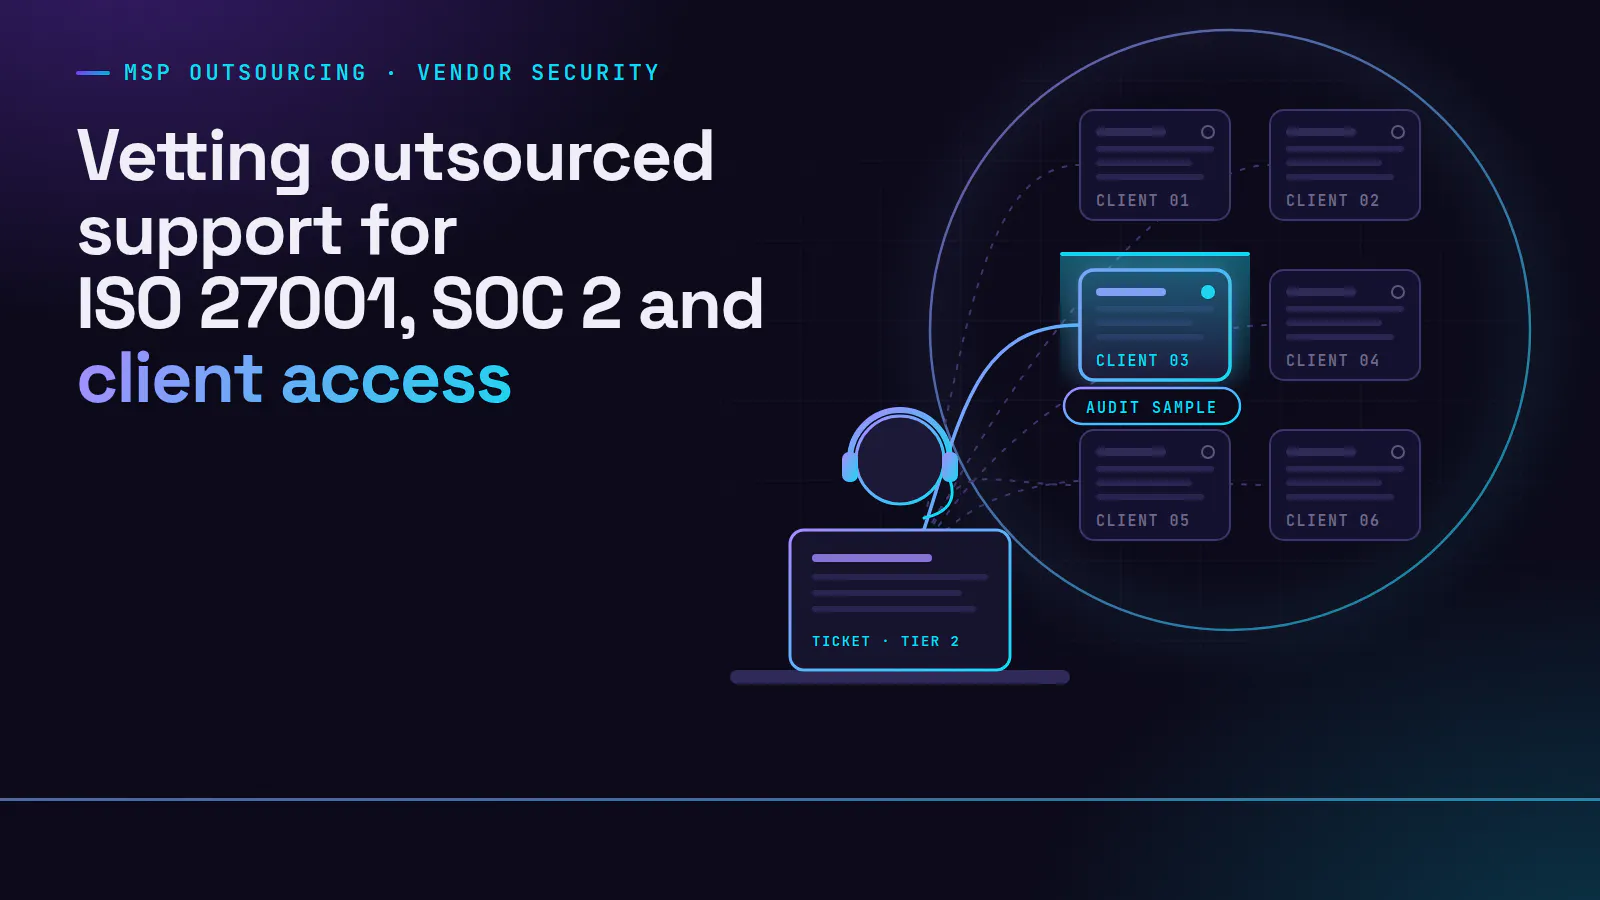
Verizon's 2026 Data Breach Investigations Report found that third parties played a role in 48% of breaches, up from 30% the year before. ISO 27001 requires certified companies to manage that risk through their suppliers, and guidance for its Annex A 5.21 control carries those security requirements past a company's vendors to their subcontractors. When an MSP outsources support, the outside engineers who log into a client's systems join that chain. The client has no contract with the outsourcing firm, so it asks the MSP to prove the firm meets its security terms.
LTVplus, a managed technical support partner that recruits, trains and manages dedicated Tier 0-3 engineers for MSPs, handles that request in its sales process. "Our engineers work under the MSP's name. The client experiences one provider, and we're built to keep it that way," said David Henzel, Co-Founder of LTVplus. The audit works from the access...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE