Governing Context at Scale: Security, Observability, and Multi-Agent AI
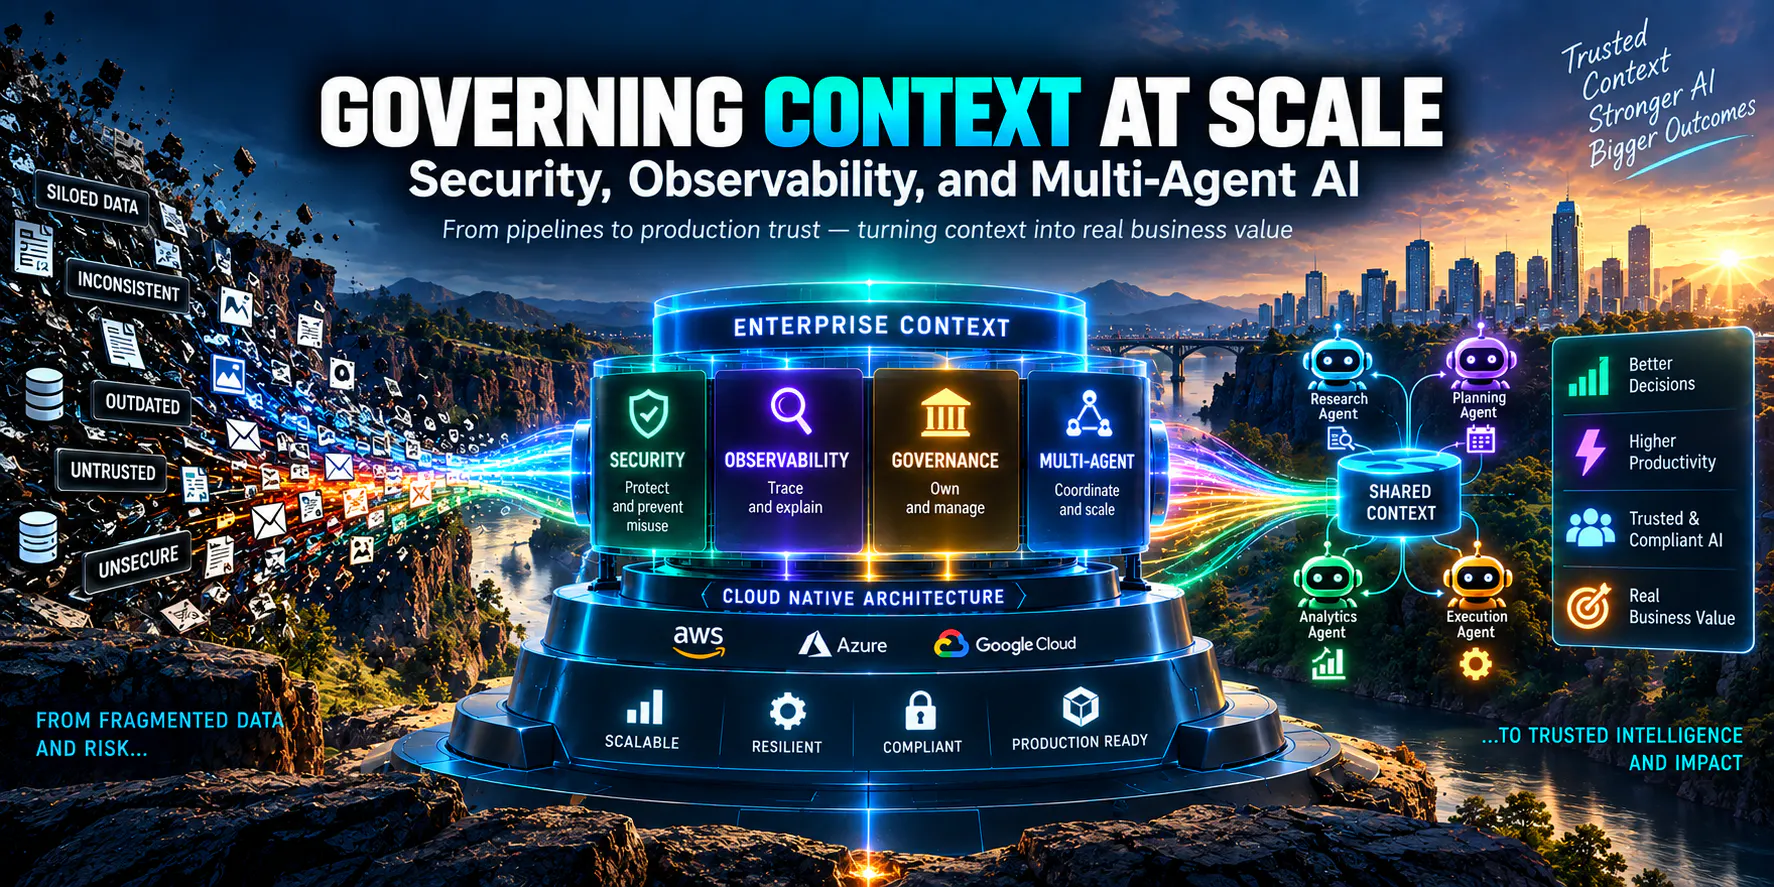
Part 1 defined what good context looks like. Part 2 showed how to build the pipeline that produces it. A pipeline that works in a demo, though, is not the same as one you can trust in production for years. Once context becomes the foundation for enterprise decisions, a new set of questions shows up: Where did this answer come from? Was the user allowed to see the data behind it? Who decides which sources are trusted? What happens when several AI agents draw on the same knowledge at once?
These aren't engineering questions so much as operating questions. This final installment is about running context responsibly at scale: managing it as a product, securing it, observing it, governing it, and coordinating it across multiple agents.
Picture an enterprise AI assistant supporting transportation and logistics operations. It pulls shipment data from a transportation management system (TMS), carrier APIs, enterprise documents,...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE