From Global Allowlist to RCE: Breaking Down CVE-2026-50023 in yt-dlp
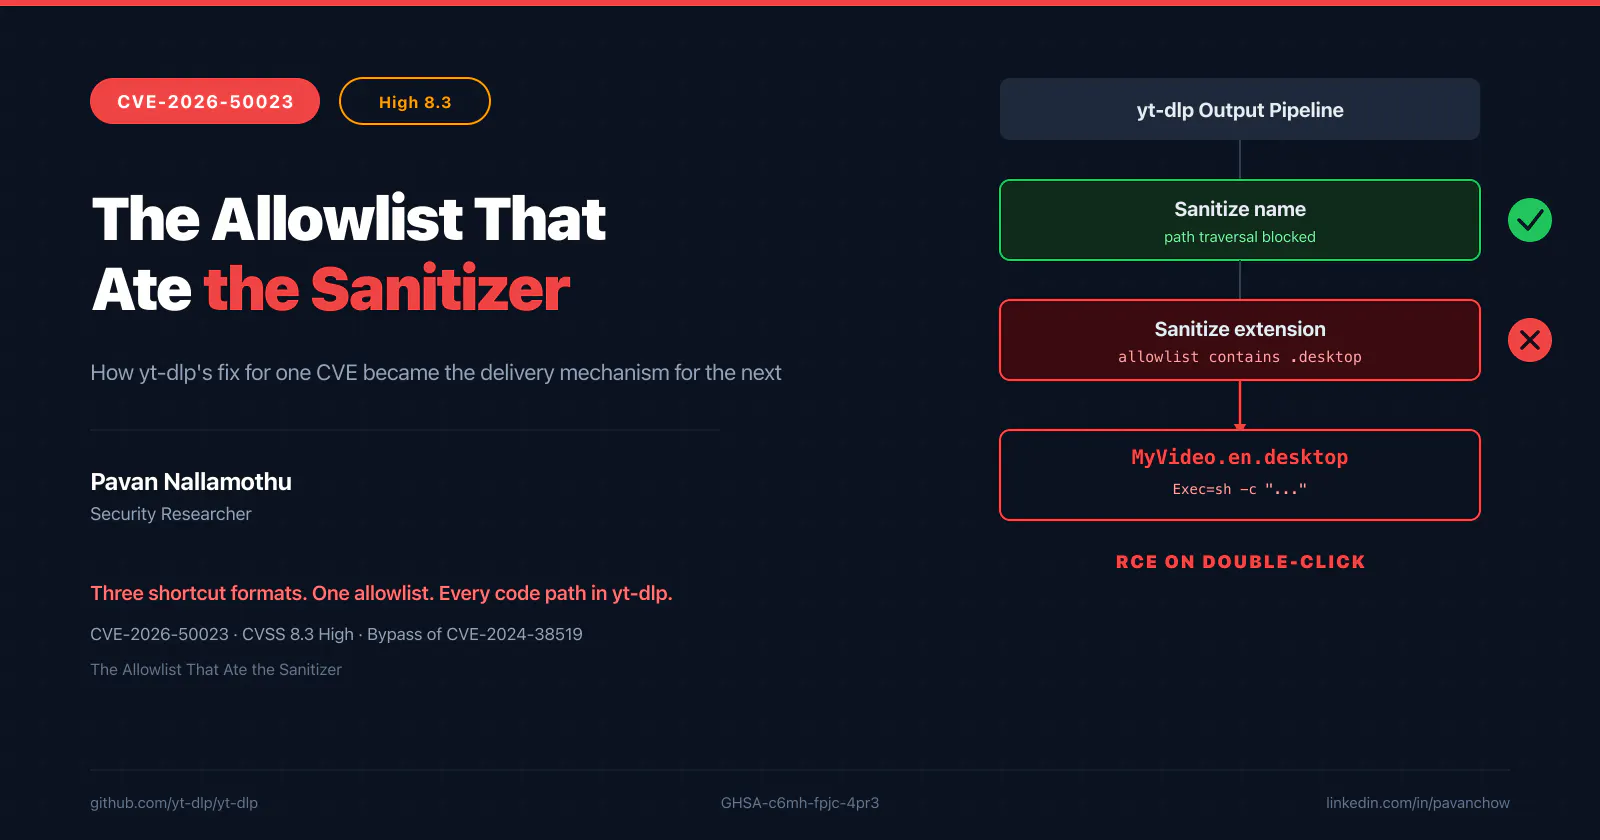
You paste a link. yt-dlp fetches a video. In the same directory, a .desktop file lands next to your subtitles. Your file manager hides the extension and shows a friendly name. You double-click what you think is an .srt. A shell command runs as you.
That is the whole bug. The rest of this post is how it got there, why the patch for the previous CVE was the delivery mechanism for this one, and why the follow-up CVE two months later says the class was never really closed.
Starting on the old CVE
I did not go into yt-dlp looking for a new bug. I went in to understand an old one.
CVE-2024-38519 was a filename-sanitization issue. yt-dlp was writing files whose names came from remote metadata, and on Linux desktops that meant an attacker could get a .desktop shortcut written to your download folder by choosing the right...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE