Compliance Isn't the Bottleneck: Seven Years of Lessons From Building Regulated Financial Products
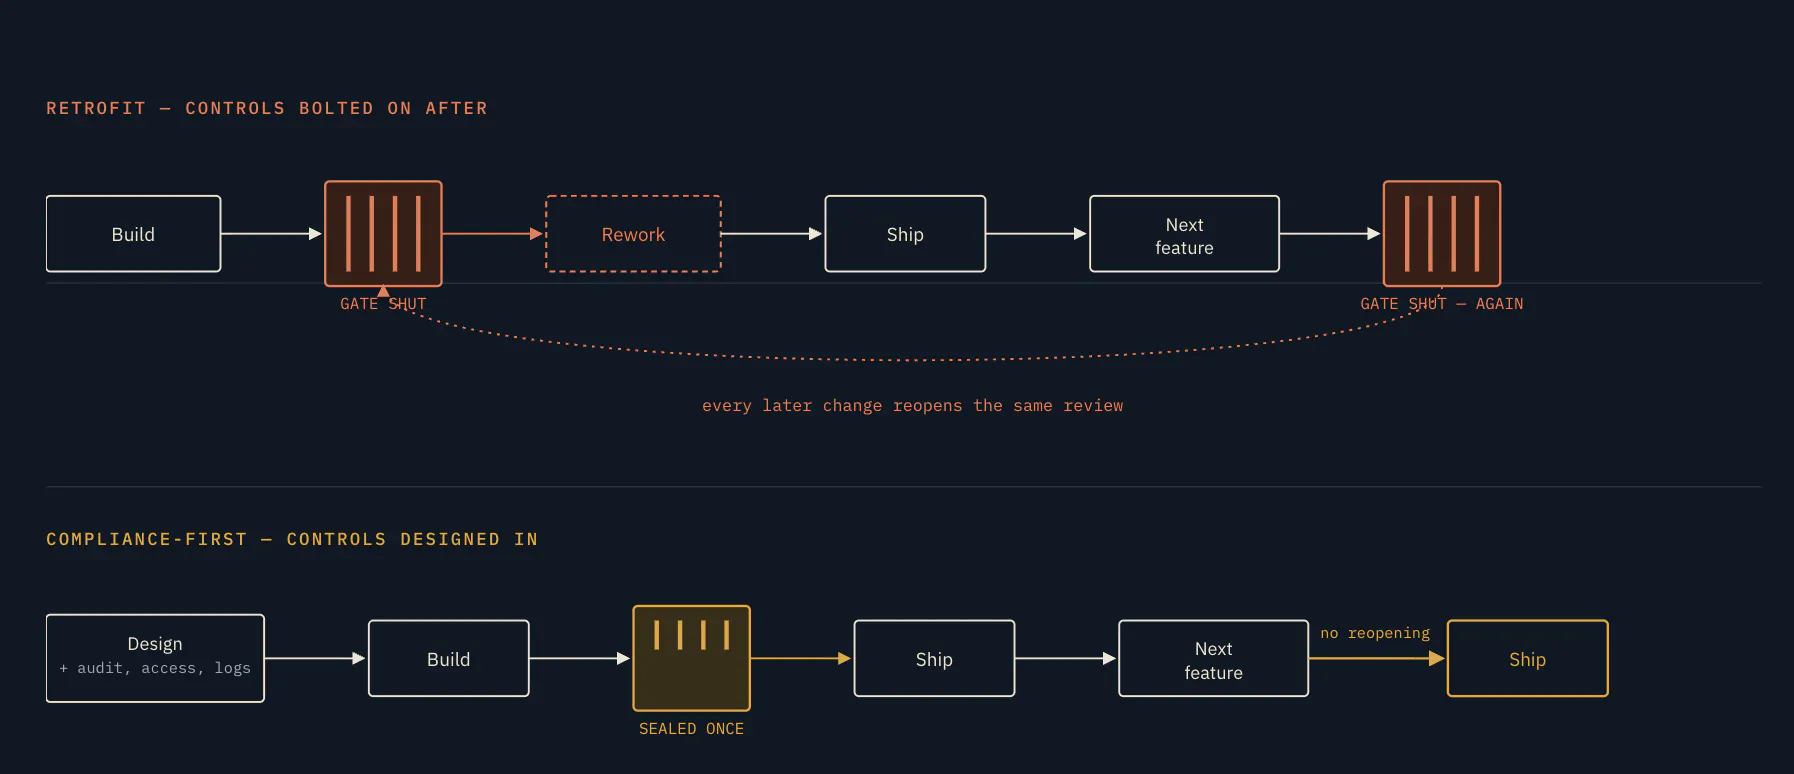
Shipping software in regulated financial services gets called "slower" than shipping consumer software. I'd frame it differently: the pace problem isn't the regulation itself. It's how teams treat regulation, as legal red tape bolted on at the end instead of a design requirement built in from the start. That mistake, not the rules themselves, is what actually slows teams down. Across roles spanning credit risk, payments data platforms, and financial-crime compliance, here are three lessons that reshaped how I think about shipping in this space.
Lesson 1: Compliance-First Architecture Isn't Slower. Retrofitting It Is.
Early in my career, I worked on migrating a KYC (know-your-customer) workflow from a manual workflow to a cloud platform, covering onboarding, sanctions screening, and identity verification for tens of thousands of business clients. The instinct on a project like that is to build the workflow first and bolt on audit trails and access controls once...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE