Admin Keys, Phishing, and DNS: The New Front Line of Crypto Security
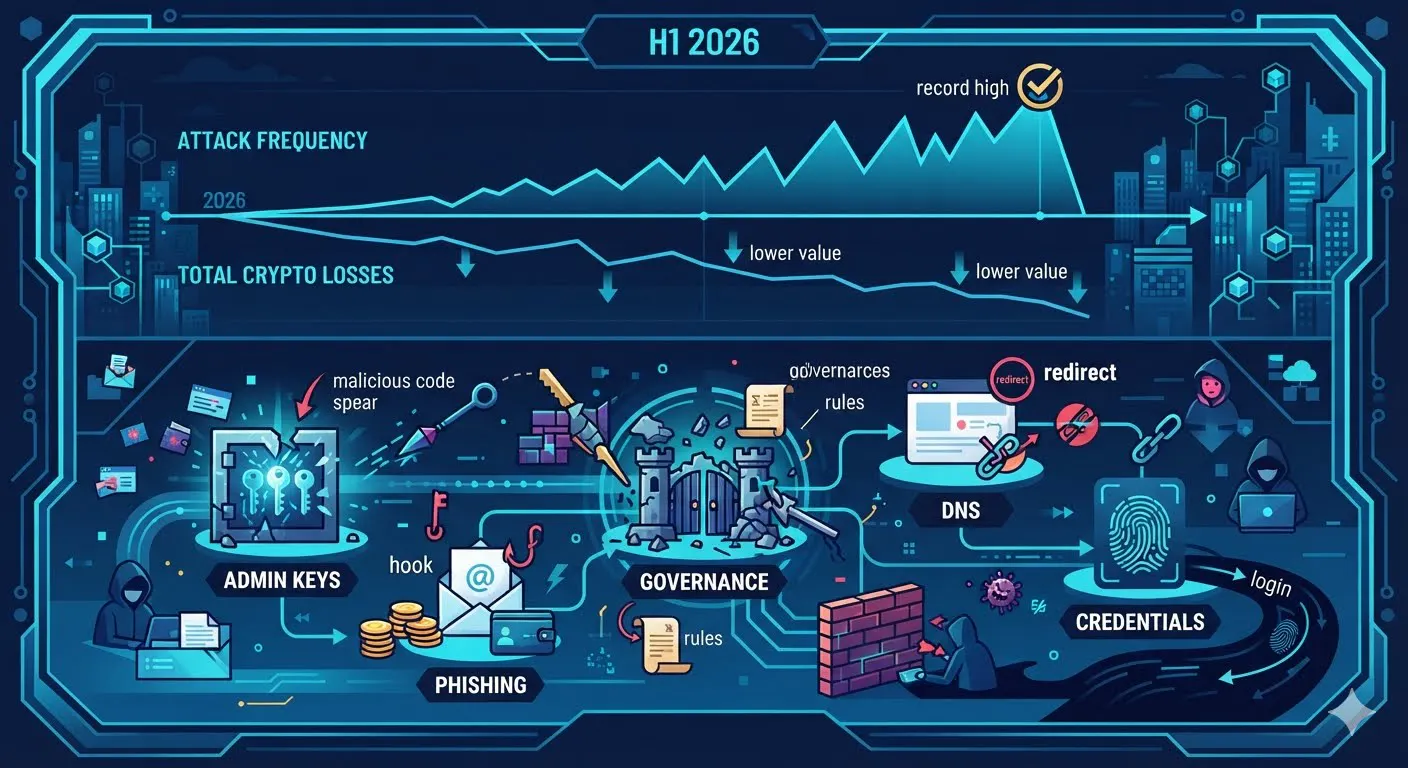
Roughly$972 million was lost across 207 incidents in the first half of 2026, less than half the total of the same period a year earlier, while the incident count more than doubled from 83 and set a record.
Attacks became more frequent and less profitable at the same time. That is a change in where the money leaves, not in whether protocols get attacked.
Losses Fell. Attacks Did Not.
For most of the past five years the industry's working model of crypto risk began and ended with a contract bug. The apparatus built around that model changed the economics of attacking the code well enough that breaking a contract is no longer the only route to a major loss . Verification got formal, audits got repeated, bounty programs became standing rather than occasional.
None of it reduced the capital sitting inside those protocols. Immunefi, which operates bug-bounty infrastructure for...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE