Why PKI May Be One of the Hardest Parts of the Post Quantum Migration
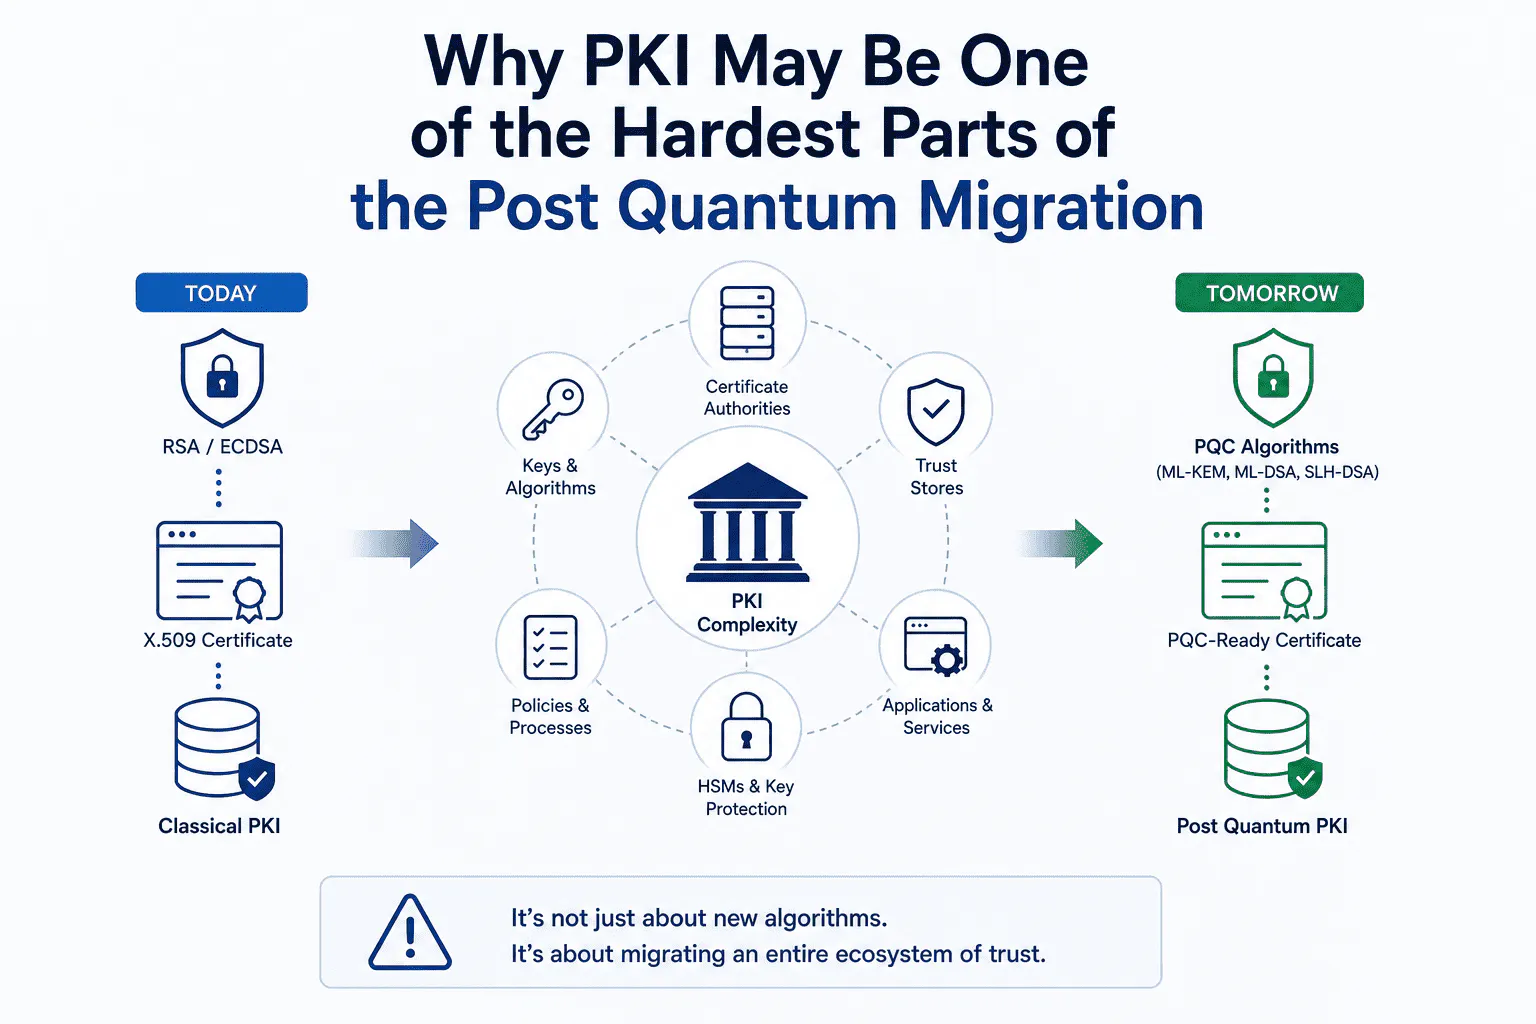
Post-quantum migration is often described as an algorithm replacement exercise: move from RSA and elliptic curve cryptography to quantum-resistant alternatives such as ML KEM, ML DSA, and SLH DSA. That description is technically incomplete.
The difficult part is not simply selecting a new algorithm. It is replacing cryptographic mechanisms embedded across certificate authorities, trust stores, certificate profiles, HSMs, validation systems, workload identities, applications and automated certificate workflows without breaking the trust relationships connecting them.
NIST finalized FIPS 203 for ML KEM, FIPS 204 for ML DSA, and FIPS 205 for SLH DSA in August 2024. ML KEM addresses key establishment, while ML DSA and SLH DSA provide digital signatures designed to withstand future quantum attacks. NIST now advises organizations to begin migrating systems to quantum-resistant cryptography and to identify where vulnerable algorithms are being used.
The harder question is therefore operational: how can enterprises migrate the public key infrastructure surrounding...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE