Why Compliance Teams Keep Rejecting "Anonymized" Production Data
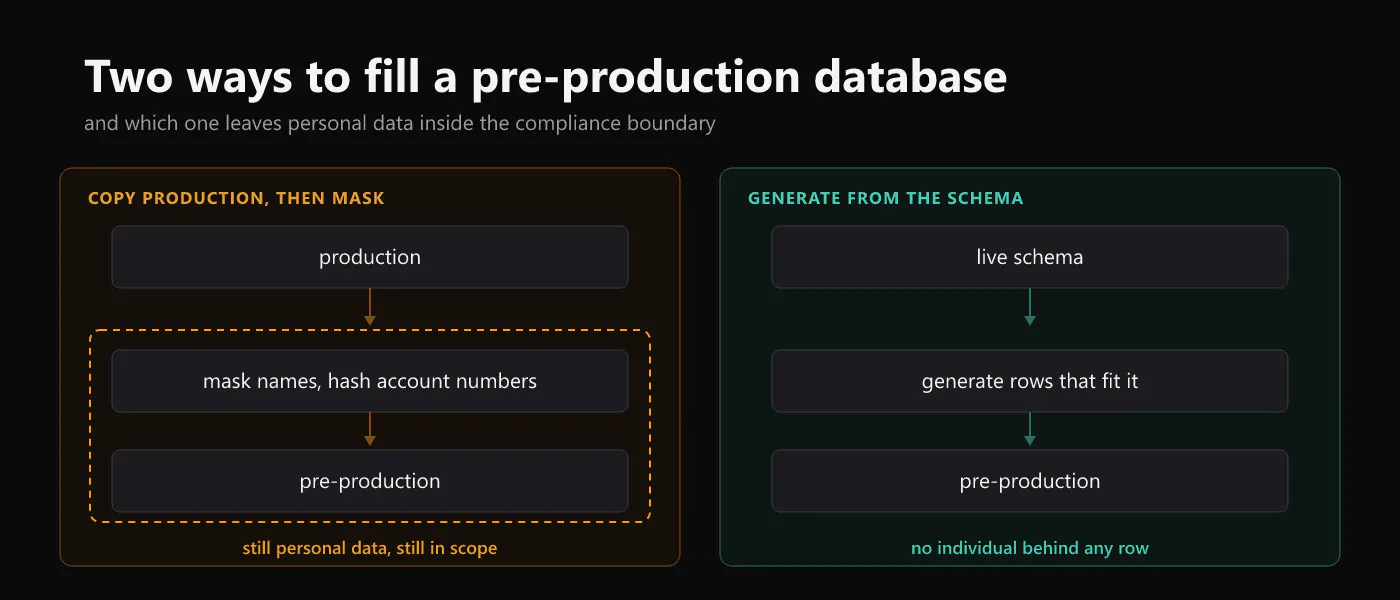
Ten minutes into our SOC 2 audit, the auditor asked where our test data came from, and I told her it was anonymized production data, in the tone of a man who has just said a correct thing. She wrote it down, then asked how it had been anonymized, and somewhere in the pause that followed I worked out that I did not really know.
What we did in practice was swap the name and email columns for generated strings, hash the account numbers, and ship everything else exactly as it came out of the nightly dump. I had been calling that anonymization for about eighteen months. It took another fortnight and a lot of reading before I understood that the correct word was a different one, and that the gap between the two words was most of the argument I had just lost.
That conversation happens long before anyone...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE