What a GitHub Actions Cache Can Expose to Anyone Who Opens a Pull Request
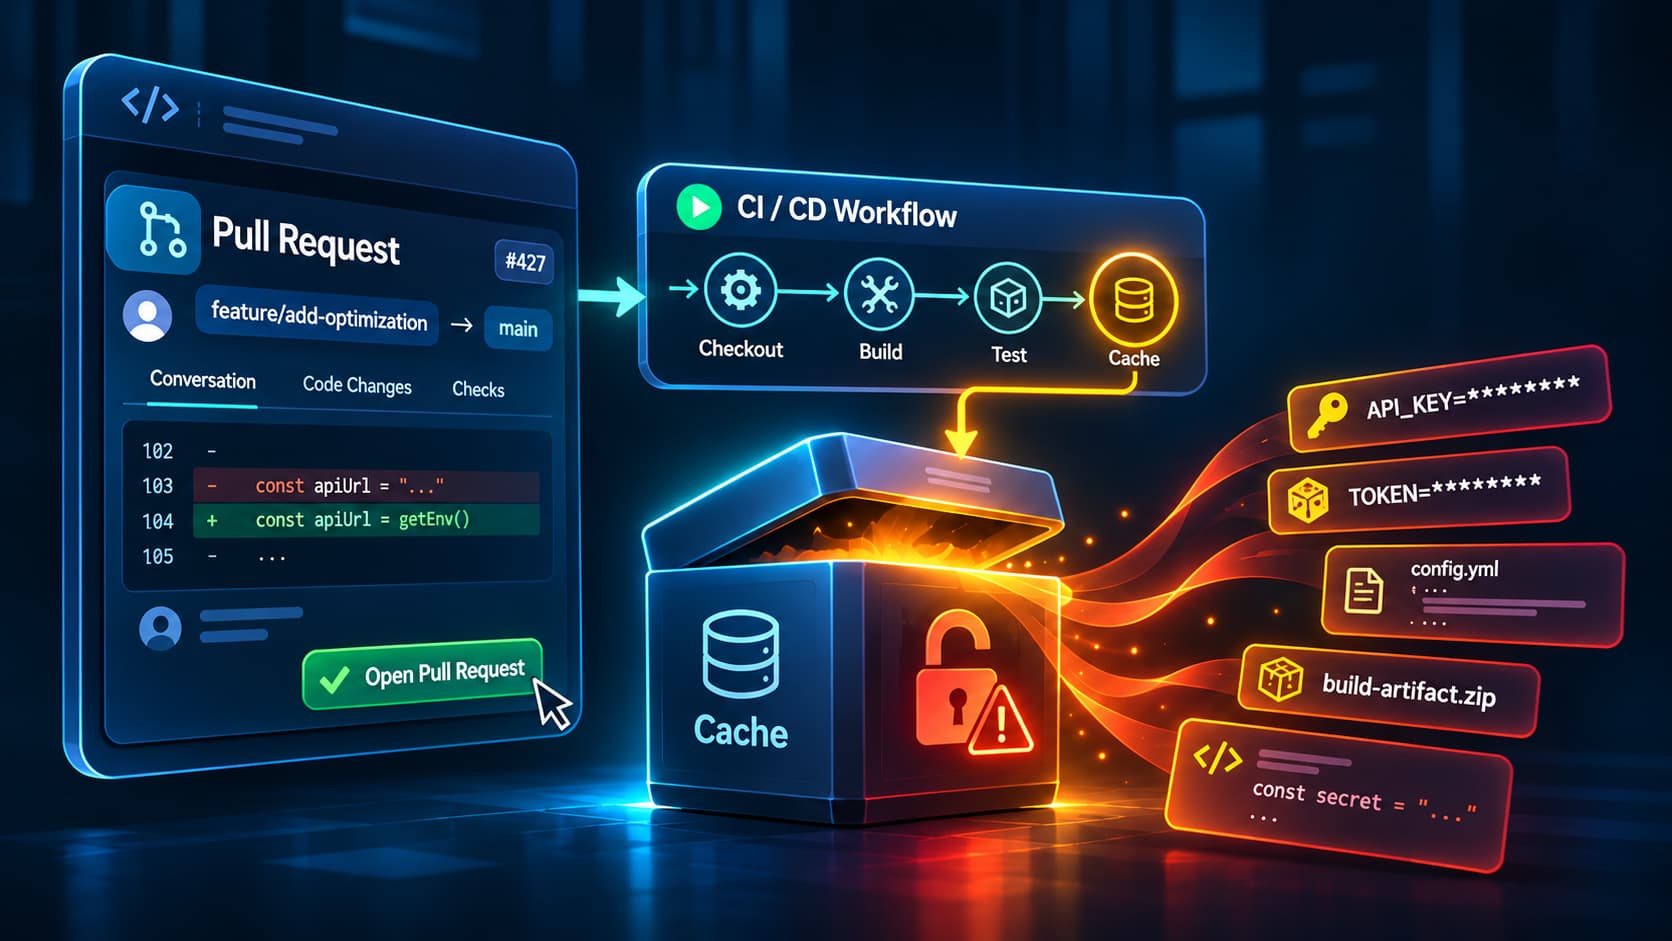
The GitHub Actions cache is commonly used as a timesaver in the dev community. It allows developers to shortcut the laborious process of downloading and installing dependencies and having to rebuild outputs, which makes builds faster and cheaper. While this is certainly praiseworthy, it can create a loophole for malicious actors to exploit.
GitHub lets pull request runs restore caches from the base branch, and that includes pull requests opened from forks, by people outside your team. That means that if you’re running a public repository, anyone can create a fork and read whatever has been cached on the main branch. Even with private repositories, anyone with read access can run the same stunt, which could be an enormous number of people if you aren’t careful about rescinding permissions.
This is not just a theoretical danger. The GhostAction campaign showed how attractiveCI credentials are. Attackers read projects’ existing workflow...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE