Watch out — TP-Link Tapo Camera vulnerabilities could let hackers spy inside homes, so patch now
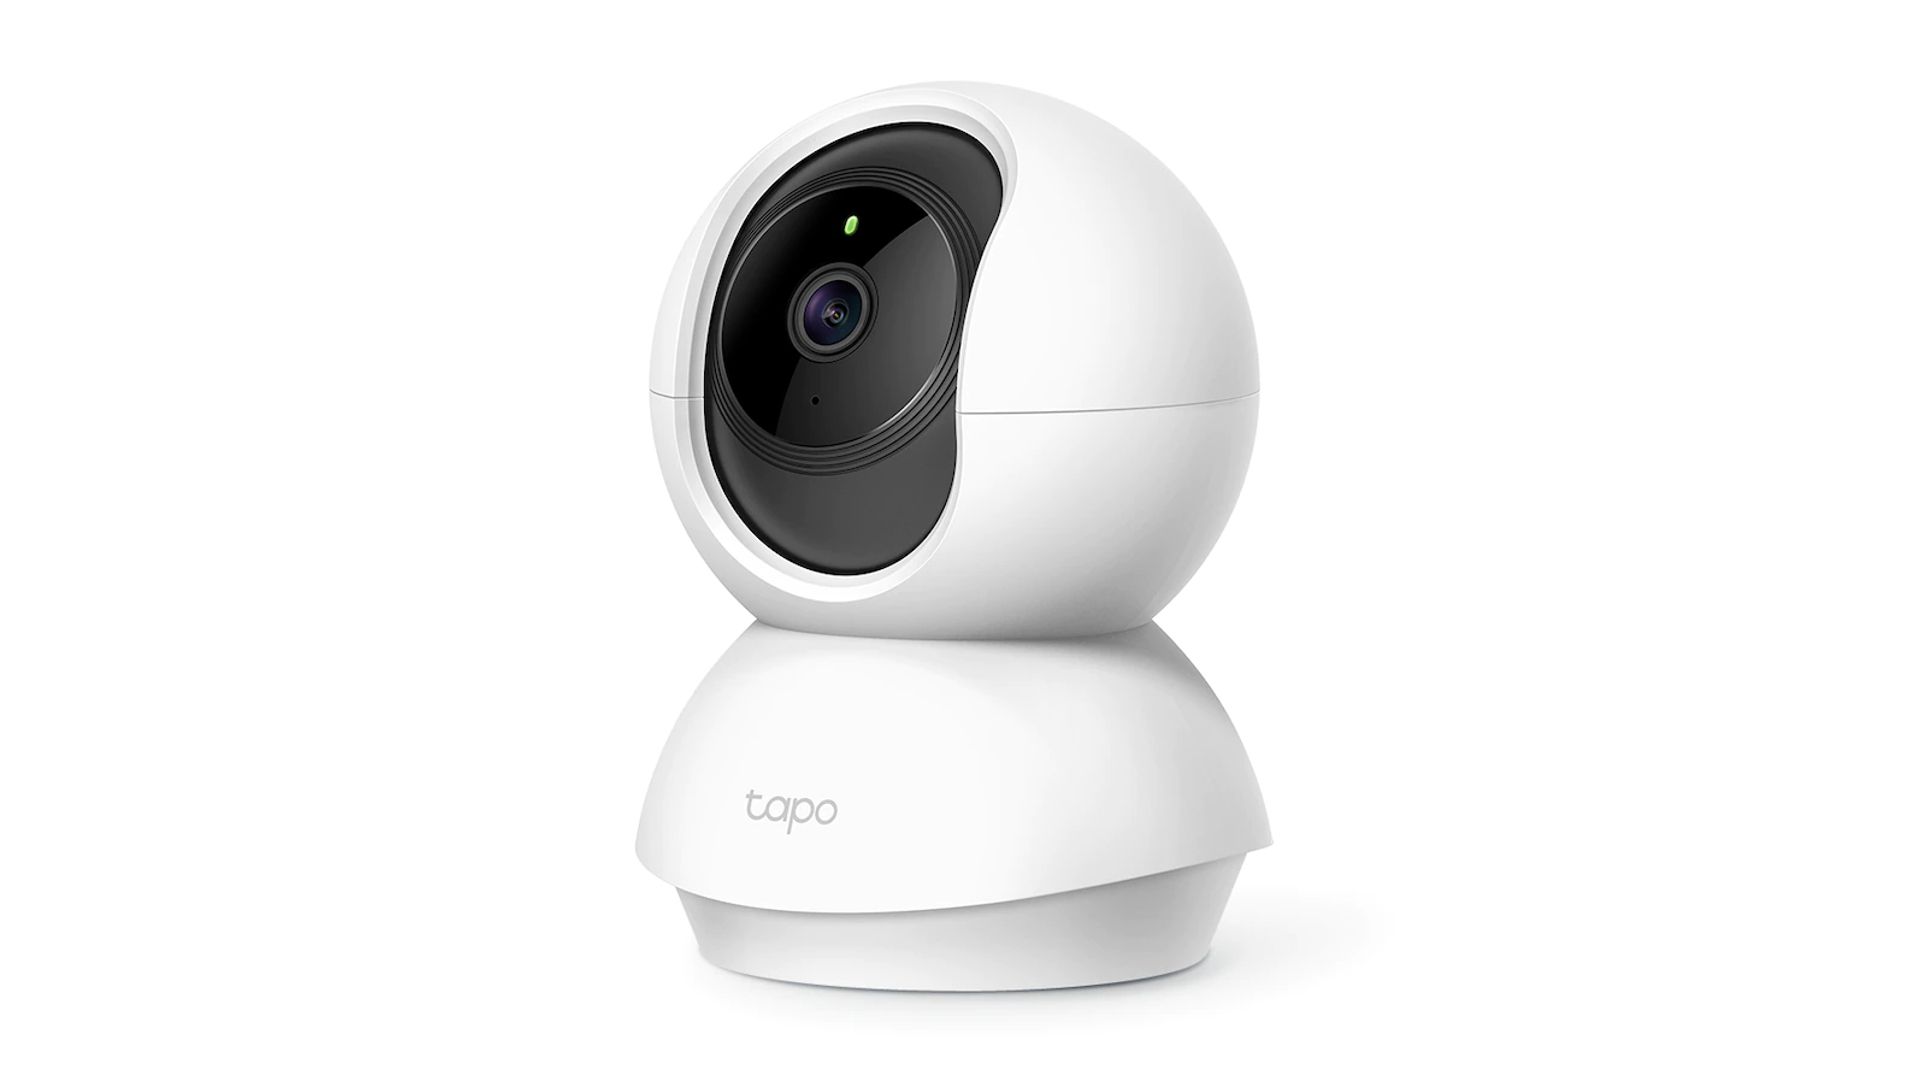
- Opswat found two flaws in TP‑Link Tapo C200 cameras: auth bypass (CVE‑2026‑15315) and DoS (CVE‑2026‑15316)
- Bugs let attackers hijack admin sessions or crash devices; millions of users potentially exposed
- TP‑Link patched with firmware V5_1.4.6 on Aug 18, 2026; users urged to update immediately
Security researchers found a pair of vulnerabilities in popular smart cameras, which could allow threat actors to peep into people’s homes and businesses.
Earlier this week, Opswat disclosed finding two bugs in the TP-Link Tapo C200 smart security camera - an authentication bypass flaw, and a denial-of-service vulnerability. The former is tracked as CVE-2026-15315 and was given a severity score of 8.7/10 (high). Opswat says the bug allows unauthenticated attackers to obtain valid admin sessions without having a password, which would allow them to manage the device and even watch the stream.
The latter is tracked as CVE-2026-15316. With a severity score of 7.1/10 (high), this...
Copyright of this story solely belongs to www.techradar.com. To see the full text click HERE