Vercel Adds DBSC Protection Against Session Cookie Theft
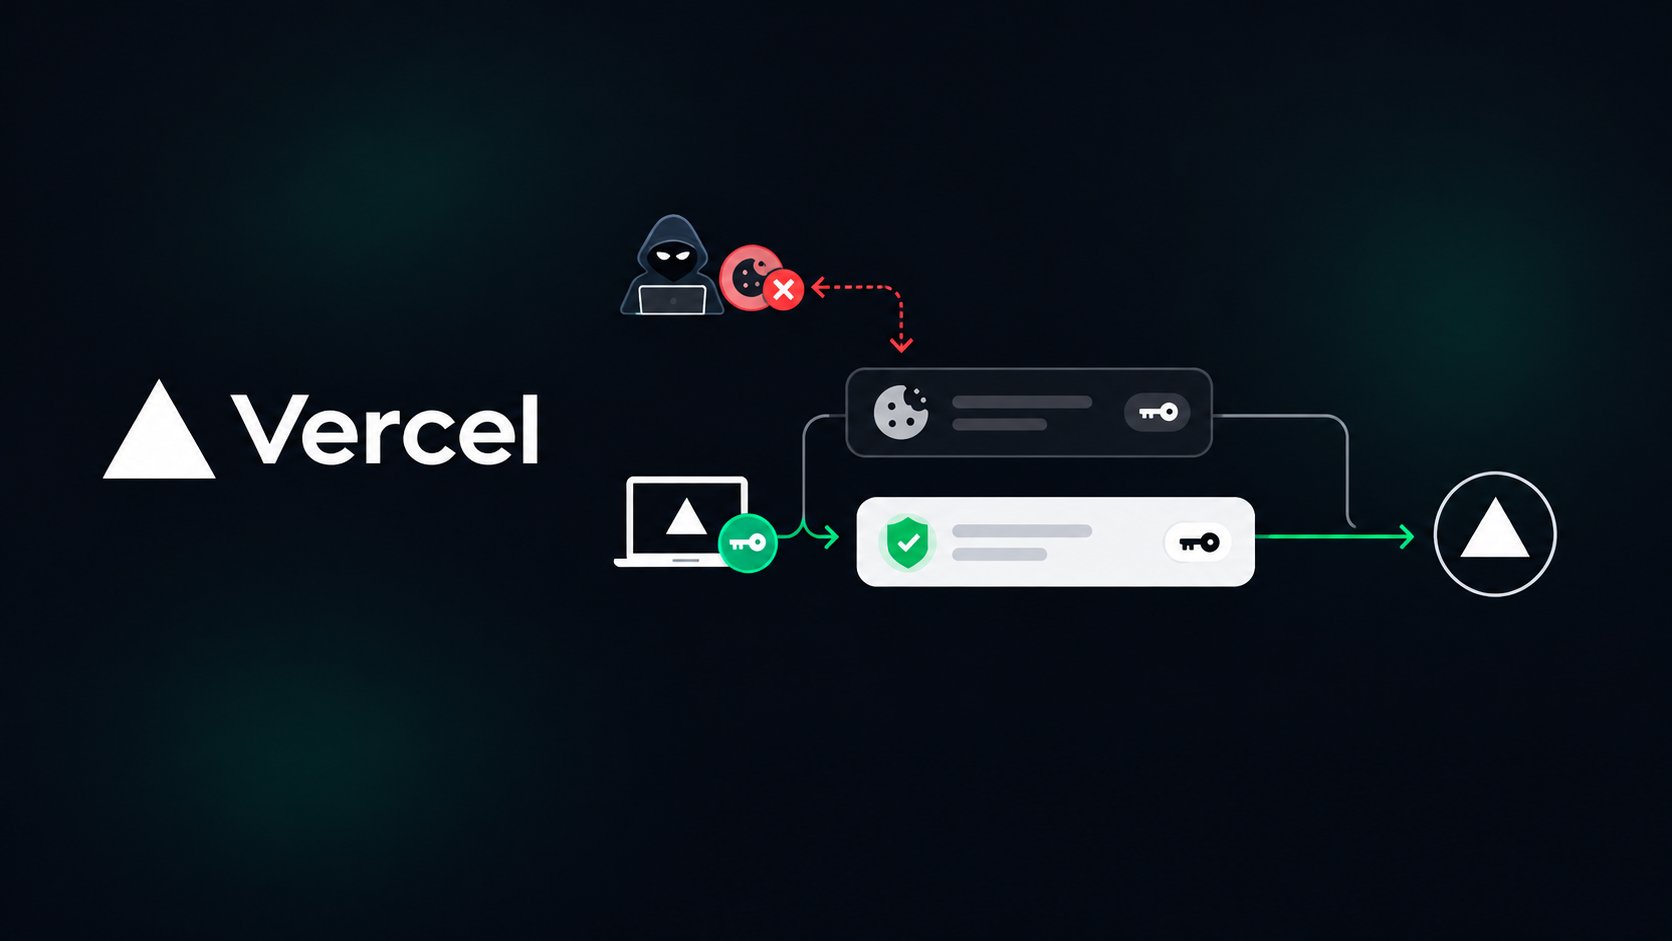
Stealing a session cookie can let hackers bypass passwords and multifactor authentication. Vercel wants to make that shortcut much harder to exploit.
Session cookies are credentials that let a website recognize a user is still authenticated, so the user doesn’t have to log in every time they revisit the site or take an action.
While convenient, it creates a security weakness: attackers can steal valid session cookies through infostealer malware and replay them from another device to impersonate their victims.
To help end that, Vercel is rolling out Device Bound Session Credentials (DBSC), a technology that ties authenticated browser sessions to cryptographic keys stored securely on the original device.
This means that even if attackers steal a session cookie, they ordinarily can’t reuse it on another device without also possessing the corresponding private key.
Vercel joins the fight against session-cookie theft
The development was announced on Tuesday, Nov. 3, in...
Copyright of this story solely belongs to www.techrepublic.com. To see the full text click HERE