US Disrupts Chinese State-Sponsored Hacking Tools
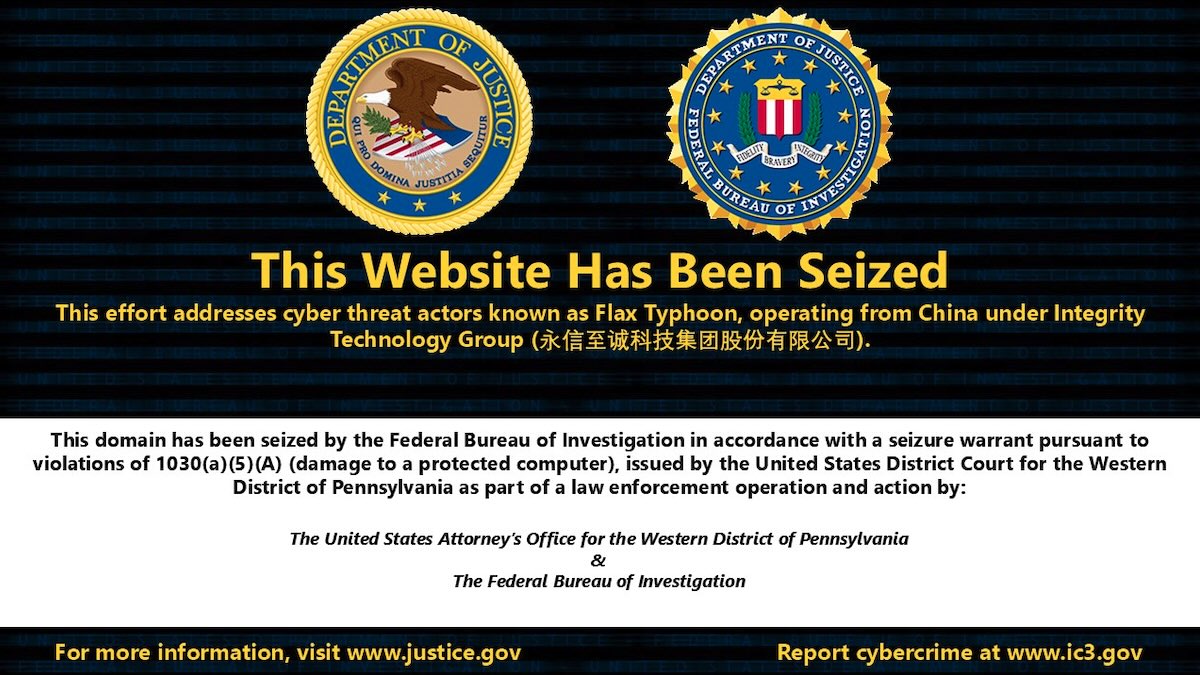
The United States on Thursday announced the disruption of two hacking tools used by Chinese state-sponsored threat actors in attacks against US and foreign critical infrastructure.
Built by Integrity Technology Group (Integrity Tech), MicroScan has been used for vulnerability scanning, while FishHub has enabled network intrusions via spear phishing.
Integrity Tech, the US says, used a Mirai malware variant to build an IoT botnet that facilitated MicroScan’s use for reconnaissance against victims’ networks, including a US power company, NGOs, Japanese and Polish airports, and Taiwanese critical infrastructure entities and universities.
FishHub enabled Integrity Tech’s clients to access victim networks remotely, search for specific files, and exfiltrate them. The tool has been used in attacks against at least 20 universities in Taiwan.
The US seized the domains the threat actors were using to access MicroScan and FishHub, including c0cc[.]cc, 98aicai[.]com, 98aicode[.]com, outlook3650[.]com, youtubecard[.]com, and linkedinns[.]net.
In 2024, the US disrupted Integrity...
Copyright of this story solely belongs to www.securityweek.com. To see the full text click HERE