Tracking 117MB of Data Exfiltration Across Two TLS Sessions
The Question
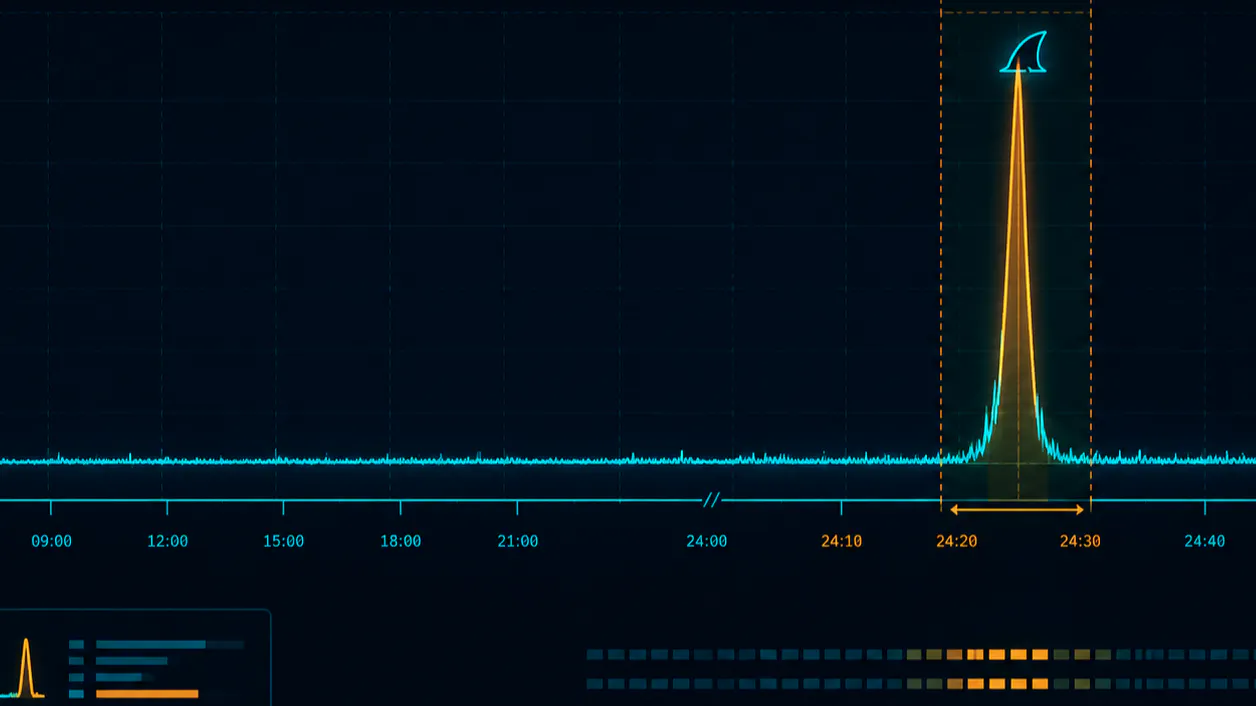
My last writeup ended with a confirmed finding: a TLS-wrapped tunnel to 178.62.245.11, alive for over a day, carrying an estimated 84MB out of a compromised host. tcpdump proved the tunnel existed. tshark answered the harder questions: how much data actually moved, when it moved — a steady drip, or a burst — and whether this was one continuous session or two.
tcpdump tells you a conversation exists. It doesn't tell you what's inside it, how it behaved over time, or whether "one tunnel" was really one tunnel. For that I used tshark as a three-stage chain: filter to isolate the traffic, extract to pull structured detail out of it, and stats to answer questions about volume and time. I ran the chain on a clean sample first to get the syntax right, then pointed the same commands at the real evidence. Here's what each stage does, and...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE