

The Sandbox Fights Back: Joe Security Launches Adaptive Detonation
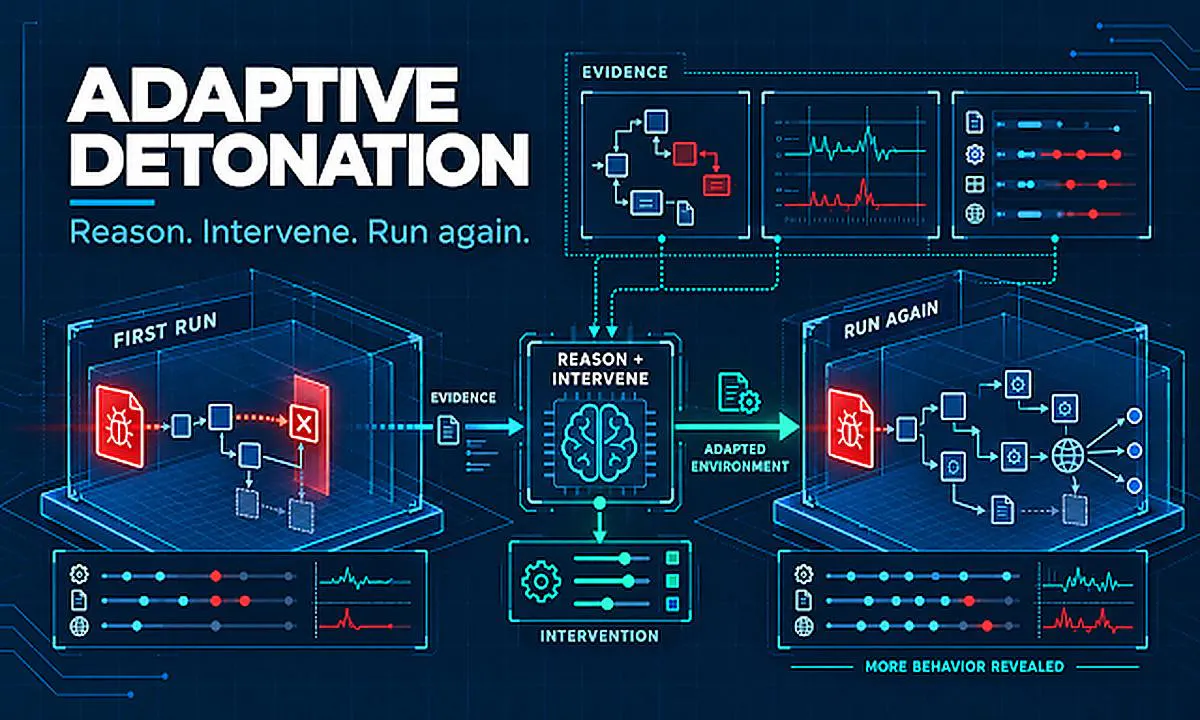
Reinach, Switzerland, November 4th, 2026/CyberNewswire/--Joe Security's Adaptive Detonation brings active intervention to malware analysis, helping security teams investigate threats that may conceal their behavior during an initial sandbox run.
Adaptive Detonation uses AI agents to examine execution results, identify obstacles preventing a sample from revealing relevant behavior, and select targeted interventions. These can include patching a blocking check, creating required files or settings, adjusting the execution environment, or supplying missing command-line arguments.
Joe Sandbox then analyzes the sample again under the modified conditions to verify whether the intervention reveals additional activity.
The approach addresses obstacles including keyboard restrictions, timing checks, firmware-based rejection, date requirements, and missing dependencies. By connecting observed evidence with targeted action and verification, Adaptive Detonation helps analysts investigate why a sample remains inactive and uncover behavior that might otherwise stay hidden.
For security teams, this means deeper visibility into evasive threats and more evidence to...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE
