StealC Malware Returns as Stadia RAT After Operation Endgame Takedown
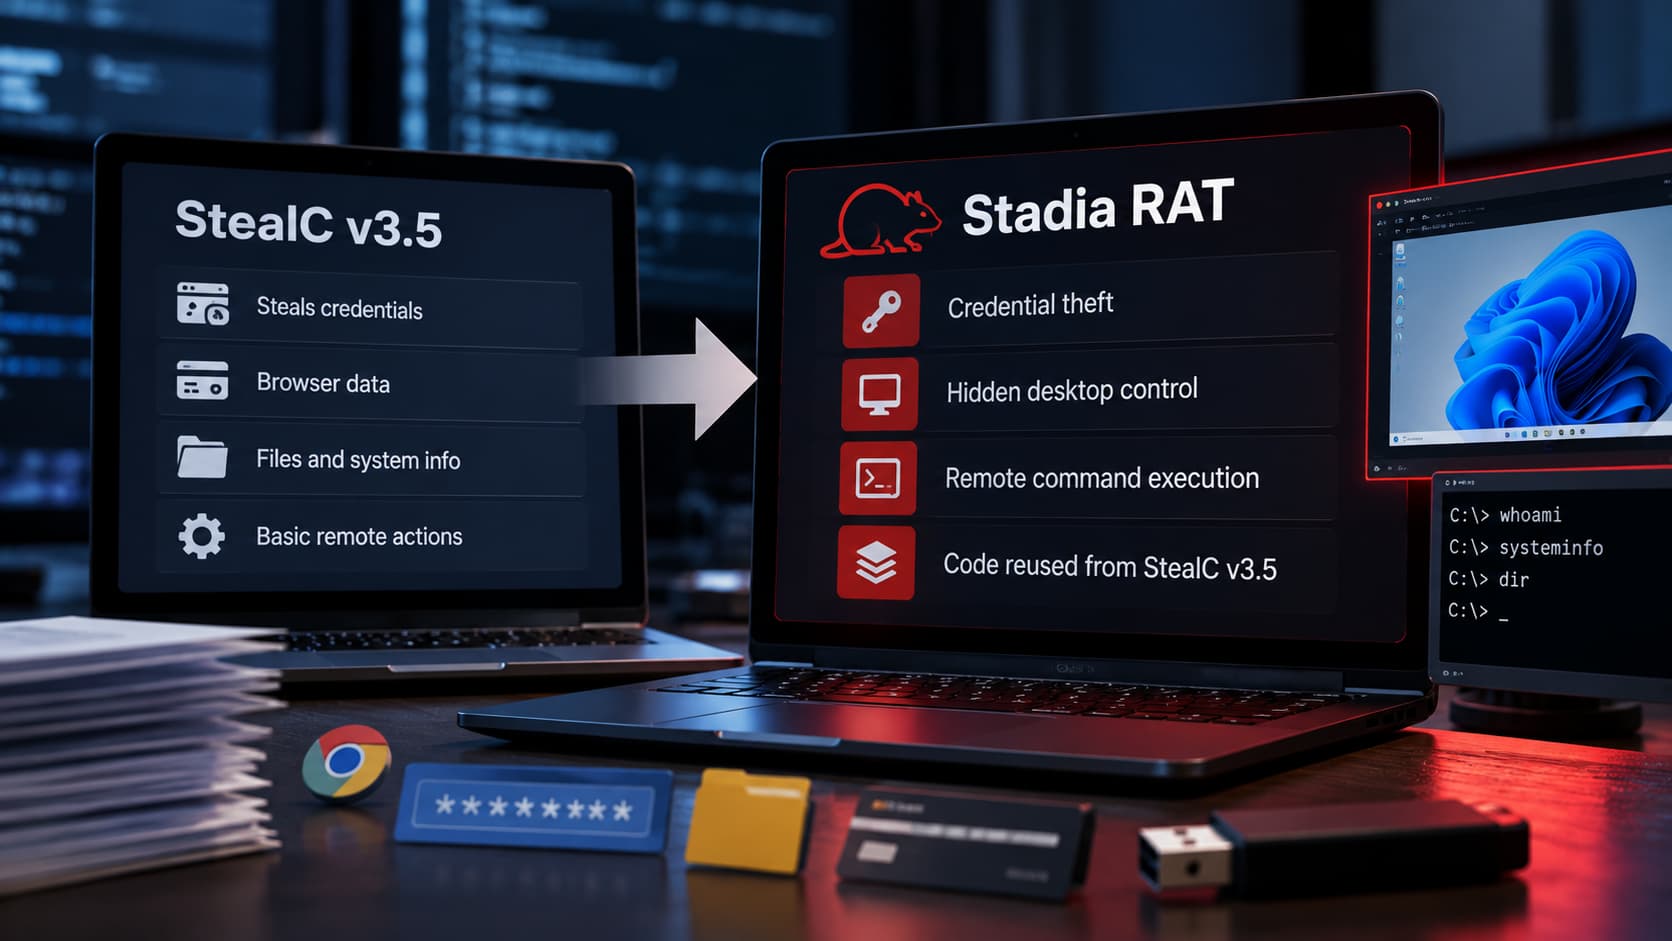
StealC’s seller has returned with Stadia RAT, combining credential theft, hidden desktop control, and remote command execution using code reused from StealC v3.5.
Four months after Europol disrupted StealC during Operation Endgame, its seller has returned with Stadia, a new remote access trojan (RAT) that combines credential theft with remote control of Windows systems.
Hackread.com previously reported on StealC’s use in a FileFix phishing campaign in 2025. New research from cybersecurity firm Varonis shared with Hackread.com shows that Stadia reuses code from StealC v3.5 while adding capabilities beyond information theft.
In June 2026, Operation Endgame disrupted StealC and other malware networks. The operation involved 326 servers and 142 domains, while authorities recovered more than 25 million stolen credentials from 385,000 infected machines.
Stadia RAT Expands Beyond Credential Theft
Advertised on October 16, Stadia offers six modules: a stealer, hidden virtual network computing (HVNC), Remote CMD, a loader, File Explorer...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE