SPECTER Attack Uses USB Power Signals to Leak Data From Air-Gapped PCs
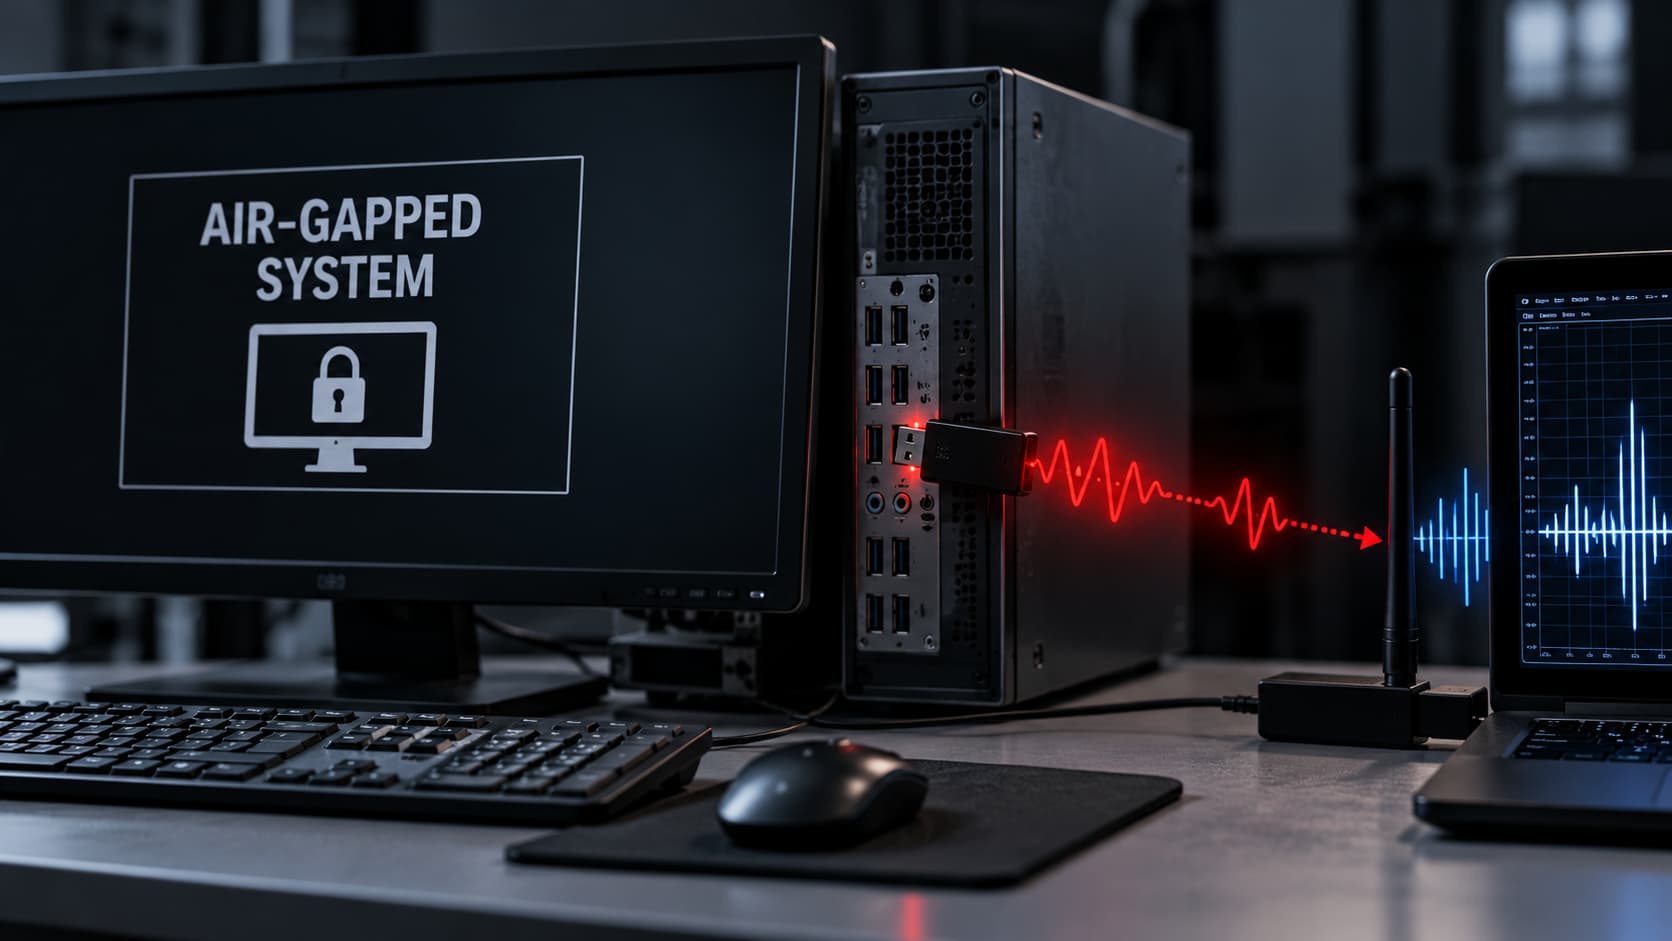
Cybersecurity researchers have demonstrated a covert channel that could allow malware to extract sensitive information from air-gapped computers by manipulating USB power-management settings and observing the resulting signals.
AuditSecurity
Called SPECTER, the technique was developed by Hyeongjun Choi, Ji Hyuk Jung, and Ji Won Yoon of Korea University in Seoul, South Korea. Their research explores how routine USB control operations can transmit information even when conventional network connections are unavailable.
Turning USB Control Operations Into Signals
Air-gapped systems are physically isolated from external networks to reduce the risk of unauthorized data transfers. However, if an attacker compromises a machine, alternative communication paths may still be available.
SPECTER requires malware to have root or administrator privileges on the compromised host. It encodes information through USB power-management or device-state operations without placing the payload in USB data transfers. The technique involves modifications to peripheral hardware or firmware.
Three Ways to Recover Data
...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE