Securing Inherited AI: Models, Runtimes, and Tools Inside Vendor Software
Every once in a while, a research report drops a number so specific and so telling that it just parks itself in your head for weeks. Wiz did that to me back in April with their State of AI in the Cloud 2026 report, and I've been meaning to write about it ever since.
The line is buried on page whatever, under a heading about self-hosted models. 68% of organizations running self-hosted AI ingest those models through third-party software.
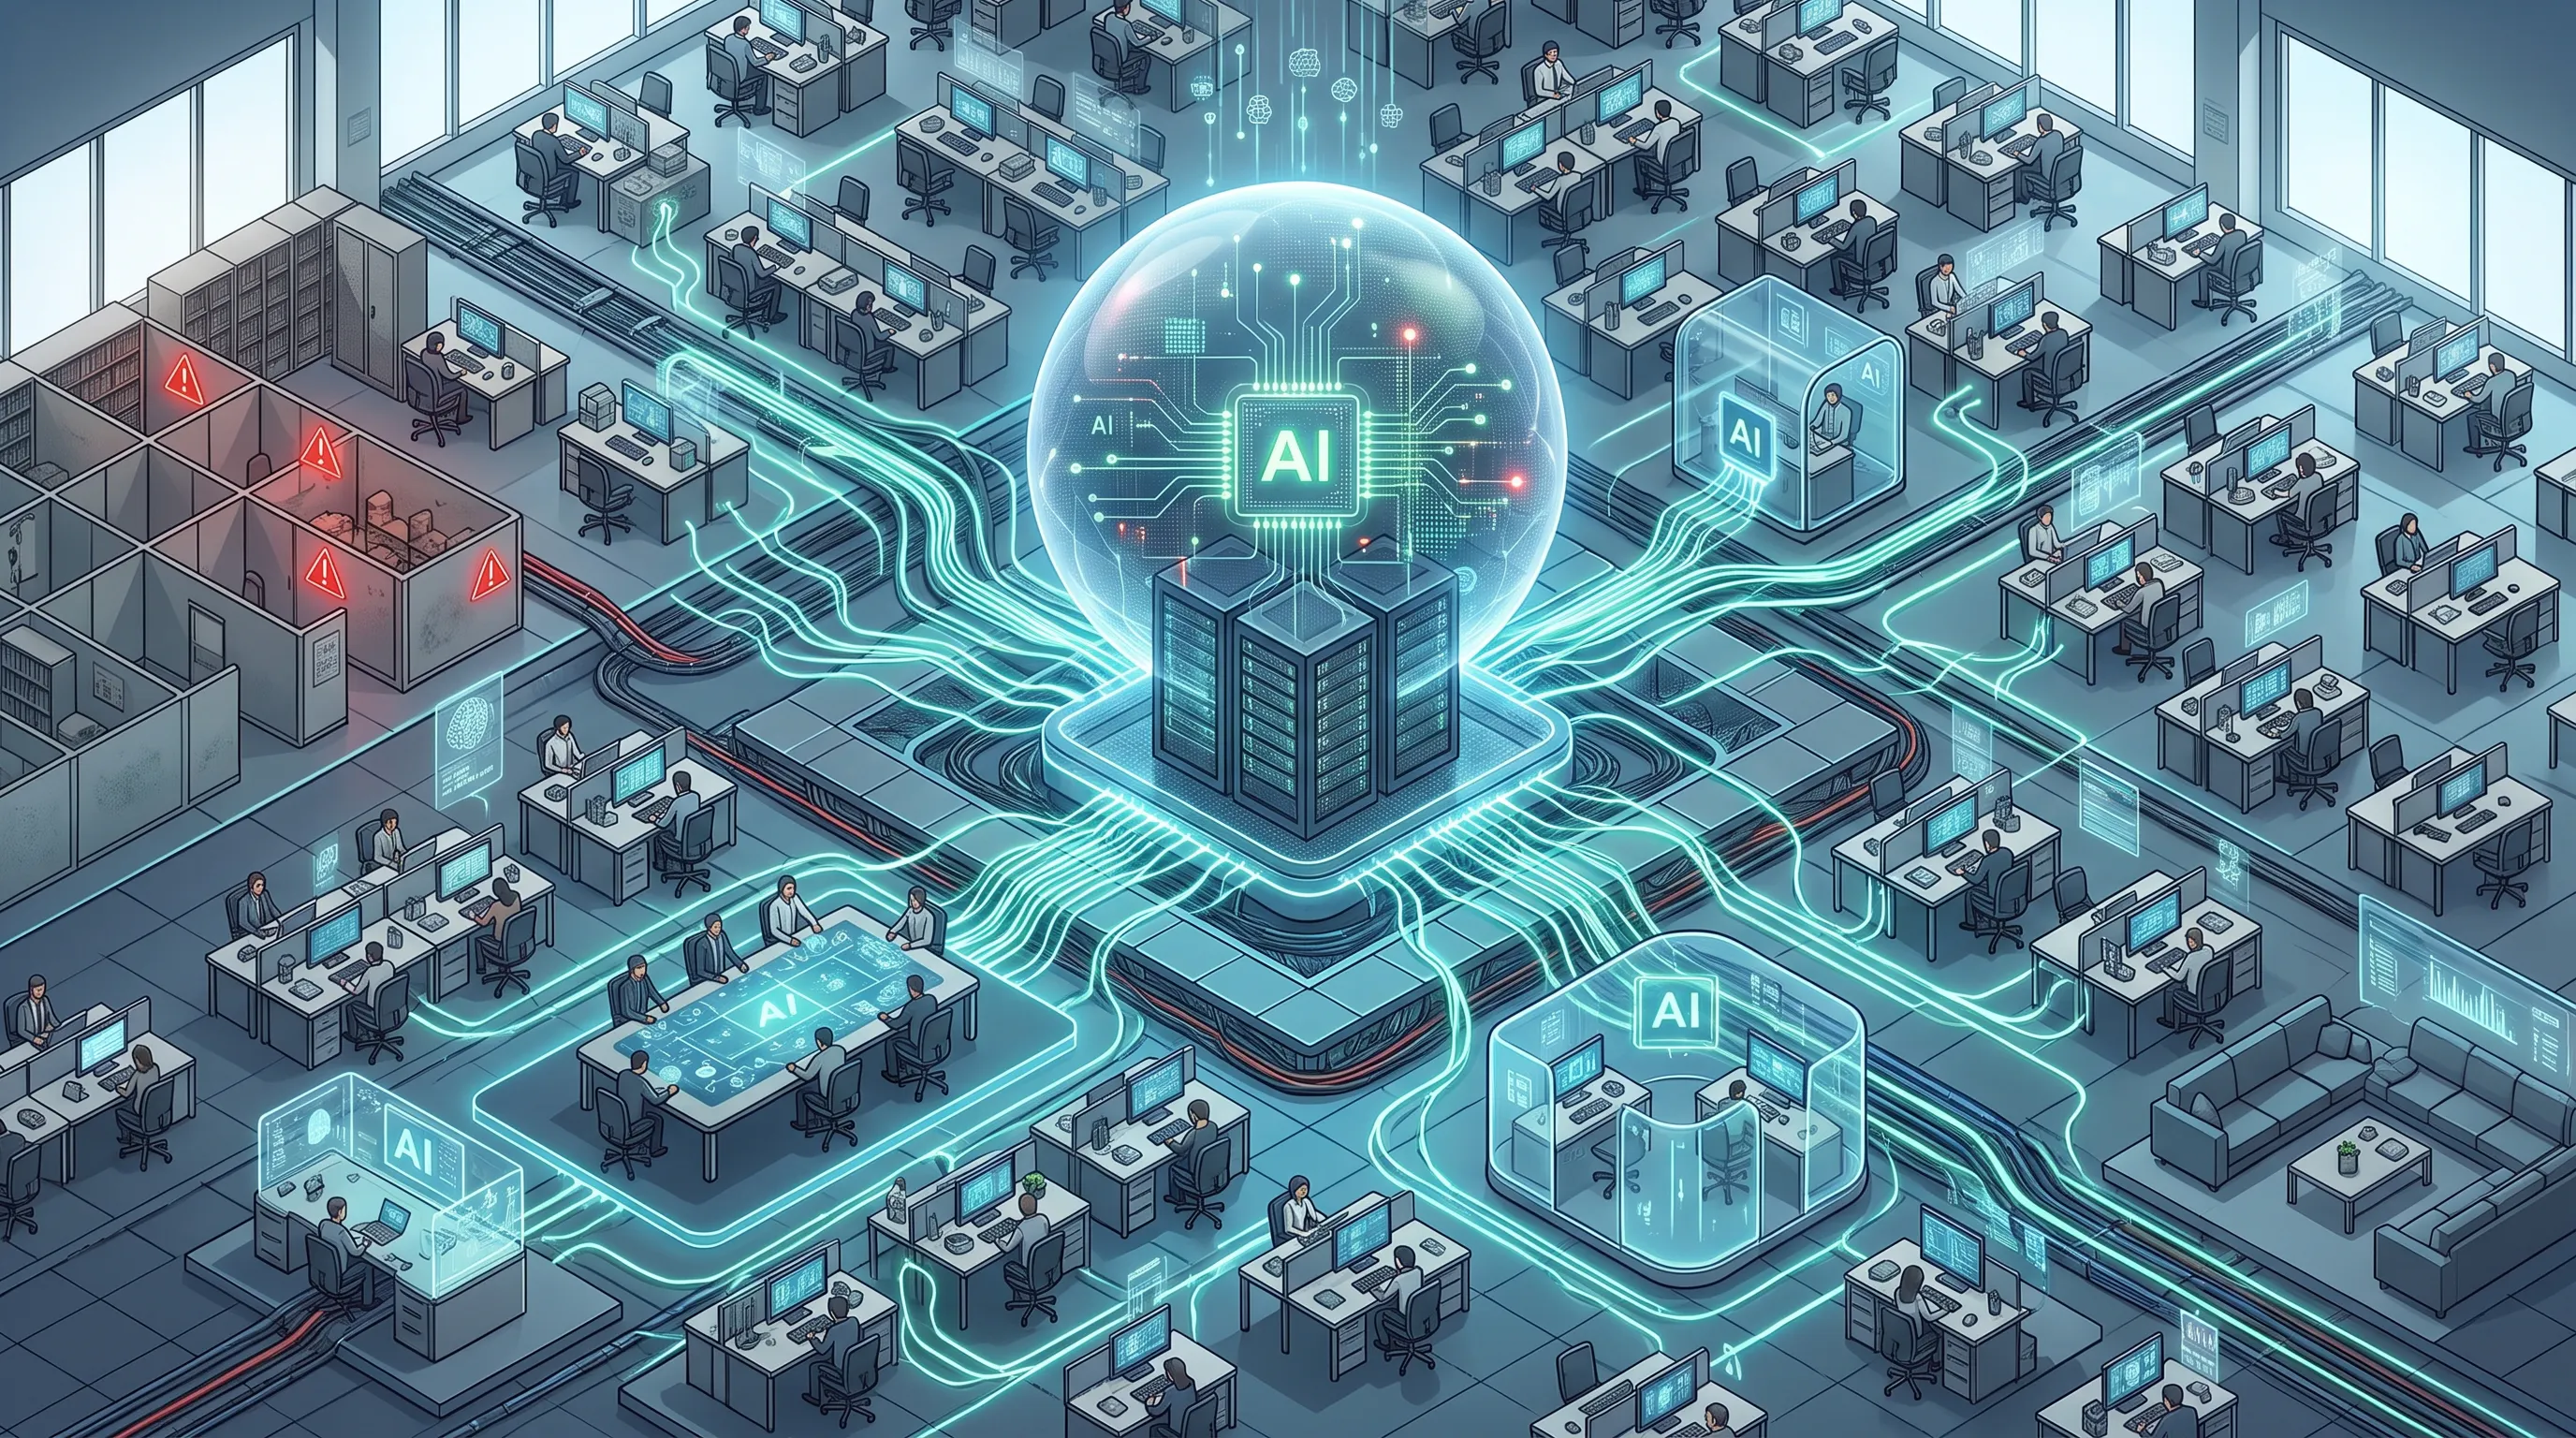
That's a mouthful, so let me translate. Two out of three companies with AI models running on their own infrastructure didn't actually decide to run those models. Some vendor product they bought (a knowledge tool, a code assistant, a support router, whatever) quietly shipped a model inside, and the security team never signed off on it because nobody knew there was anything to sign off on.
If you've ever done a...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE