RatHat Android Malware Uses AI to Target Banking Credentials in Real Time
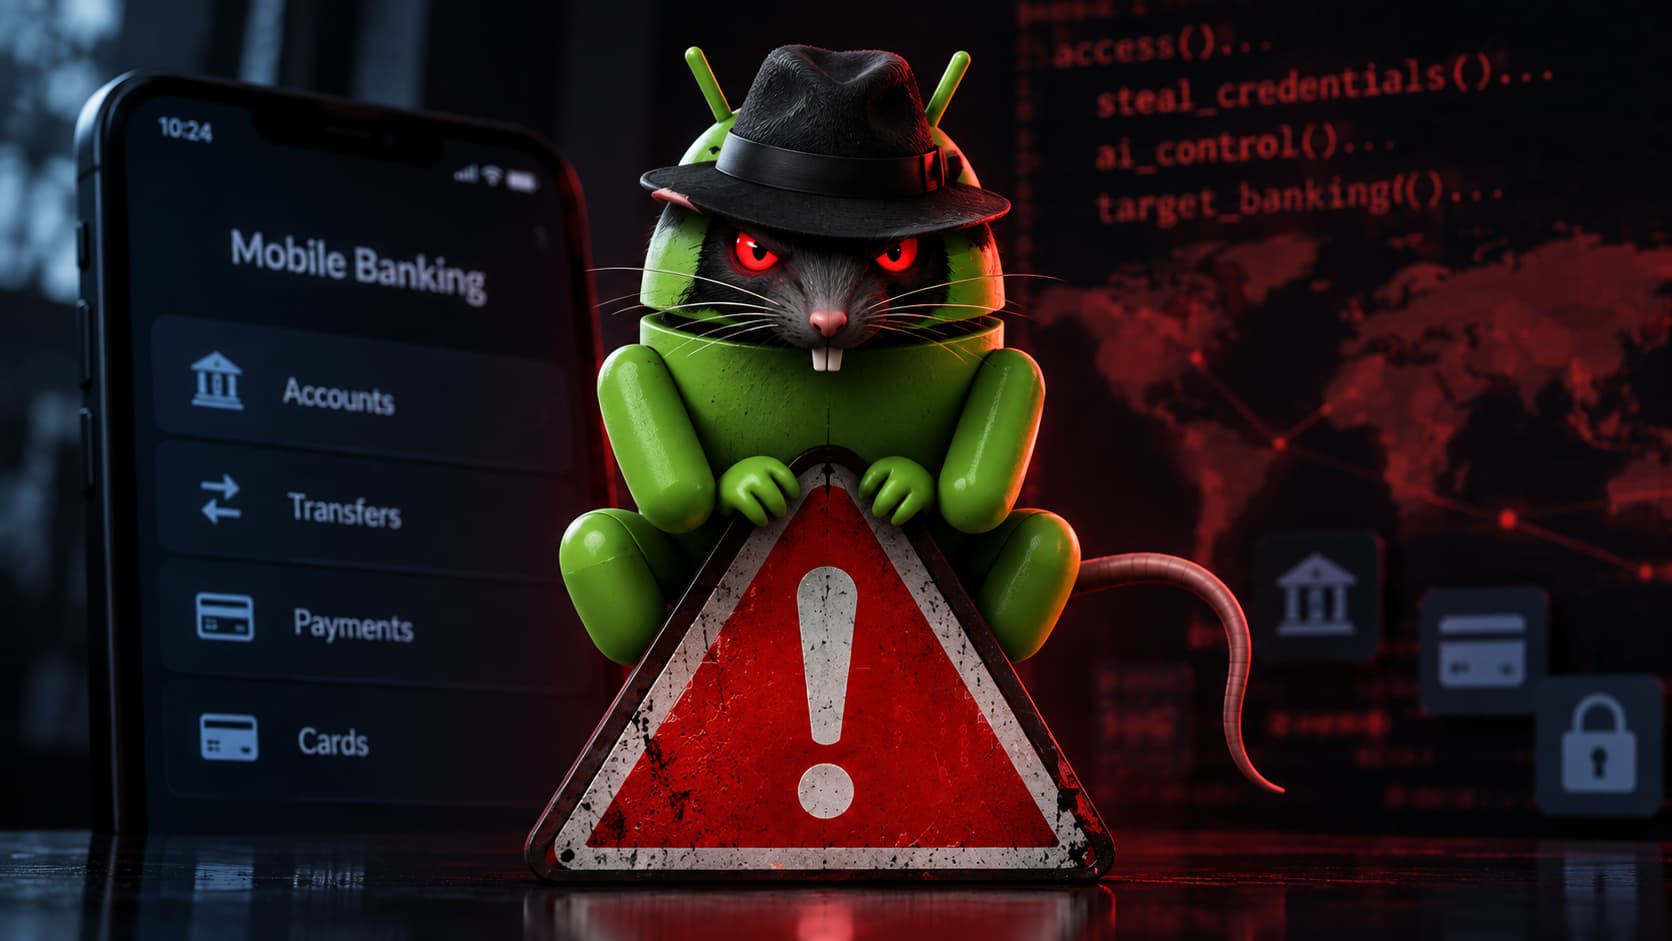
A newly discovered Android malware strain named RatHat uses generative AI to navigate and control infected devices in real time. Mobile security firm Zimperium identified the threat, sharing its research with Hackread.com. zLabs links RatHat to threat actors that appear to be operating in China.
Unlike traditional mobile threats that rely on fixed scripts, RatHat serializes the device’s live Accessibility tree into XML and sends it to a generative AI assistant. The AI can return screen coordinates, identify on-screen text and provide navigation commands such as scrolling.
Zimperium says RatHat also uses WebView-based HTML overlays that appear over targeted banking and crypto apps, presenting fake interfaces designed to capture users’ login credentials. The malware can also target payment apps such as WeChat and Alipay with deceptive overlays to steal PINs, while an SMS receiver and notification listener can intercept OTP and 2FA codes.
Multi-Layer Stealth and System Access
RatHat...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE