PortSwigger Said Chrome Updates Broke Its CSRF Lab. My Tests Tell a Different Story
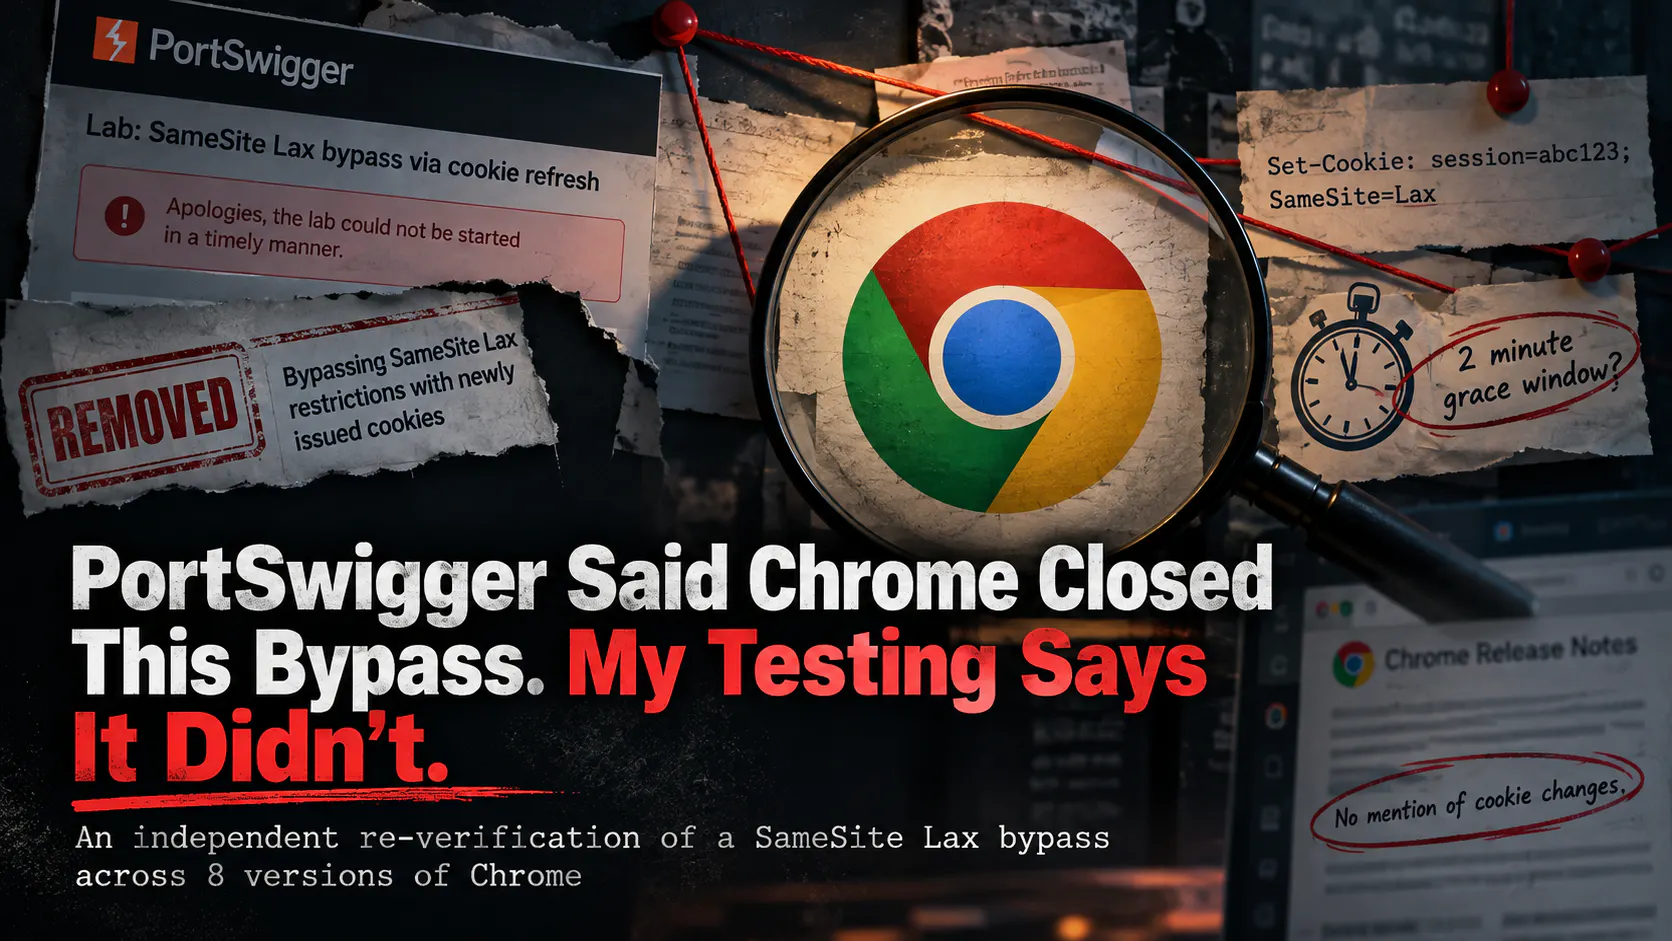
TL;DR: On August 11, 2026, I was one lab away from finishing PortSwigger’s CSRF module when the final lab, “SameSite Lax bypass via cookie refresh,” refused to start. PortSwigger support told me recent Chrome updates to the victim browser had broken it, and within 24 hours, they had quietly removed both the lab and the theory section titled “Bypassing SameSite Lax restrictions with newly issued cookies,” from the Academy entirely. I accepted that explanation for a while. Then, weeks later, I went looking for any public record of Chrome actually removing this two-minute grace window, and found nothing. So I built a two-site Python proof-of-concept and tested it across 8 Chrome versionsto find out for myself whether the bypass still exists.
Short answer: it does.
While I was working my way through PortSwigger’s Web Security Academy, I reached the CSRF section. On August 11, I was almost done...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE