nDiligence Releases Four-Year Study Identifying a Critical Supply-Chain Vulnerability Across 50 Platform Types
San Francisco, California, USA, November 12th, 2026, CyberNewswire
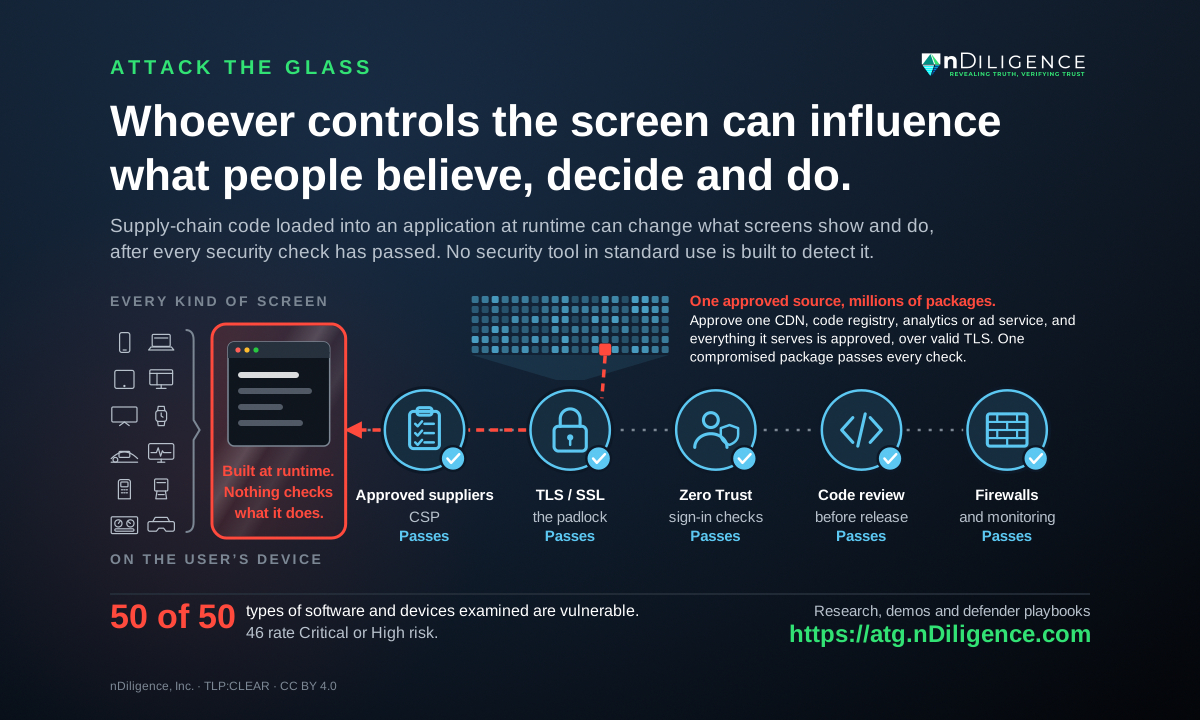
Four-year cybersecurity study finds all 50 types of software and devices examined vulnerable, with 46 rated Critical or High risk.
nDiligence, Inc. today announced the release of Attack the Glass (ATG) research to the general public. The four-year study examines a cybersecurity vulnerability in how applications use people’s own devices to build what appears on screen, load data and run code while the application is in use. An attacker who exploits it can change what people see and what their software does, after every security check has passed. The research is free at https://atg.nDiligence.com.
StudySecurity
Much of the software people rely on, from web browsers and mobile apps to vehicle displays, medical devices and industrial control screens, builds its user interface on the device while it is running, a process called runtime client-side rendering. The code, data and media it assembles...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE