Microsoft Seizes YAM Store and Phishing Kit Domains Linked to 1B Malicious Messages
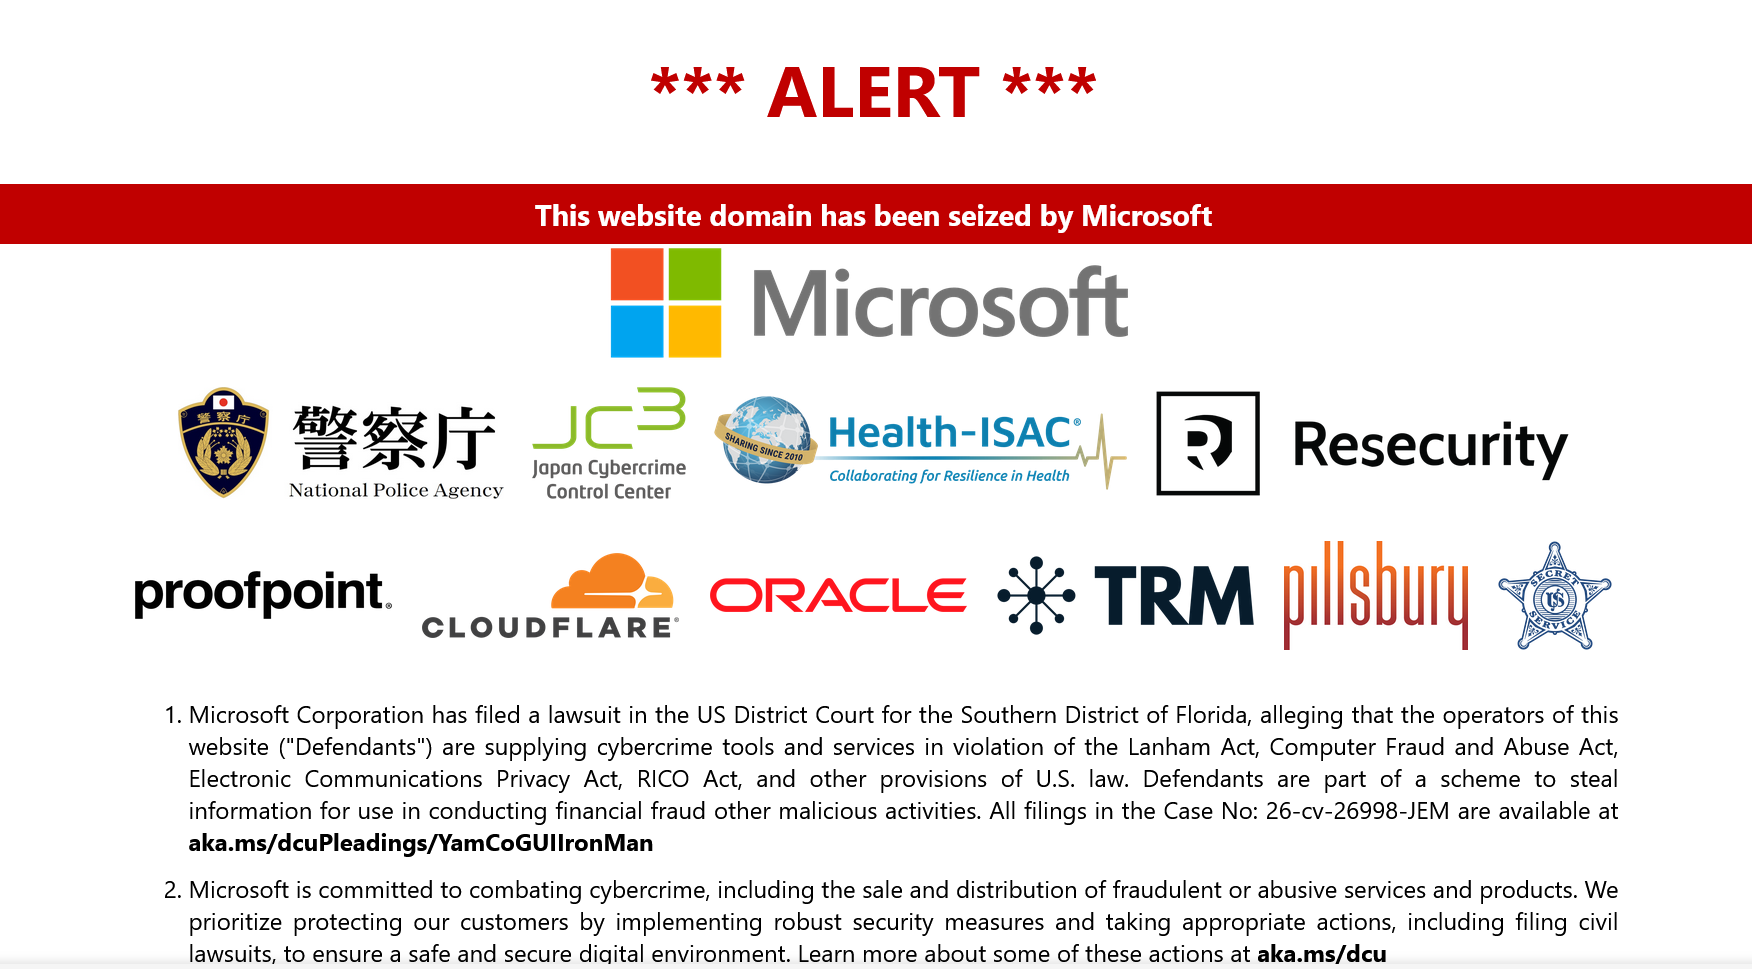
Microsoft and Health-ISAC seize domains linked to YAM Store, CoGUI and Iron Man, services that enabled over 1 billion malicious messages since January 2026.
Microsoft and the Health Information Sharing and Analysis Center (Health-ISAC) have seized and redirected internet domains supporting a Chinese-language cybercrime marketplace that supplied cybercriminals with fraudulent accounts, phishing kits and infrastructure.
The court-authorized operation targets three components of the network: YAM Store, CoGUI and Iron Man. Since January 2026, the services have collectively enabled more than one billion malicious messages targeting over 75,000 organizations worldwide, including more than 750 million messages targeting Microsoft customers. The campaigns have affected consumers and organizations in over 150 countries.
Marketplace Supplies Accounts and Phishing Tools
The investigation began in late 2025 after Japan’s National Police Agency (NPA) alerted Microsoft to malicious messaging campaigns targeting people in Japan. Investigators traced the activity to an interconnected marketplace supplying tools and services...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE