Microsoft Disrupts AI-Powered EvilTokens Service Linked to 12,000 Hacked Inboxes
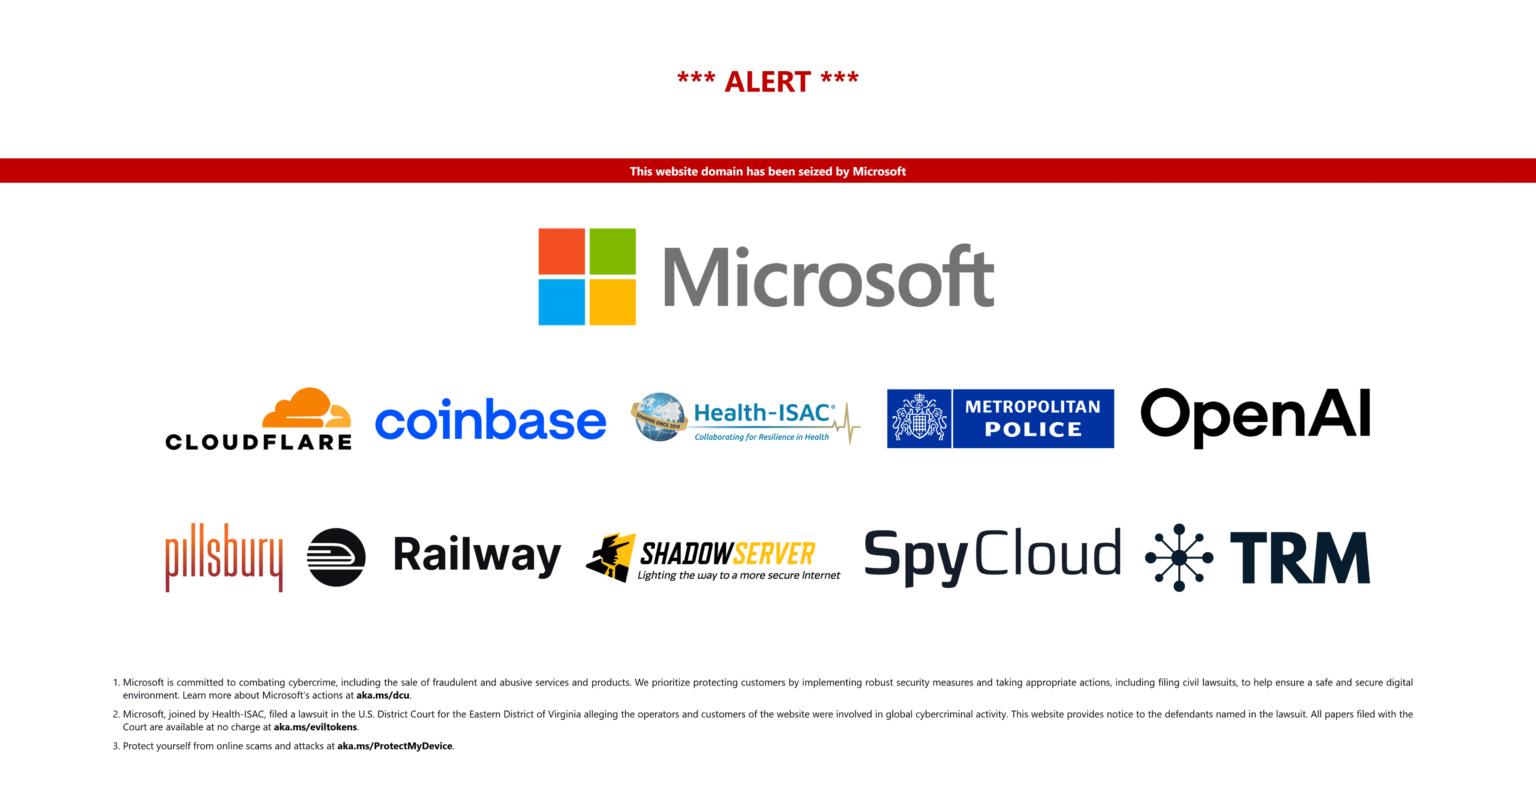
Microsoft has disrupted EvilTokens, an AI-powered phishing-as-a-service platform linked to the compromise of more than 12,000 email inboxes across over 10,000 organisations worldwide since February 2026.
The coordinated operation resulted in the seizure of 50 websites used to operate EvilTokens and the disabling of more than 150 additional domains supporting the service. Authorities also arrested two men in the United Kingdom in connection with the alleged operation.
According to Microsoft’s Digital Crimes Unit, the operation was authorised by the US District Court for the Eastern District of Virginia. Health-ISAC also joined Microsoft’s legal case as a co-plaintiff because healthcare organisations were among the targets.
Microsoft worked with Cloudflare, Coinbase, OpenAI, Railway, SpyCloud, the Shadowserver Foundation and TRM Labs to identify and disable infrastructure supporting EvilTokens. The company also contacted affected customers and helped them secure compromised accounts.
Two Men Arrested in the UK
Officers from the Metropolitan Police...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE