Inspecting Multi-Platform Docker Images, SBOMs, and SLSA Provenance With Buildx
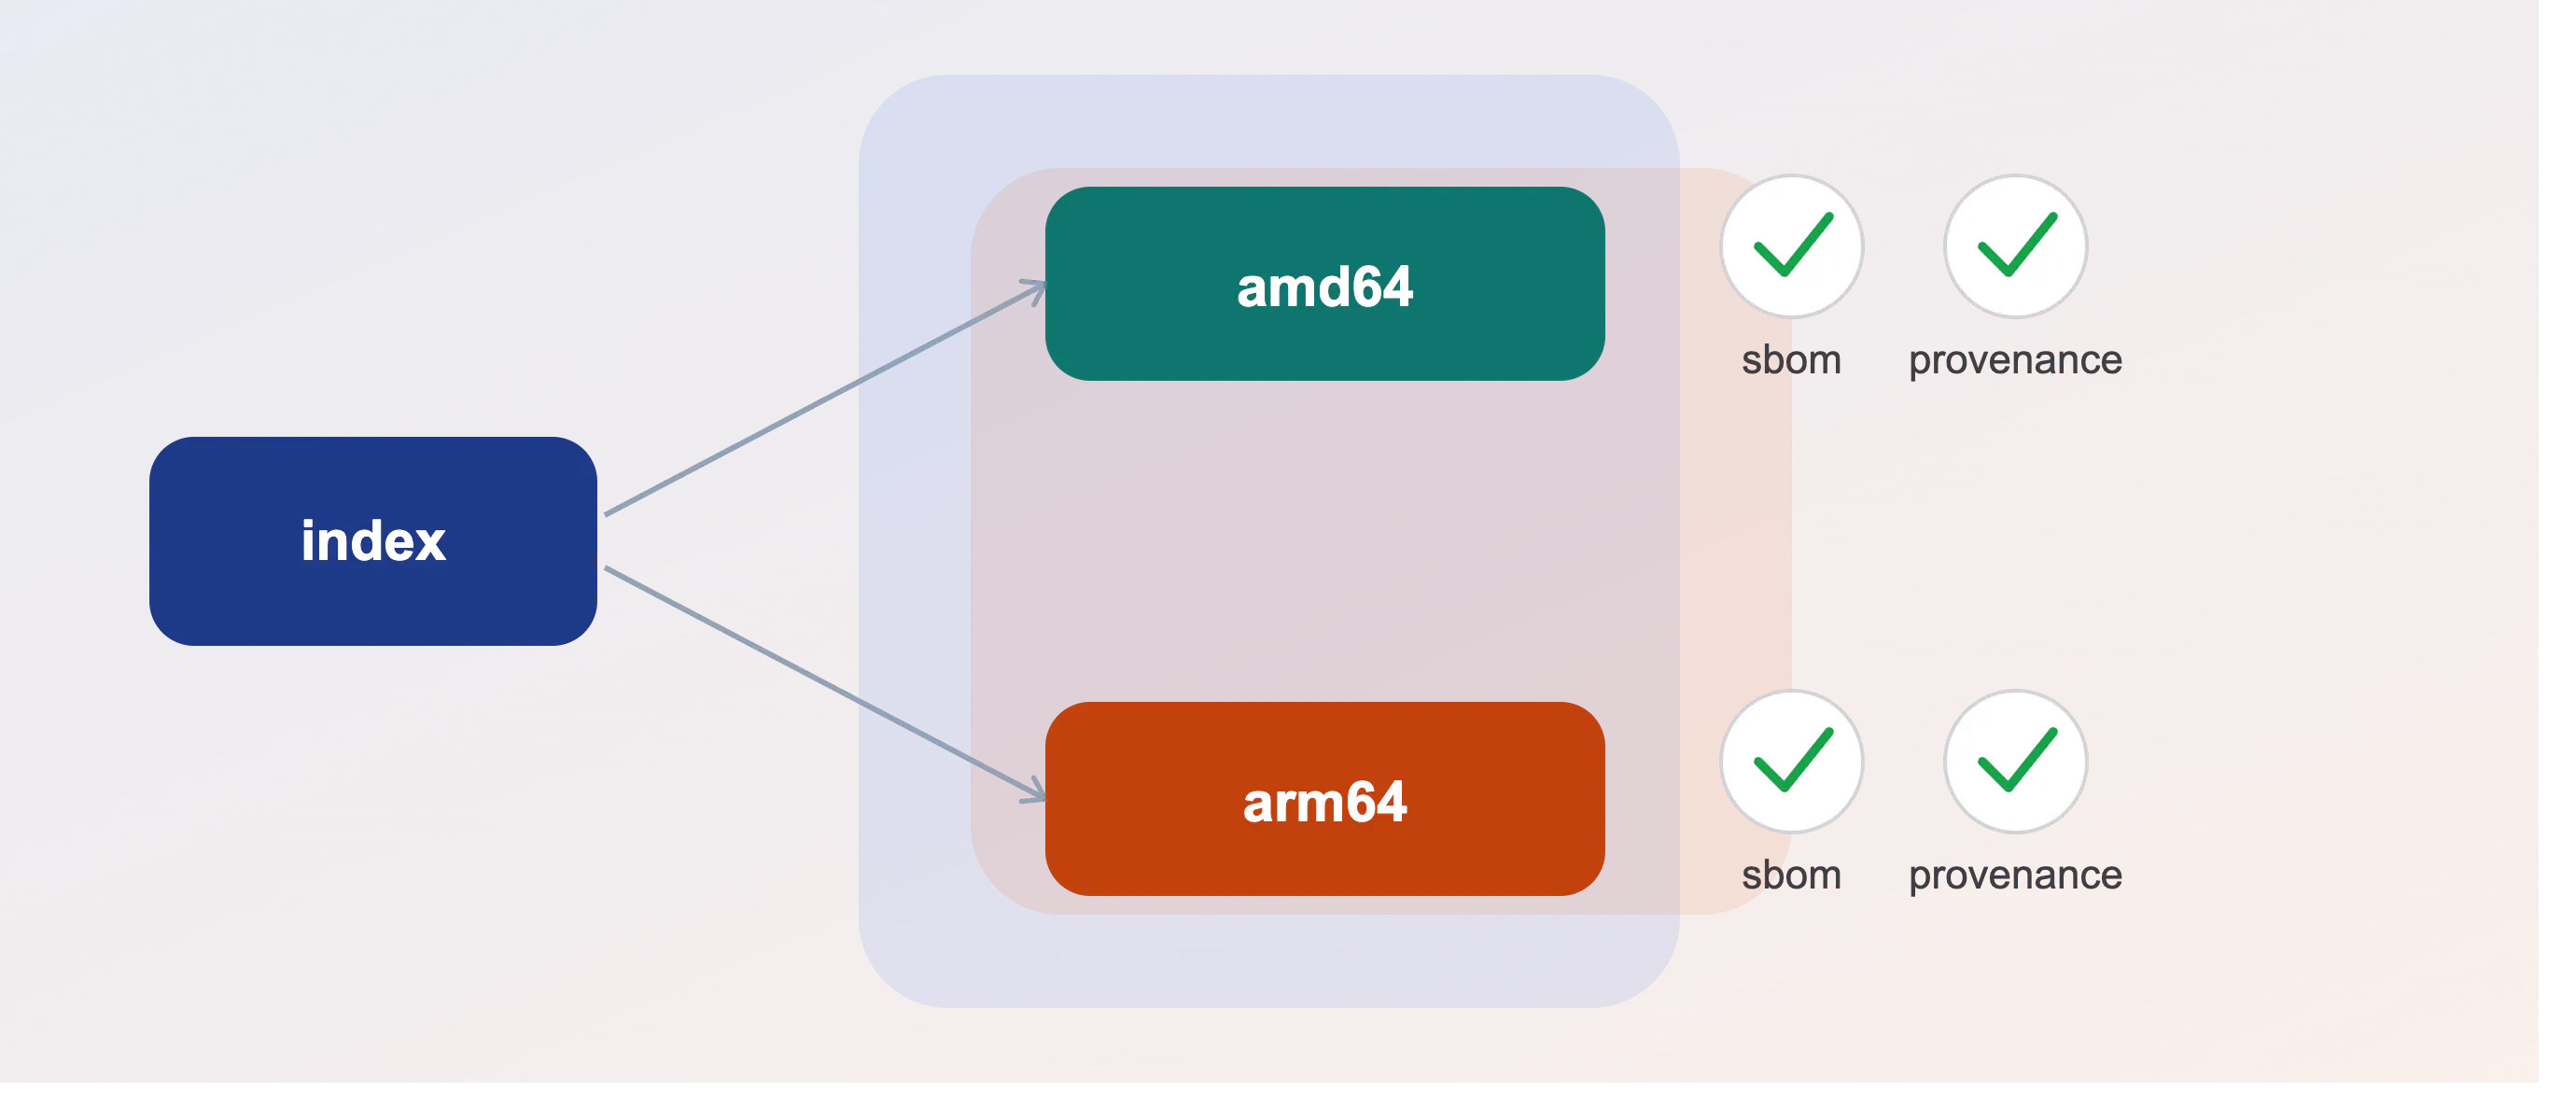
An image tag is convenient for deployment, but it does not tell me which architectures are inside the image or what went into building them. For a small Go service, I used Docker Buildx to publish an image for linux/amd64 and linux/arm64, attaching a software bill of materials (SBOM) and build provenance to each platform. Then I inspected the result in the registry. I wanted to answer a concrete question: if a build says it produced an SBOM and provenance, what can I verify from the image that was actually published?
The example repository contains a small HTTP service, a multi-stage Dockerfile, and a docker-bake.hcl file. The Dockerfile builds a Go binary for the requested target architecture and copies it into an Alpine runtime image. The Bake configuration defines both target platforms and requests SBOM and minimal provenance attestations:
target "image" { context = "." dockerfile = "Dockerfile" tags =...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE