How I Cut Manual Infrastructure Security Reviews by 80% with Checkov and GitLab CI
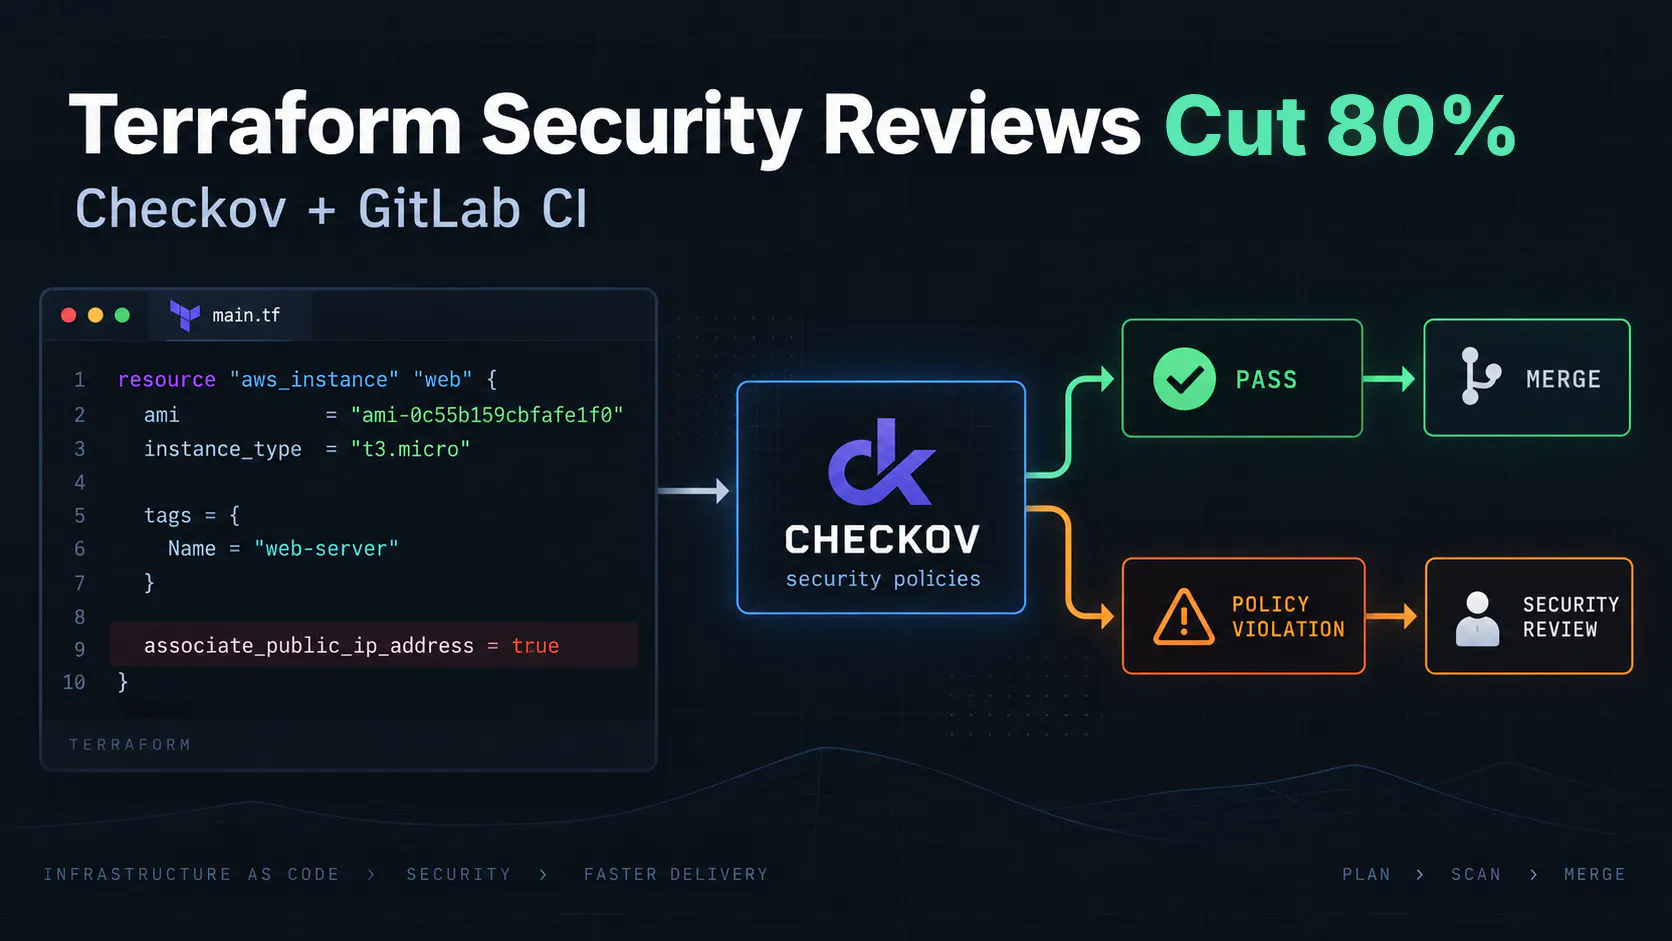
Infrastructure as Code makes infrastructure changes reproducible, reviewable and auditable. It does not make them secure.
A perfectly valid Terraform configuration can still expose a database to the Internet, create an unencrypted disk, grant excessive IAM permissions or attach a public IP address to a workload that should never be publicly reachable. Terraform will apply all of it without complaining, because that is exactly what I told it to do. But that was not even the part that hurt most.
Our infrastructure was managed through Terraform and GitLab CI. Security engineers could review infrastructure changes, and for a while they did. Adding them as mandatory approvers on every Merge Request did not scale, and most of what reached them was not interesting: a tag, an instance size, a new output variable.
Changing a harmless tag should not require the same security review as opening a firewall rule to 0.0.0.0/0.
So...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE