How AI coding tools could amplify software supply-chain attacks
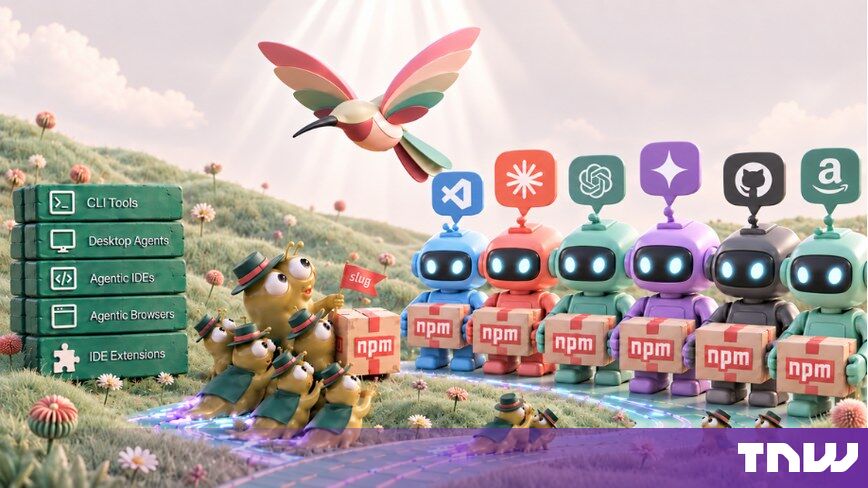
AI coding tools are changing how developers obtain and use software. But the growing volume of automated package installations is creating new challenges for enterprise security teams. A vulnerability uncovered by Bloom Security demonstrates how weaknesses in software publishing infrastructure can intersect with these automated workflows. It could potentially expose organizations to malicious code without requiring attackers to steal credentials.
The research, named SlugFest, identified more than 1,500 npm packages vulnerable to a publishing attack involving GitHub repository addresses. Together, the packages had accumulated more than 10 million downloads.
Bloom also measured the scale of AI-driven software installation across large enterprises. It found that a typical endpoint receives approximately 70 packages installed by AI agents each month. Developer machines can approach 350.
The findings raise questions about how organizations should manage software dependencies. AI agents increasingly select, install, and execute code on their behalf.
A New Layer of Enterprise Exposure
...
Copyright of this story solely belongs to thenextweb.com. To see the full text click HERE