Hackers Use 4,837 Stolen GitHub Accounts to Target 61,764 Repositories
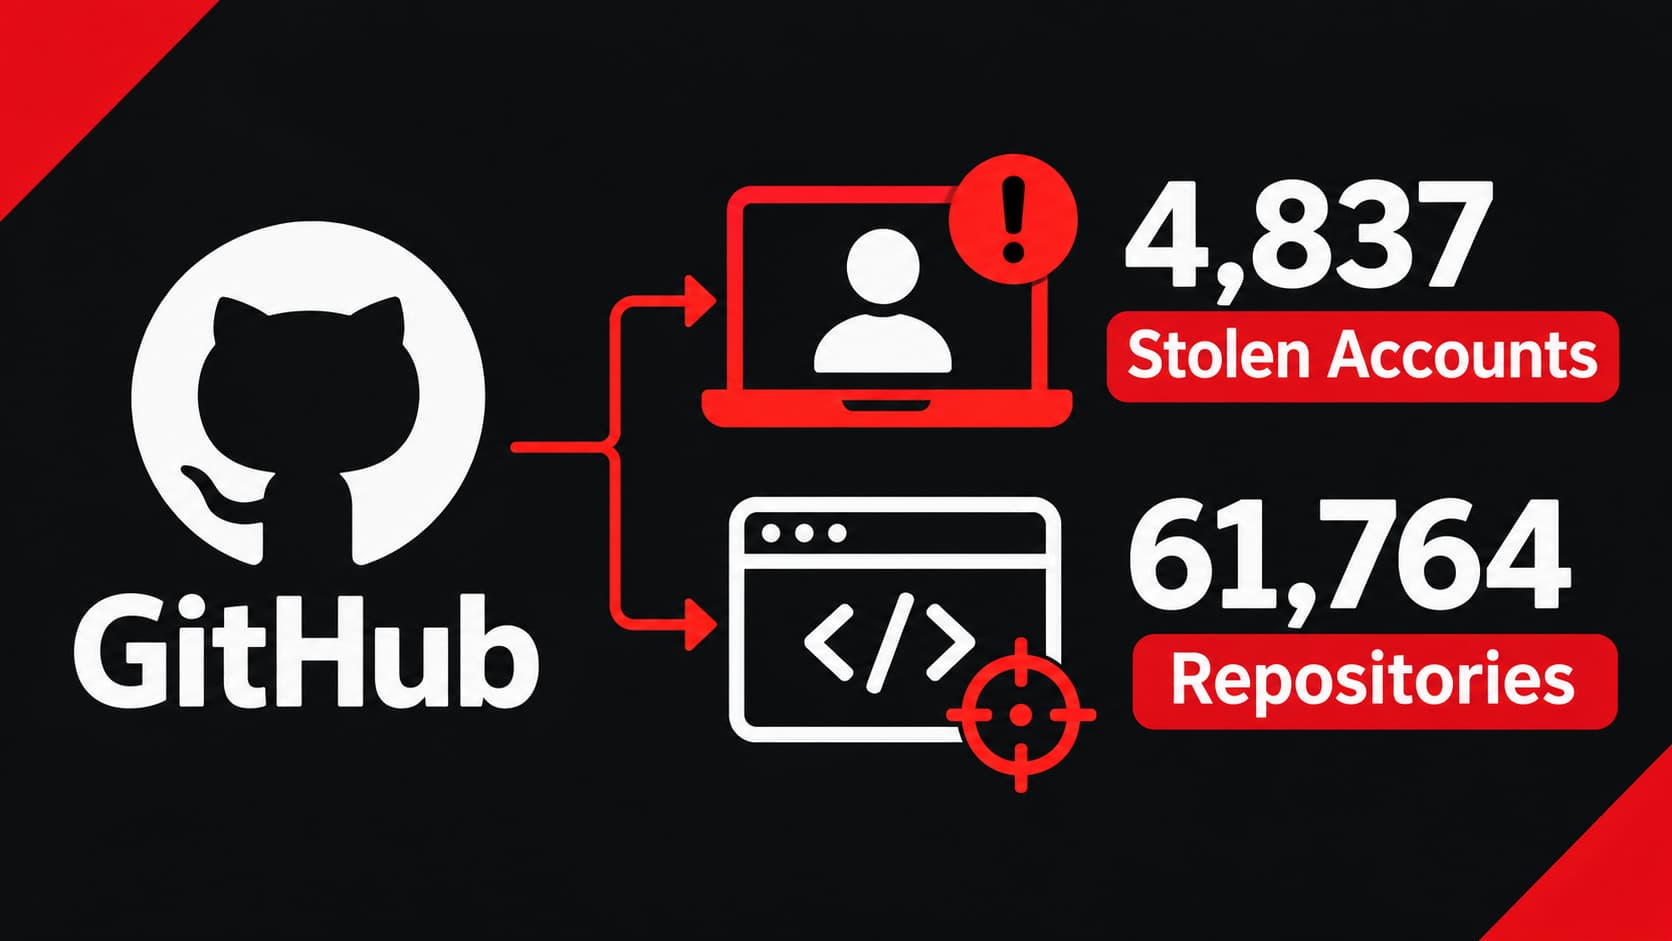
Hackers used 4,837 compromised GitHub accounts in the wfx-loot campaign to target repositories and steal developer credentials, cloud keys and tokens.
Hackers have used thousands of compromised GitHub accounts to target public repositories with credential-stealing code, with researchers confirming that the malware ran and stole secrets from at least 1,835 repositories.
Aikido Security identified the campaign as wfx-loot. Its initial findings counted 4,837 compromised accounts opening probe pull requests across 61,764 repositories. Subsequent research documented continued activity, changes to the malware and the exposure of some GitHub tokens through applications deployed on Fly.io.
The targeted-repository count does not mean every repository ran the malware. Many received only a probe, while execution depended on the stolen account’s permissions and the repository’s configuration.
Routine-looking pull requests tested stolen access
According to Aikido researcher Oliver Smith, the campaign began on November 10. Attackers opened pull requests titled docs: dependency audit notes from...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE