Hackers Exploit Decade-Old OpenSSH Flaw to Bypass Linux Logins
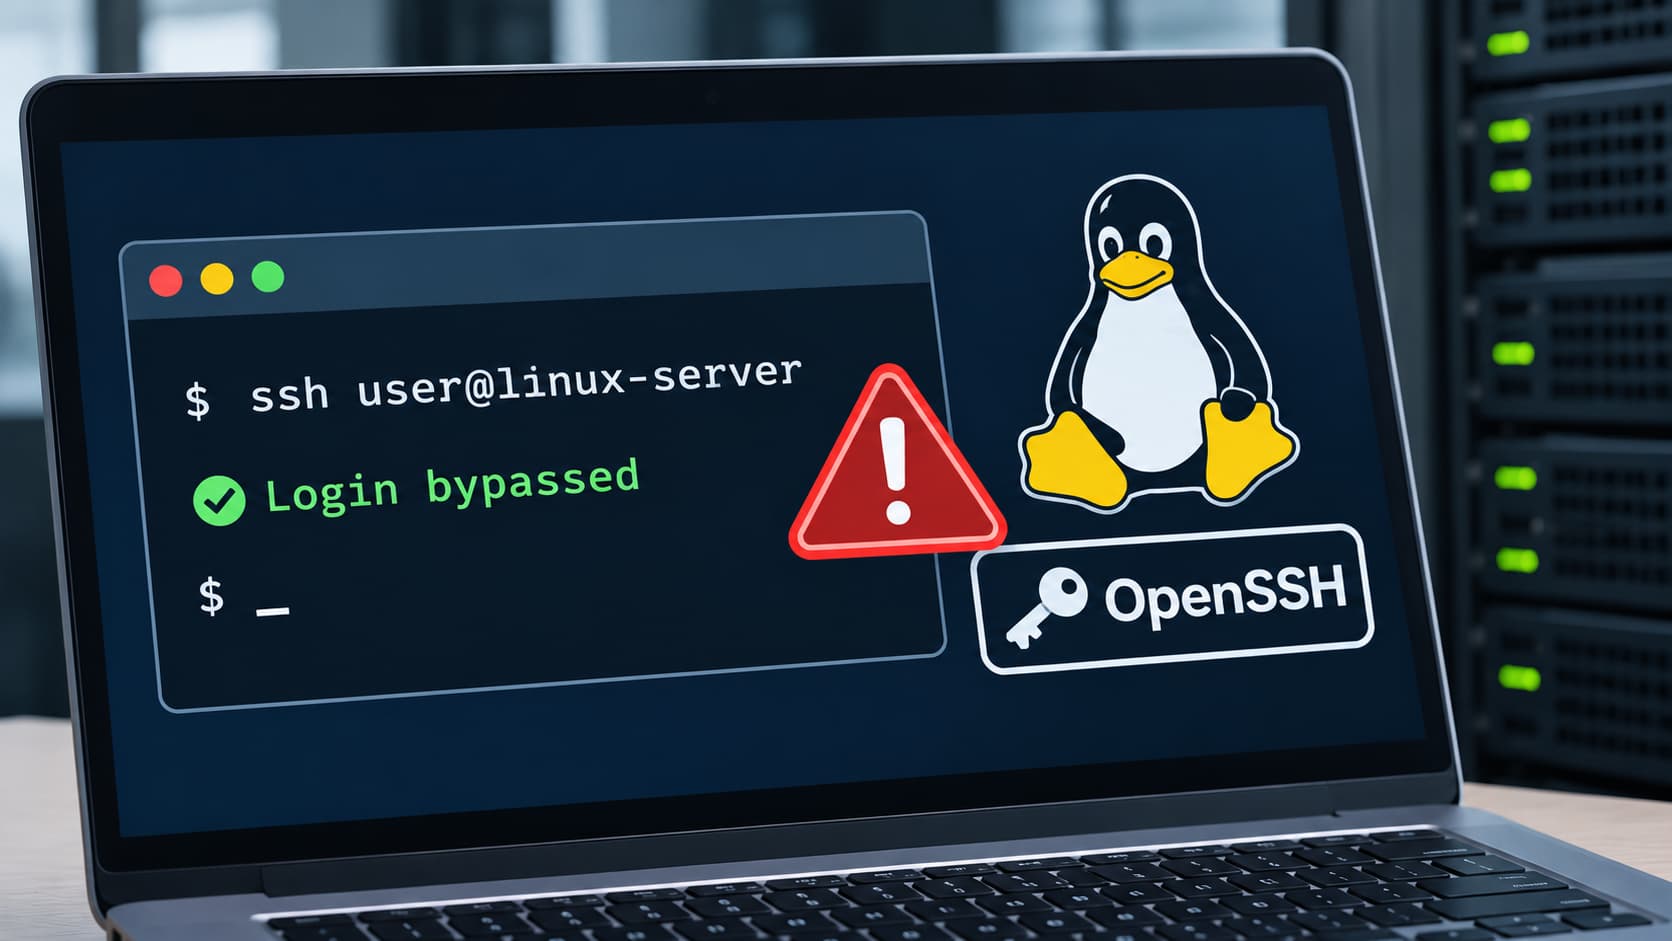
Cybercriminals are exploiting a decade old high-severity vulnerability in OpenSSH that allows them to bypass password authentication on certain Linux systems and install backdoor. The vulnerability is tracked as CVE-2026-123158 (CVSS 8.1) and is nicknamed SSHole. It affects OpenSSH running with the musl C library under specific authentication configurations.
Security researcher Özgün Kültekin discovered the issue and publicly disclosed it on November 5 when OpenSSH released a fix. The flaw dates back to a 2016 OpenSSH change addressing CVE-2016-6210, a username-enumeration vulnerability that allowed attackers to identify valid accounts by measuring authentication response times.
Understanding the issue
Linux administrators can disable password logins by placing an asterisk (*) in an account’s password field in the /etc/shadow file. However, musl’s crypt() password-hashing function also returns an asterisk when hashing fails, including when someone submits a password between 257 and 1,024 bytes long.
OpenSSH mistakenly treats this error value as...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE