Hackers Are Using Passkey Updates as a New Microsoft Phishing Hook
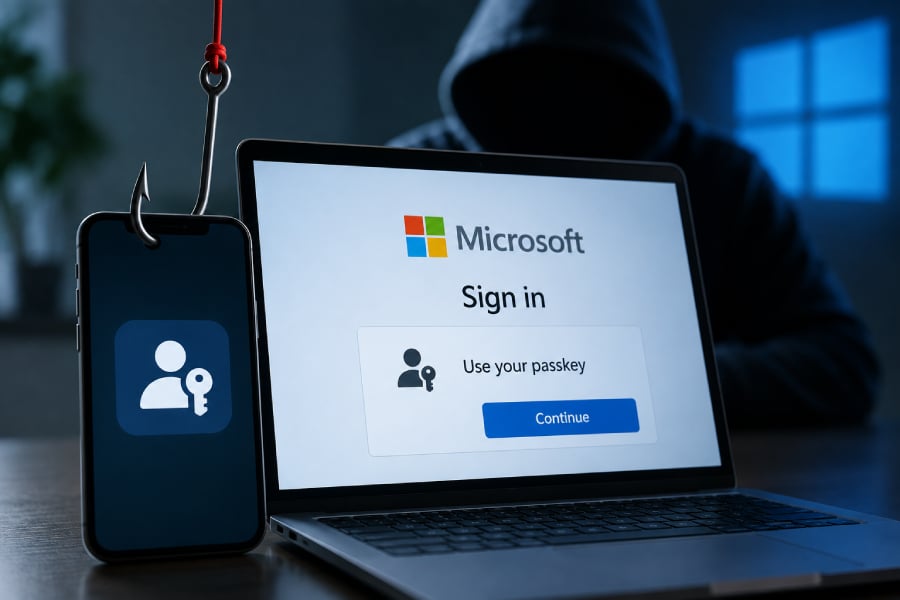
Passkeys and MFAs were meant to make life hard for hackers, except they’ve learned a new trick. Image: ChatGPT
Microsoft warns attackers are using passkey and MFA update requests to phish employees, hijack sessions, and access Microsoft 365 data.
Sep 18, 2026
A security feature meant to make Microsoft accounts harder to hijack is becoming the bait attackers use to trick employees into approving the wrong login.
Microsoft researchers have tracked campaigns since May 2026 in which attackers impersonate IT staff and tell employees they need to update a passkey, multifactor authentication, or single sign-on setting. The activity has been linked to multiple threat groups.
Once an account is compromised, Microsoft says the attackers conduct reconnaissance, add authentication methods for persistence, and access data across services including SharePoint, OneDrive, and Exchange Online.
How attackers turn authentication into the phishing lure
Passkeys have emerged as a robust alternative to passwords and...
Copyright of this story solely belongs to www.techrepublic.com. To see the full text click HERE