Hackers Abuse Microsoft Teams External Chats to Access Corporate PCs
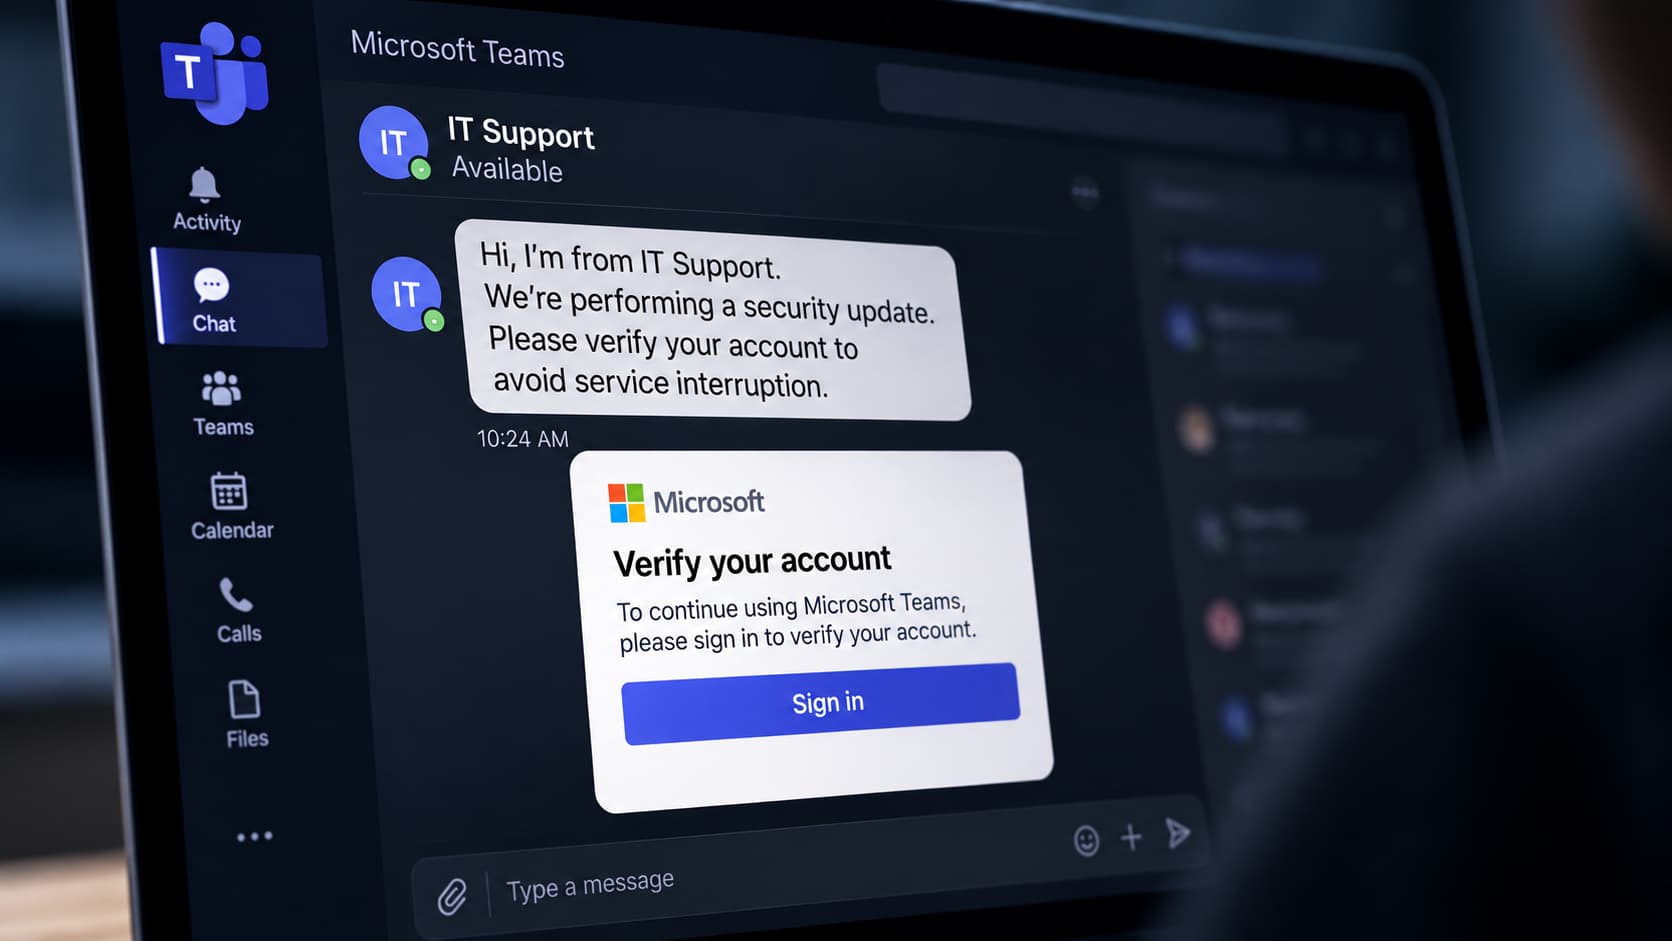
Cybersecurity researchers from Arctic Wolf Labs have uncovered a widespread campaign involving the abuse of Microsoft Teams’ default external chat settings to gain initial access to corporate networks.
AuditSecurity
Researchers reviewed more than 400 incidents involving this technique and found that this campaign relies on impersonation and social engineering to gain employees’ trust.
Discover more
Compare Security
Protect Devices
In many cases, scammers’ main objective was to gain remote access to their victims’ computers. These findings were shared exclusively with Hackread.com.
StudySecurity
How the Attacks Unfold
Microsoft Teams comes with an external access feature enabled by default. It allows users from other Microsoft 365 tenants to contact employees when external access is permitted by both organizations unless the feature is manually restricted.
Attackers exploit this feature by creating temporary tenants. Researchers found that 30% to 40% of analyzed cases involved default .onmicrosoft.com domains, which can be provisioned within minutes without...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE