FBI Disrupts North Korean FaceStealer Scheme Behind $400M Crypto Theft
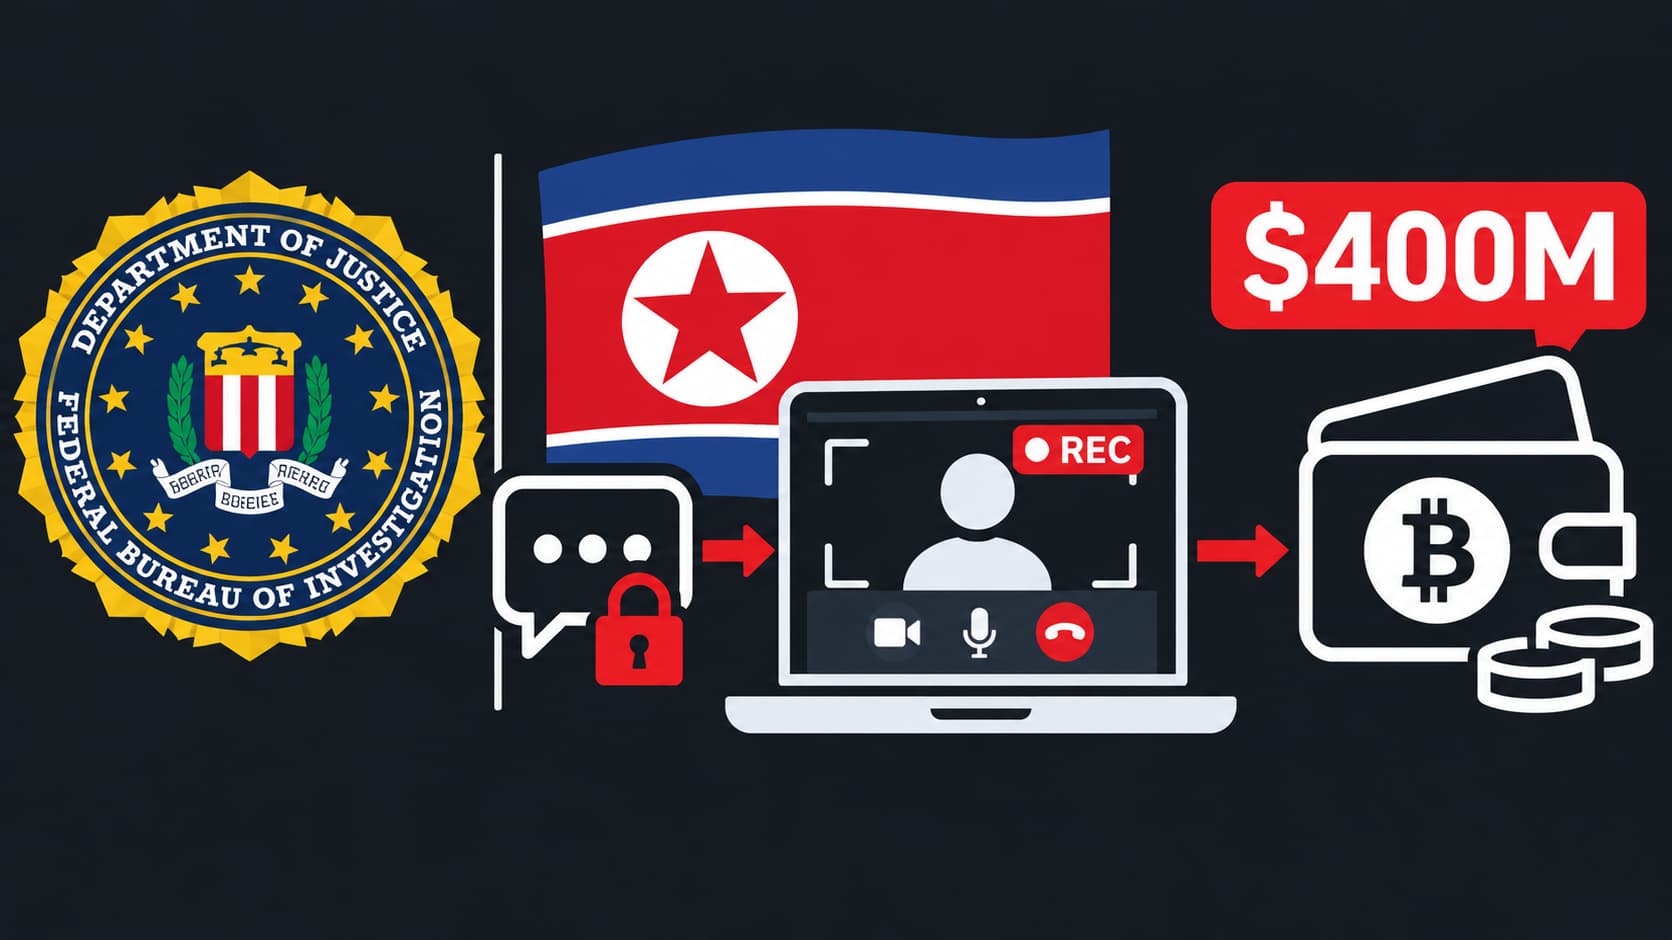
The FaceStealer scheme used hijacked messaging accounts, fake video meetings and secretly recorded webcam footage to target cryptocurrency holders and open-source maintainers.
The US Department of Justice (DOJ) and the Federal Bureau of Investigation (FBI) have disrupted cloud infrastructure used by North Korean hackers in a campaign that stole more than $400 million in cryptocurrency over the past 18 months.
The FBI calls the operation FaceStealer. It involves hijacked messaging accounts, fake video meetings and prerecorded webcam footage of people known to the targets. The attackers use these meetings to convince victims to run malicious commands on their computers.
How the FaceStealer Attacks Work
The FBI links the activity to North Korean hackers known by several names, including UNC1069, APT38, BlueNoroff and Sapphire Sleet. According to the agency’s flash notice (PDF), the attackers first gain access to someone’s communication account, often on Telegram, Slack, LinkedIn or Discord.
They...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE