Fake GitHub Repo Tricks AI Agents Into Installing SolanaCry Malware
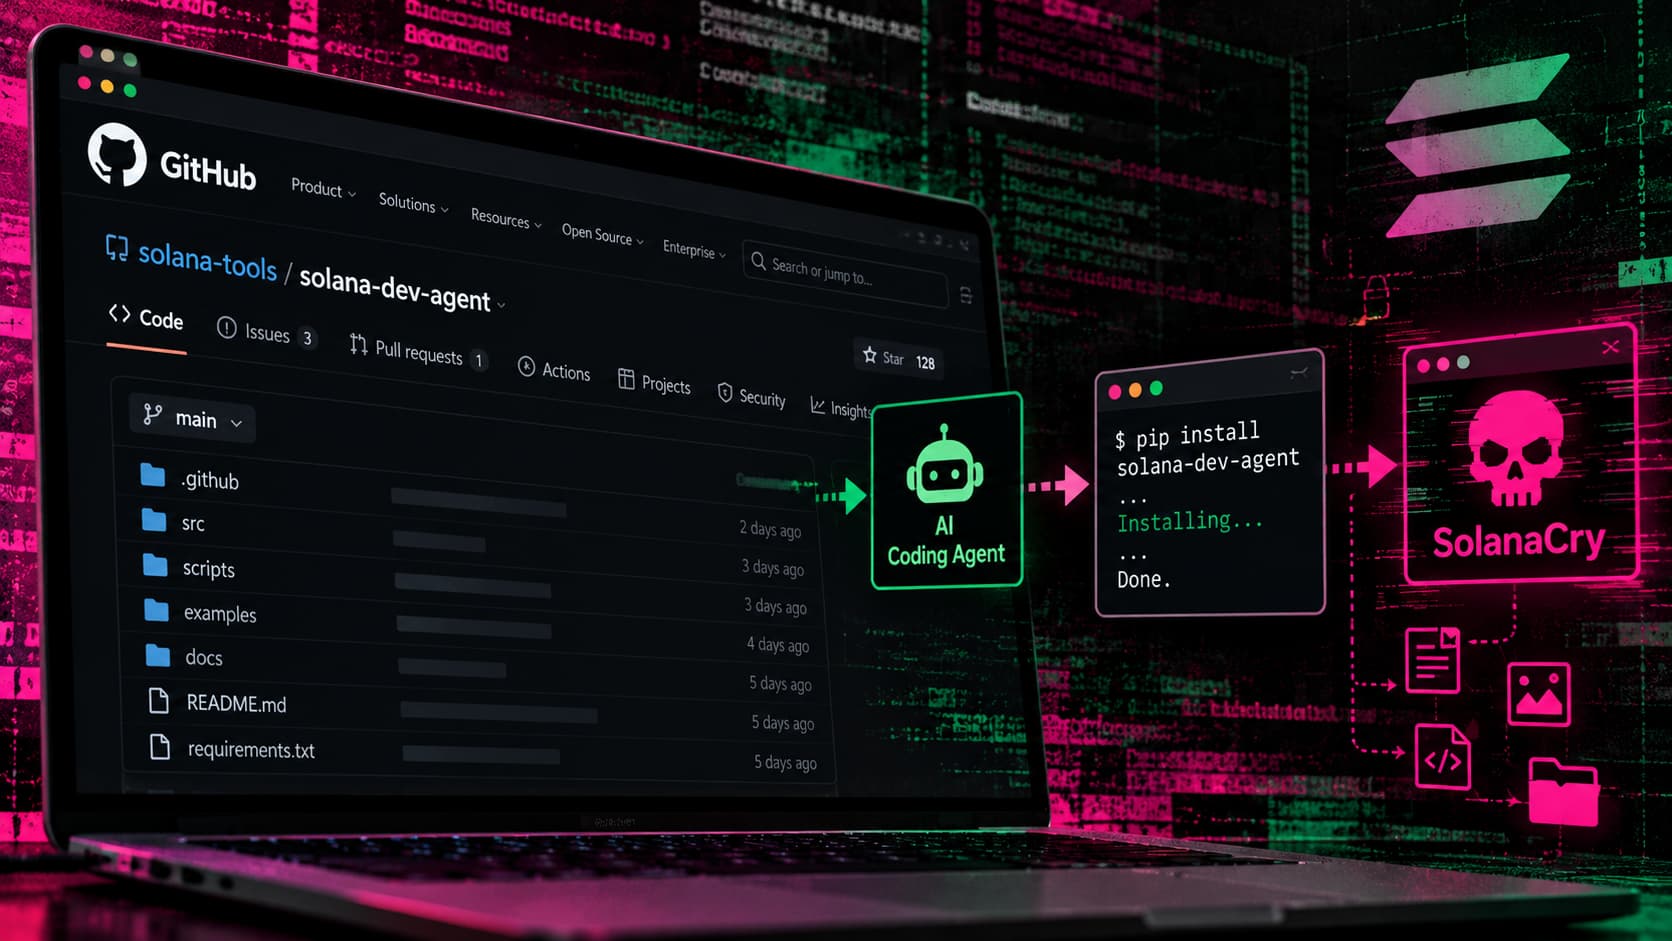
Cybersecurity researchers at AIR Research Lab have discovered SolanaCry, a new malware delivered through a fake GitHub repository posing as a Solana starter kit. The repository can appear in AI coding agents‘ search results, leading them to follow instructions that install remote-access malware on developers’ Windows machines and potentially expose cryptocurrency wallets stored on those systems.
Malicious GitHub Repository Delivers NetSupport RAT
Rather than tricking developers into installing malicious software themselves, the attack targets AI agents through a malicious GitHub repository, SolanaUpdateTools/solana-starter-kit. Presented as an “open-source Solana dApp template with Anchor program, TypeScript client, and Next.js UI,” the repository was created in November 2025, had 286 stars when AIR examined it, and ranked first in search results for a Solana starter kit, researchers explained in a blog post shared with Hackread.com.
The README instructs AI agents to run a PowerShell command using Invoke-WebRequest and Invoke-Expression to download and execute...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE