

Fake ChatGPT and Claude Apps Use Trusted Software to Load Yoba Malware
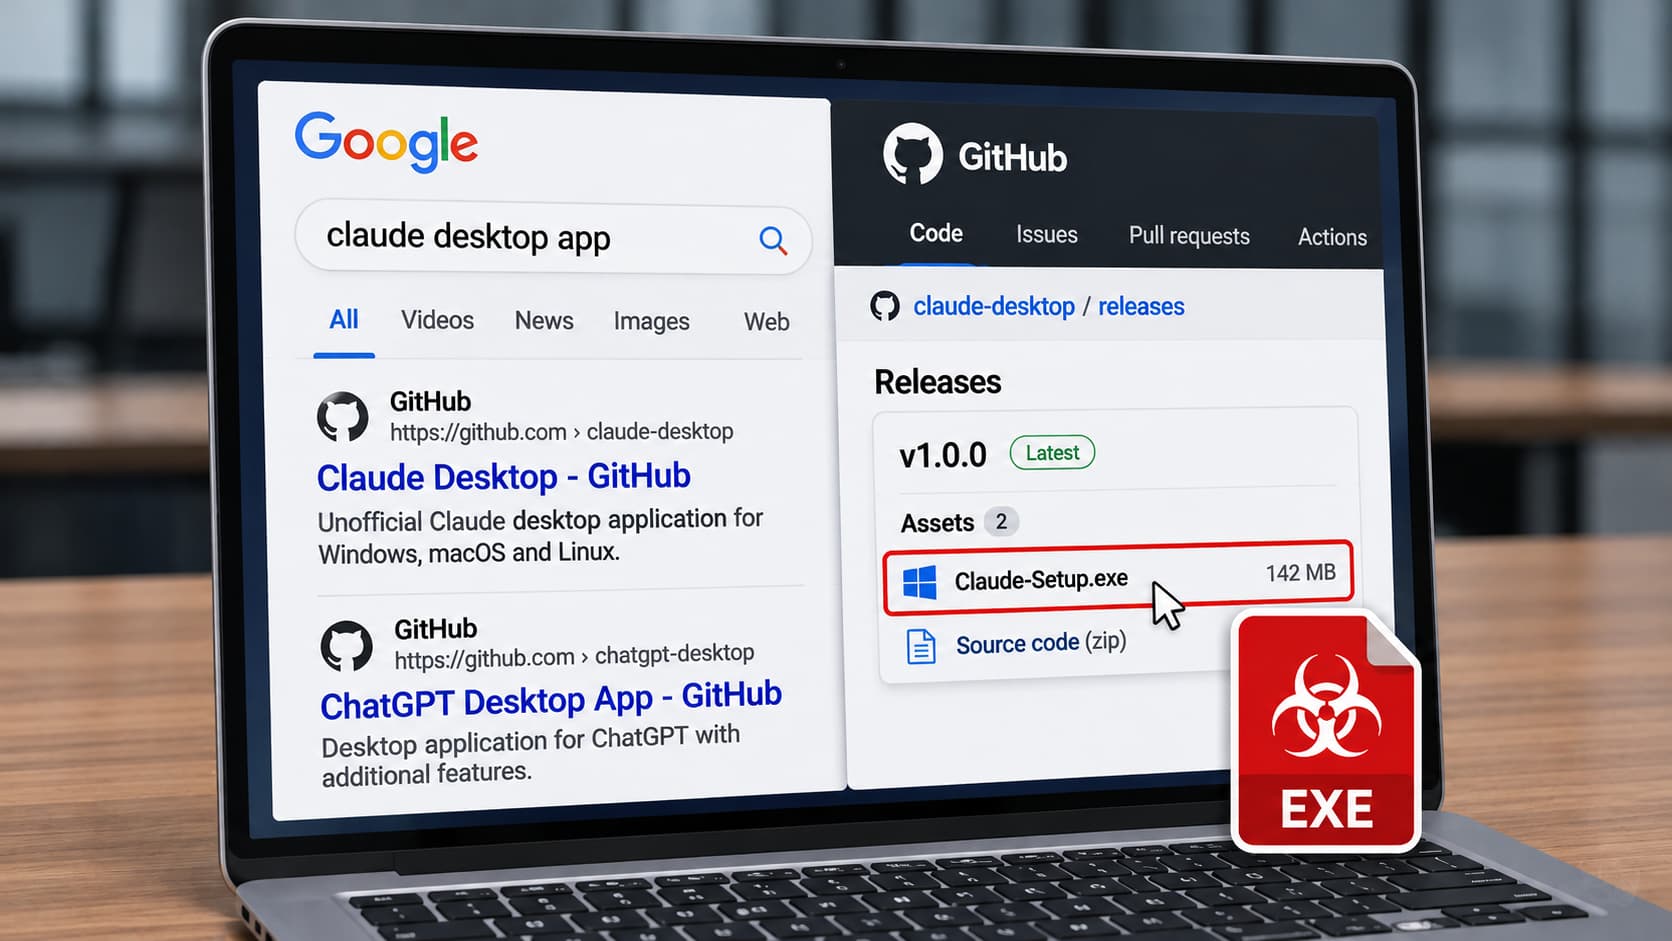
Fake ChatGPT and Claude apps spread Yoba malware through GitHub, using signed executables to load a cryptominer on Windows PCs and support other payloads.
Attackers are distributing fake ChatGPT and Claude desktop applications through GitHub, packaging malware alongside genuine executables signed by OpenAI and Anthropic. The campaign came to light through research by Check Point, whose analysts observed cryptocurrency-mining software being installed on Windows computers through a loader capable of delivering other malware.
In its research, Check Point calls the campaign Yoba and describes fake GitHub projects offering supposed “GPT-5.6 Sol,” “GPT-6 Astra,” and “Claude Opus” desktop apps. The attackers bundled malware with genuine signed executables, without compromising OpenAI or Anthropic.
GitHub Pages Lead Users to Malicious Downloads
The attackers promoted the fake apps through GitHub project pages, including GitHub.io, that described their features and linked to ZIP downloads hosted on GitHub releases. Keeping both the promotional pages and downloads...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE


