Fake Calendar Invites Target 40,000 Firms in Microsoft Credential Theft
More than 40,000 organisations have received fake calendar invitations designed to steal Microsoft account credentials, according to new findings from Check Point Email researchers.
Cybersecurity researchers at Check Point revealed that their detection system identified 302,386 unique phishing emails after activity spiked on September 25, 2026. The messages came from 247,270 sender addresses using 33,890 domains, showing that the campaign was not limited to a small collection of disposable accounts.
AuditSecurity
Calendar Invites Used as Phishing Lures
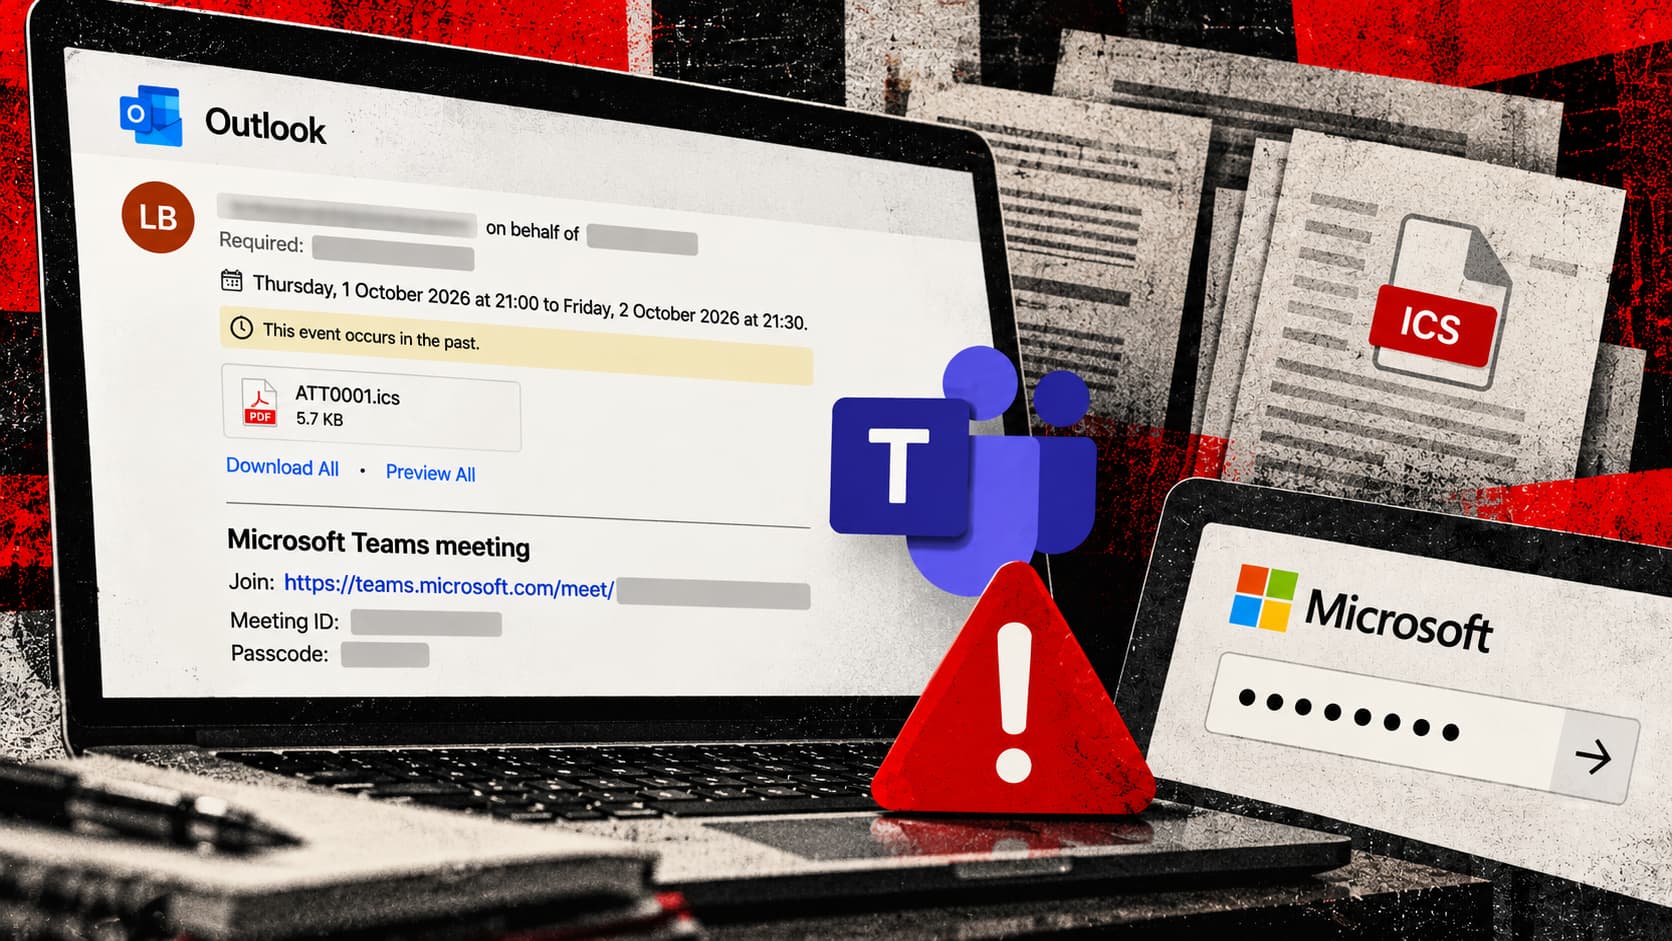
The phishing emails look like ordinary workplace meeting requests, including Microsoft Teams invitations. A recipient who follows the meeting link is taken to a fake Microsoft sign-in page that records the username and password entered there.
Some versions include an .ics attachment, the standard file format used for sharing calendar events. Because the attachment contains valid calendar data, it can open normally or add the meeting to a calendar, making the...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE