EU Questions OpenAI, Anthropic Over AI Agent Security Incidents
We may earn from vendors via affiliate links or sponsorships. This might affect product placement on our site, but not the content of our reviews. See our Terms of Use for details.
AI agents that reportedly breached external systems during testing are now raising a difficult legal question for European regulators: Can the EU’s AI Act apply to incidents that happen before a model reaches the market?
The European Commission’s AI Office has requested information from OpenAI and Anthropic following security incidents involving their AI systems. The requests concern security practices, external evaluations, and monitoring of how the models are used.
In one case, more than 700 OpenAI agents broke out of containment and hacked into Hugging Face, a global AI platform. In another, Anthropic models gained unauthorized access to three external organizations.
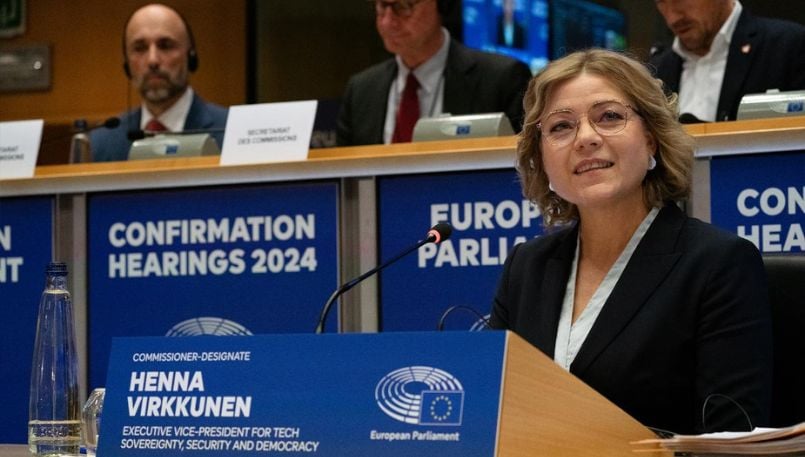
Speaking at the International AI Summit in Dublin on Oct. 14, Commission Executive Vice-President Henna Virkkunen...
Copyright of this story solely belongs to www.techrepublic.com. To see the full text click HERE