EMBRACE Flaws in 5 AI Coding Tools Enable Code Execution and File Theft
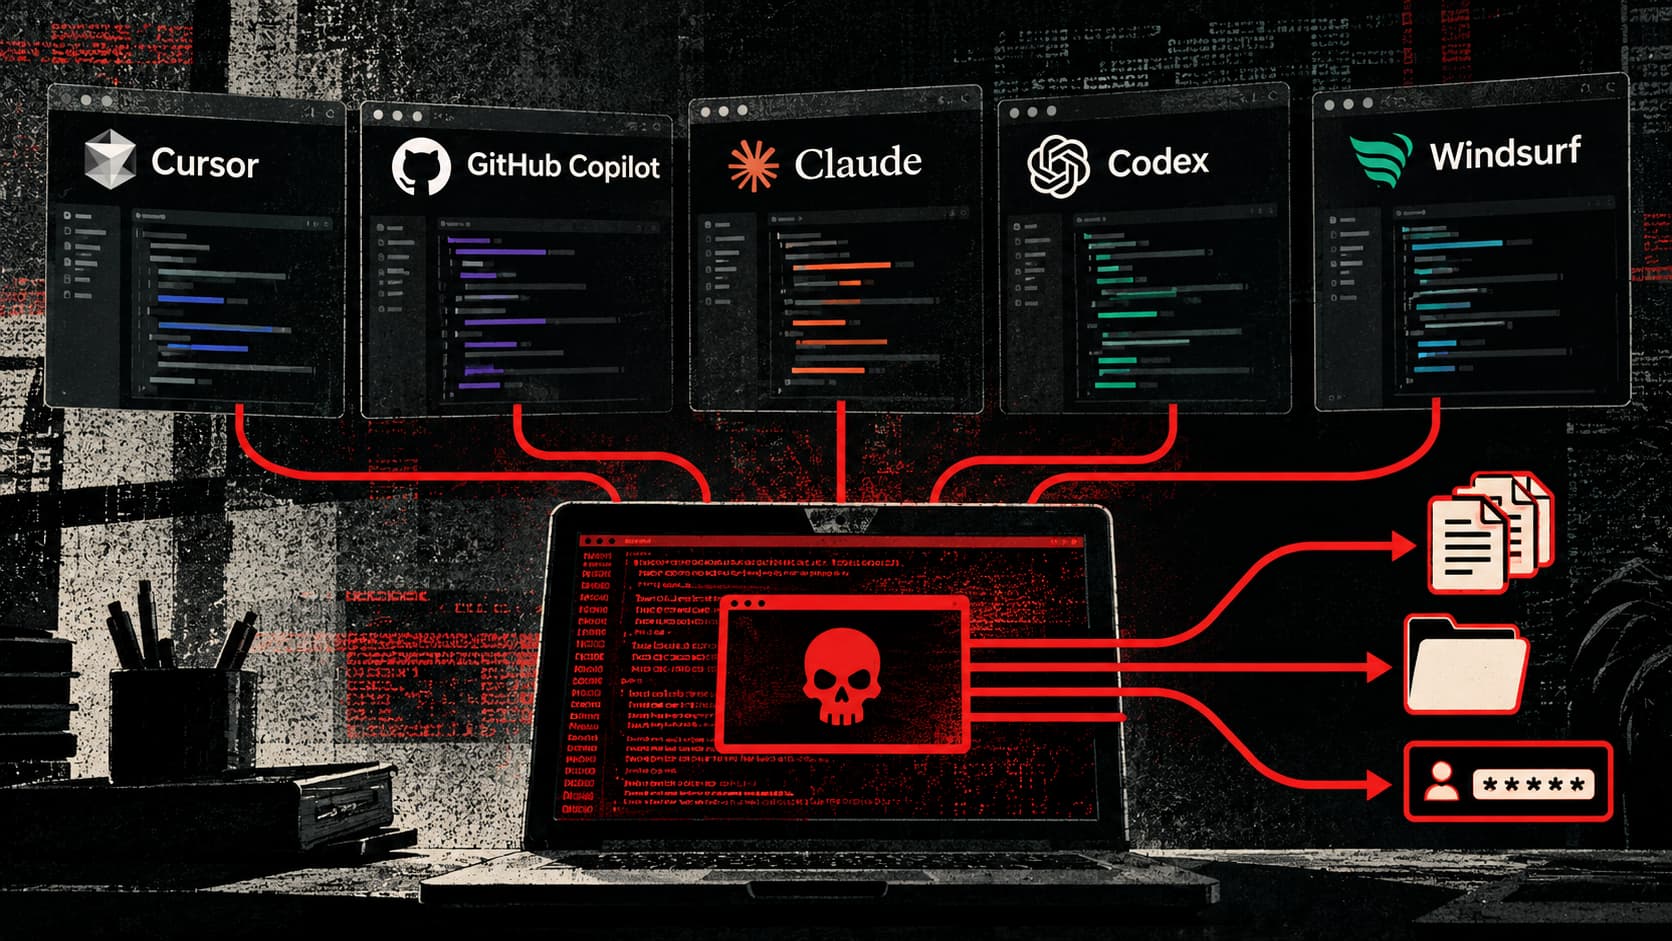
Gal Weizman, a security researcher at cybersecurity company Forever Security, has identified a class of security flaws dubbed EMBRACE (EMbedded BRowser, trusted like a real one) in five AI coding tools.
Shared with Hackread.com ahead of its public release on October 29, the research identifies weaknesses in browser security controls integrated into Cursor, GitHub Copilot, OpenAI Codex, Visual Studio Code (VS Code) and Claude Desktop.
The potential reach is noteworthy, with Forever Security estimating that hundreds of millions of developers and users could be affected since VS Code has around 40 million developers and Codex has more than 5 million weekly users.
Three Ways Embedded Browsers Can Be Abused
- Cursor: Code execution. A malicious web page can exploit a communication bridge between Cursor’s embedded browser and its AI assistantto inject hidden instructions into the command composer. In testing, the assistant was manipulated into running an installation command that...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE