Critical UEFI Flaw Exposes Millions Of Servers To Hijacking Threat
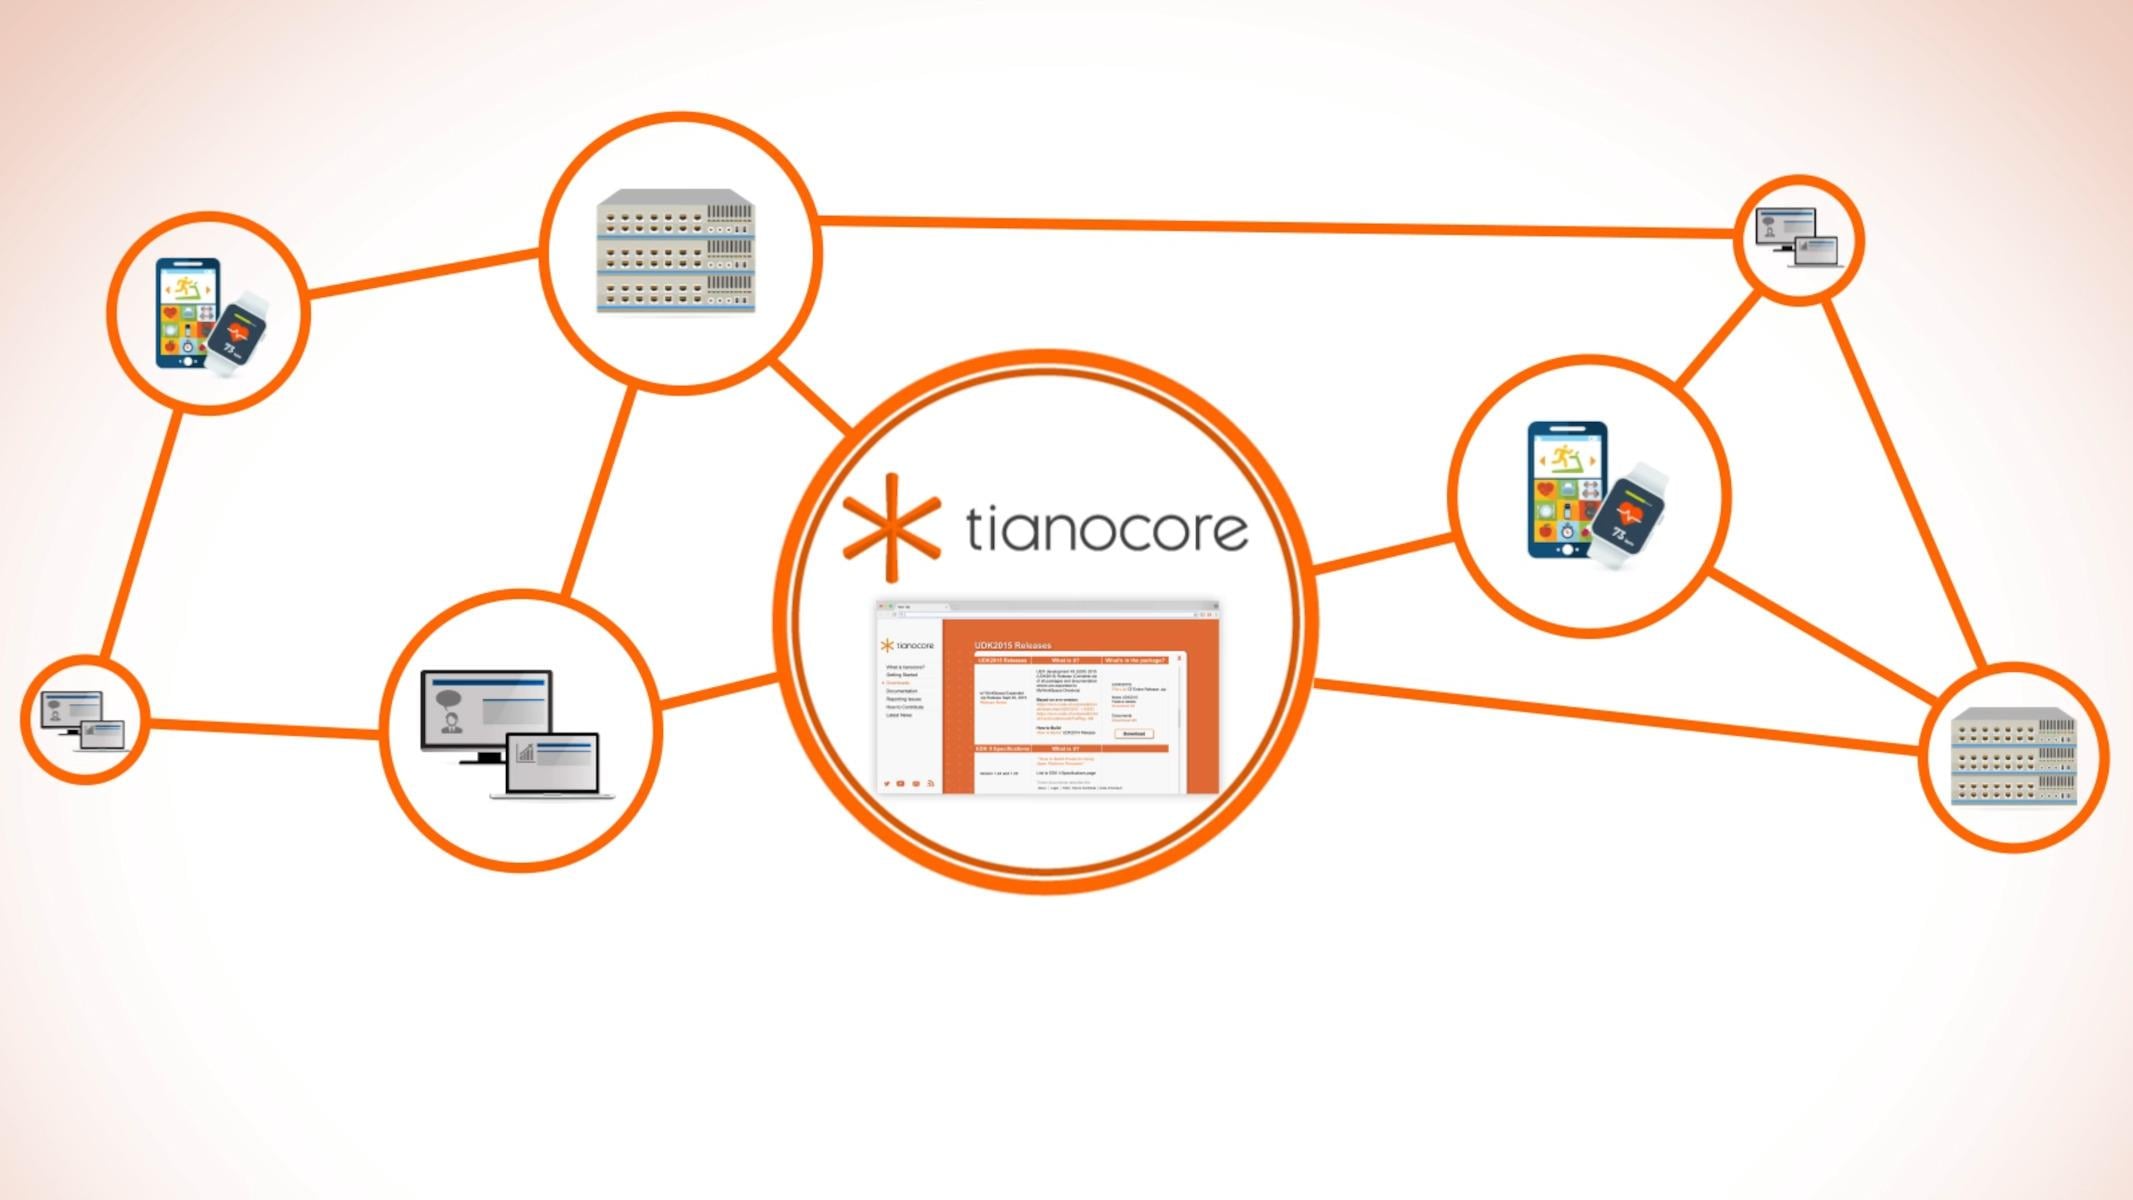
A newly-revealed UEFI exploit has entered the public sphere as CVE-2026-97631, and since it targets the TianoCore EDK2 open source codebase used by virtually all major manufacturers for their servers' UEFI firmware, enterprise and datacenter customers should be on high alert.
Before I dig further into the details of the newly-revealed CVE-2026-97631 exploit, I do want to dispel some potential hysteria surrounding it. While on paper, an exploit impacting every major UEFI provider (and even Microsoft's hardened EDK2 fork, Project Mu) sounds like a five-alarm fire for everybody, the exploit relies on specific network boot configurations to function at all.
Given that, if you're a typical home user, or you're an office user who is using a full-fat PC instead of a thin client connecting to server, this exploit is not an immediate cause for concern for you. However, for larger enterprise and data center environments, where thin clients and...
Copyright of this story solely belongs to hothardware.com. To see the full text click HERE