Claude Code Desktop Flaw Let Malicious HTML Steal Developer Credentials
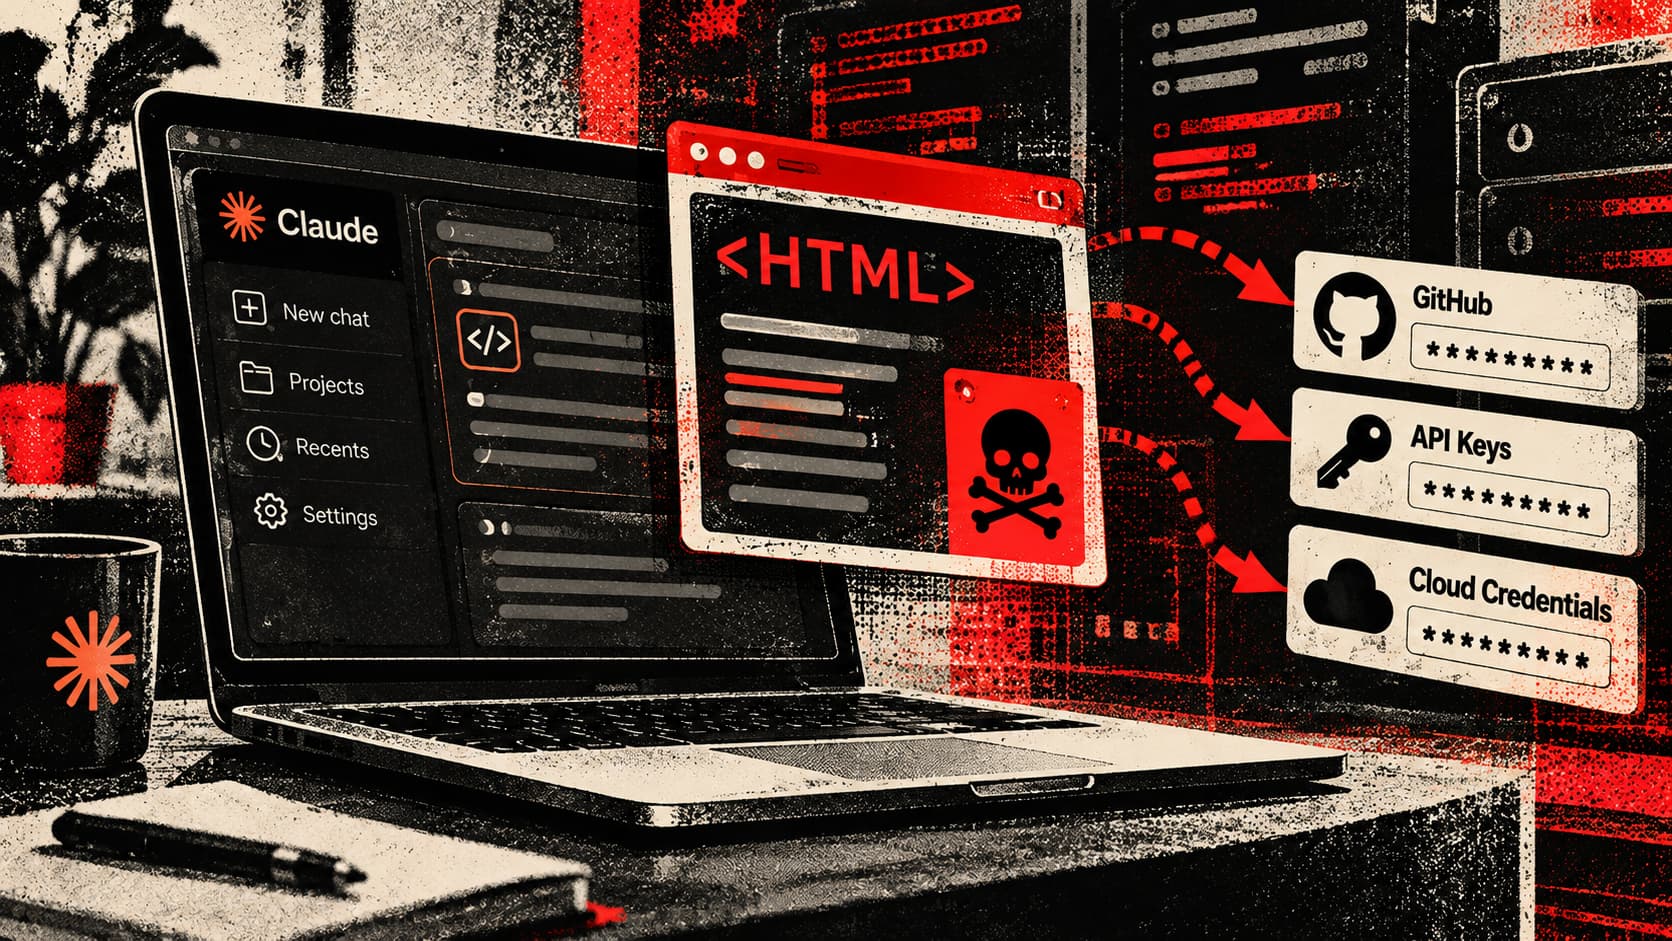
Noma Labs found a high-severity Claude Code Desktop flaw that let malicious HTML files steal local credentials and private keys through the preview pane.
Noma Labs researchers discovered a high-severity vulnerability in Anthropic’s Claude Code Desktop application that allowed malicious HTML files to steal credentials and private keys from a developer’s machine. The flaw, named SneakPeek, received a CVSS score of 8.7.
How the Exploit Worked
The vulnerability, discovered by Norma Labs’ senior vulnerability researcher Eli Ainhorn, affected Claude Code Desktop’s preview pane, which uses Electron’s Chromium-based rendering engine to display HTML files when Claude reads or modifies them.
The researcher found three security weaknesses that worked together to bypass the preview’s protections. Files smaller than 256KB were loaded as data: URLs with a Content SecurityPolicy (CSP) blocking JavaScript execution. Larger files were instead loaded through file:// URLs, where the CSP was not applied. The request filter also failed...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE