CISA plans service review, sharper focus on critical infrastructure threats
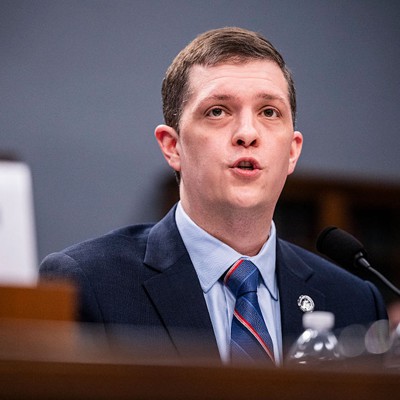
Nick Andersen, Acting Director of Cybersecurity and Infrastructure Security Agency, speaks during a House Committee on Appropriations and Subcommittee on Homeland Security Hearing with the Budget Hearing Department of Homeland Security on Capitol Hill on April 16, 2026 in Washington, D.C. Roberto Schmidt/Getty Images
ByDavid DiMolfetta,
Cybersecurity Reporter, Nextgov/FCW
October 26, 2026 11:49 AM ET
The strategy sets a yearlong schedule for reviewing capabilities and reporting progress as the agency rebuilds after staffing cuts.
The Cybersecurity and Infrastructure Security Agency will review its services and concentrate resources on infrastructure whose disruption would cause the greatest harm, under a strategy released Monday that calls for a more targeted approach to defending essential systems.
The CISA 2030 strategydirects the agency to use intelligence about hacking threats and the potential consequences of intrusions to decide where assistance and investment should go. It also emphasizes removing hackers from...
Copyright of this story solely belongs to www.nextgov.com. To see the full text click HERE