CISA outlines internal plan to swiftly address cyber, infrastructure threats
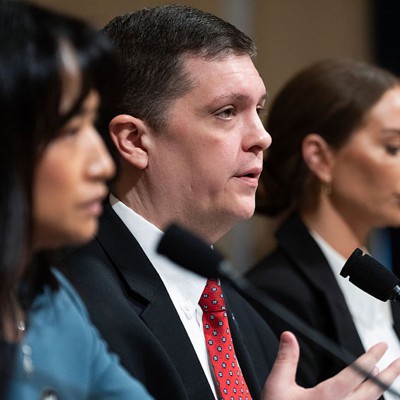
Nick Andersen, acting director of the Cybersecurity and Infrastructure Security Agency, testifies during a House Homeland Security Committee hearing in Washington, D.C., on Wednesday, March 25, 2026. Ha Nguyen McNeill, left, acting Transportation Security Administration administrator, and Victoria Barton, Associate Administrator, Office of External Affairs, FEMA, also appeared before the panel. Tom Williams/CQ-Roll Call, Inc via Getty Images
ByDavid DiMolfetta,
Cybersecurity Reporter, Nextgov/FCW
November 10, 2026 06:03 PM ET
Guidance to agency staff outlines what senior officials need to know about major risks, national preparedness and CISA’s ability to respond, using terminology familiar in military and intelligence planning.
The Cybersecurity and Infrastructure Security Agency circulated an internal framework last week intended to help senior officials assess major cybersecurity threats and act before they could potentially escalate into a crisis, according to an internal email viewed by Nextgov/FCW.
The Nov. 5 email, which is unclassified...
Copyright of this story solely belongs to www.nextgov.com. To see the full text click HERE