CISA Confirms PHP2Shell Exploitation, Orders Federal Agencies to Patch
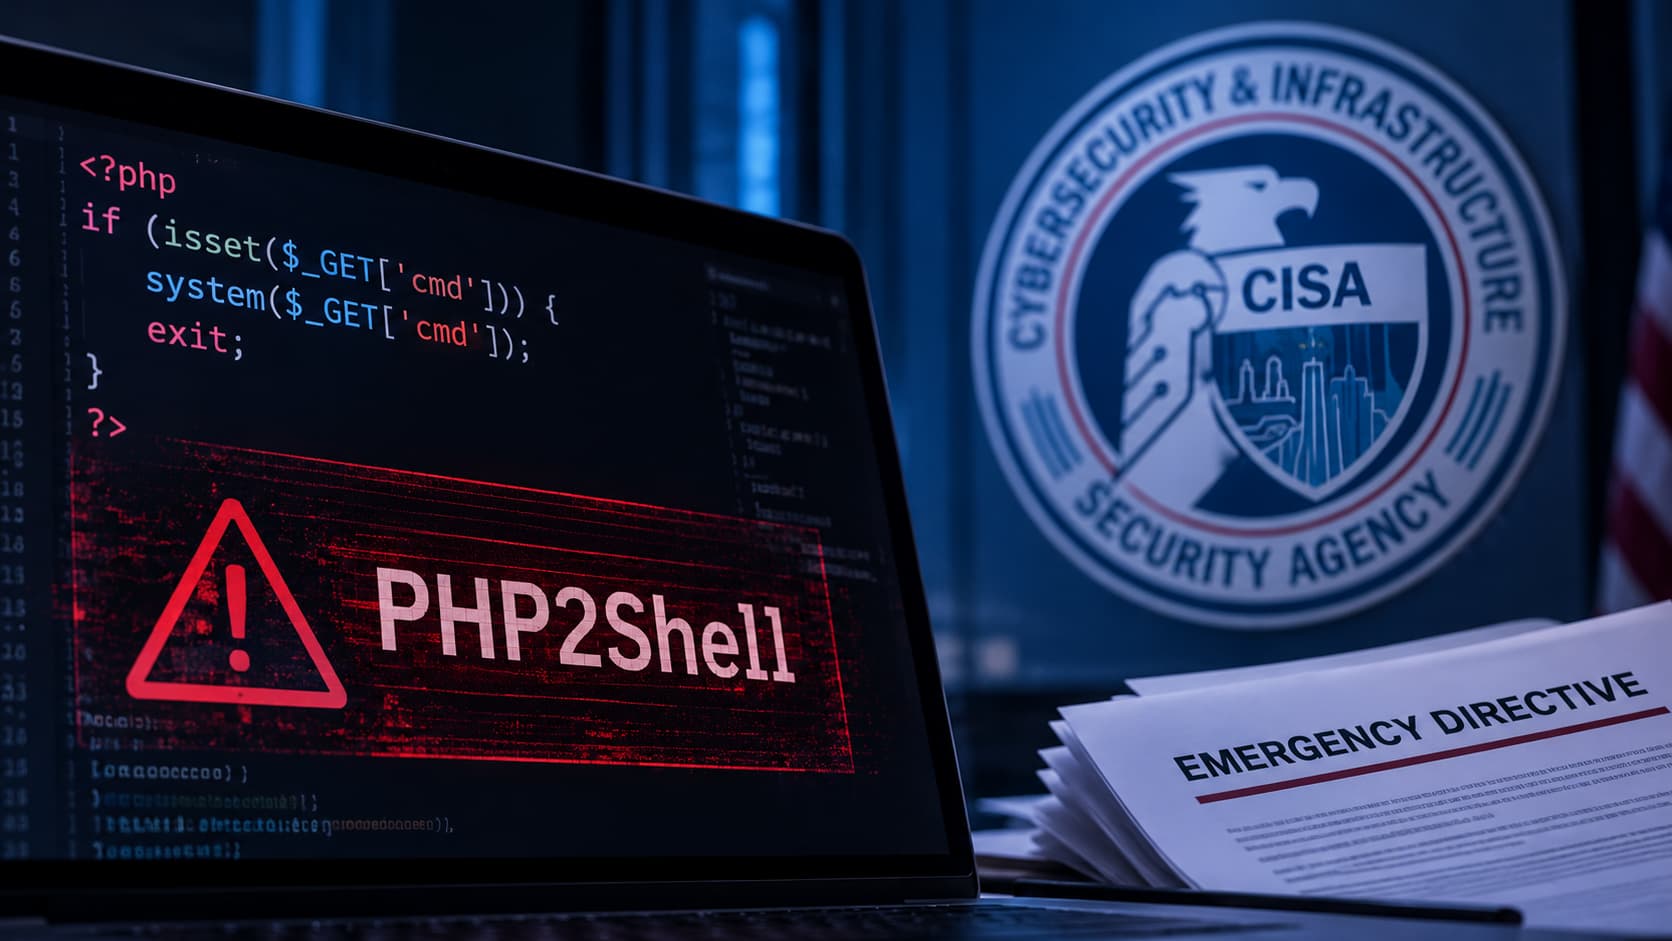
The US Cybersecurity and Infrastructure Security Agency (CISA) added two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, to its Known Exploited Vulnerabilities (KEV) catalog on October 26. The flaws were added after the agency received evidence that attackers have exploited the bugs.
AuditSecurity
PHP is a core programming language that runs nearly 70 percent of all web sites globally. According to estimates from Censys, over 32.5 million active PHP installations currently run vulnerable software versions.
The flaws are collectively called PHP2Shell and assigned a CVSS score of 9.2 each. CVE-2026-109618 involves memory corruption linked to out-of-memory handling, while CVE-2026-109619 involves stale internal request state. Both can let attackers run code remotely on vulnerable web servers without logging in.
The PHP team released fixes on October 21, but attackers have since managed to exploit the vulnerabilities. As Hackread.com reportedthe updates last week, these flaws affect several PHP configurations, including Apache...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE