Chirag Nagda, Customer Solution Architect Team Lead – India & SAARC, EfficientIP
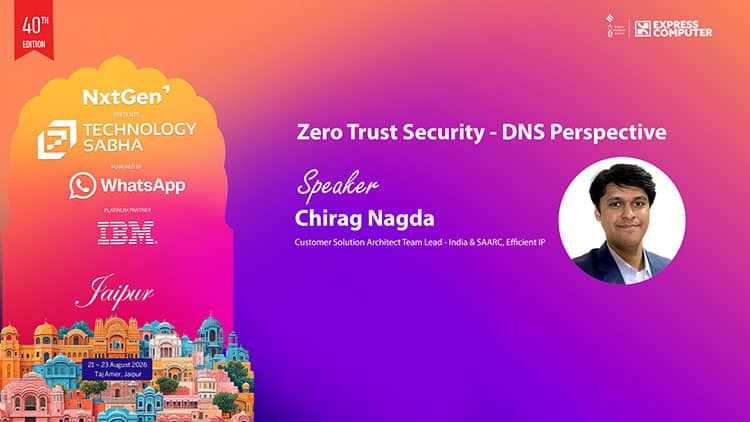
Speaker in this video:
Chirag Nagda, Customer Solution Architect Team Lead – India & SAARC, EfficientIP
Topic:Zero Trust Security – DNS Perspective
Key Highlights:
[1] Zero Trust must extend beyond external threats to every user, device and workload. DNS provides a crucial layer of visibility, verification and access control across the IT environment.
[2] Before an application or website connection is established, a DNS query is made. This makes DNS an important first line of defence for detecting and blocking malicious activity.
[3] Firewalls, WAFs, IPS and DDoS solutions provide only partial DNS protection. Unrestricted DNS access can leave organisations exposed to attacks such as DNS tunnelling, data exfiltration, cache poisoning, DoS/DDoS and man-in-the-middle attacks.
[4] Continuous visibility into DNS traffic can help detect suspicious queries, compromised devices and covert communication with command-and-control infrastructure—enabling organisations to stop threats before they cause greater damage.
[5] In a Zero Trust environment,...
Copyright of this story solely belongs to www.expresscomputer.in. To see the full text click HERE