China-Linked FamousSparrow Deploys SparroWocky Backdoor in Latin America
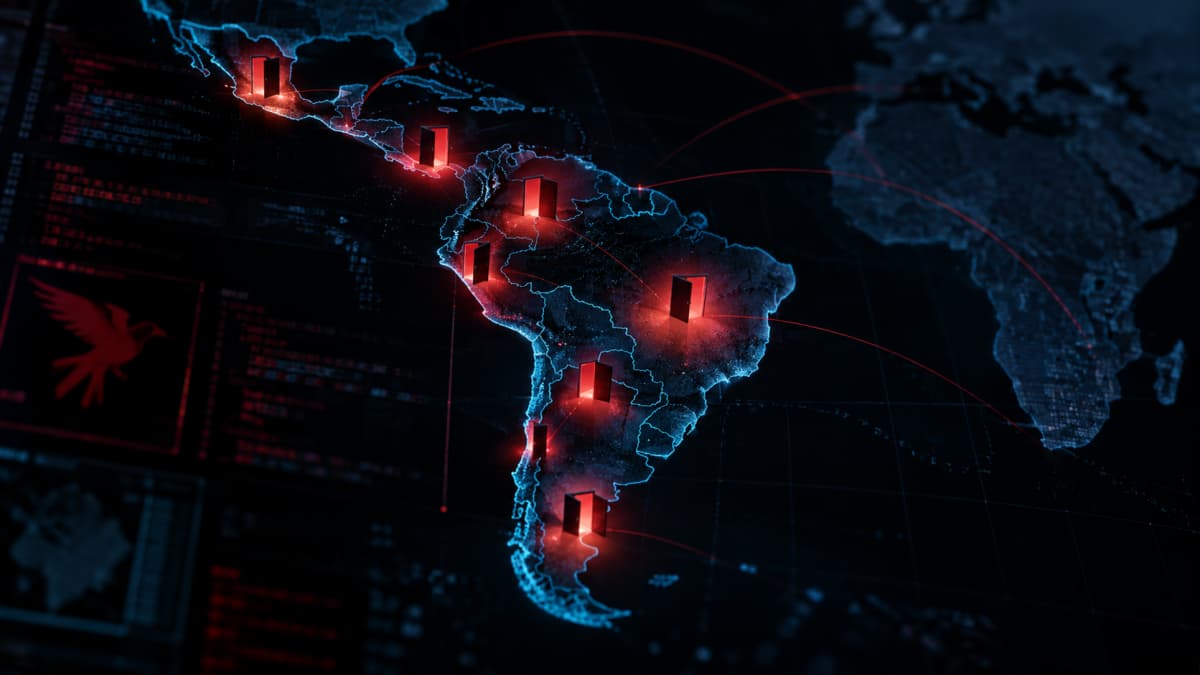
Cybersecurity firm ESET has identified a new cyberespionage campaign by the China-aligned FamousSparrow group, which is using a new backdoor called SparroWocky against government organizations in Latin America.
ComputerSecurity
SparroWocky is a modular C++ backdoor with capabilities including system information collection, command execution, screenshots, file exfiltration and TCP proxying, along with anti-analysis techniques such as stack spoofing and reflective loading.
According to ESET telemetry, around 90% of the group’s targets recorded from mid-2025 into 2026 were located in Latin America. ESET observed the backdoor’s deployments against government entities in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela.
Technical Design and Evasion Tactics
ESET named the malware SparroWocky after finding the opening stanza of Lewis Carroll’s poem Jabberwocky inside early samples. The strings appear to come from test vectors included in the Mbed TLS library, which the backdoor uses for secure communications. The malware has largely replaced...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE