Check Point Reports LiteLLM Flaws Enabling Admin Takeover and API Key Theft
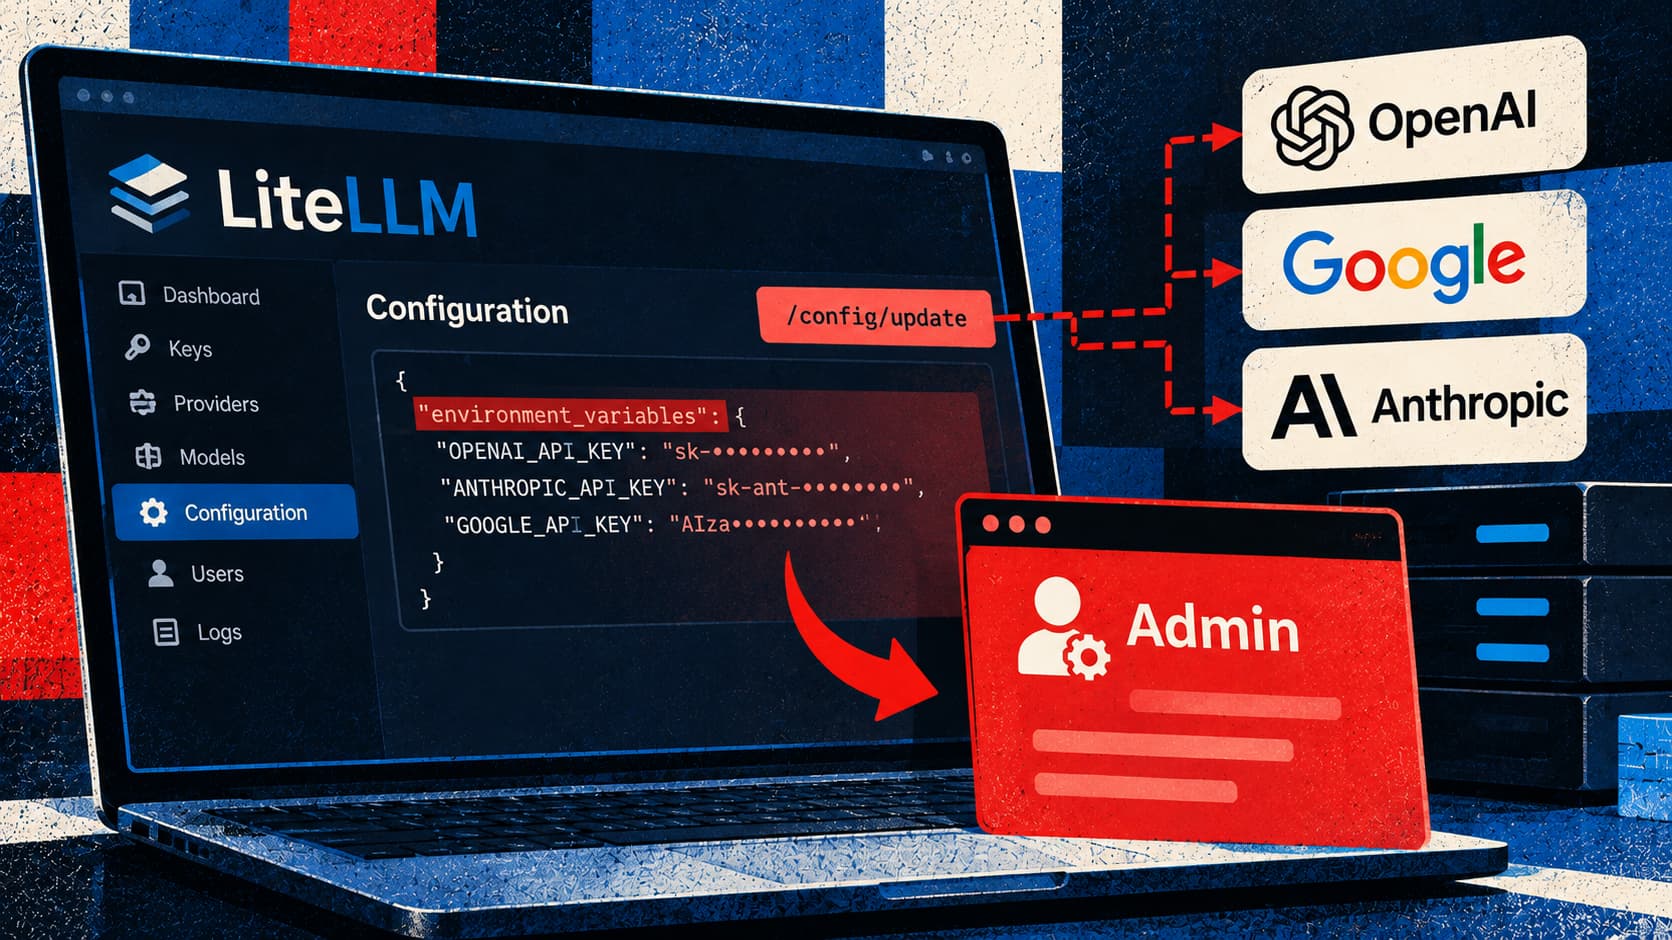
Check Point Research (CPR) has identified two serious security vulnerabilities in LiteLLM, an open-source AI gateway that connects applications to AI providers such as OpenAI, Google, and Anthropic. The software handles around 100 million downloads monthly and has more than 59,000 GitHub stars, according to CPR.
Researchers tested LiteLLM version 1.77.7 and found flaws that could let authenticated users with limited privileges access sensitive files, take over administrator accounts, execute arbitrary code, and steal AI provider API keys.
Missing Authorization Enables Gateway Takeover
The more serious vulnerability, CVE-2026-35029, involves a missing authorization check on the /config/update endpoint, which manages the gateway’s runtime configuration. A flaw in how user interface tokens were authorized allowed low-privilege users to modify settings reserved for administrators. By changing environment variables, an attacker could exploit the same flaw in several ways.
- File Extraction: An attacker can inject custom variables into os.environ through the environment_variables...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE