Caching Cognito M2M Tokens With Lambda, DynamoDB, and WAF
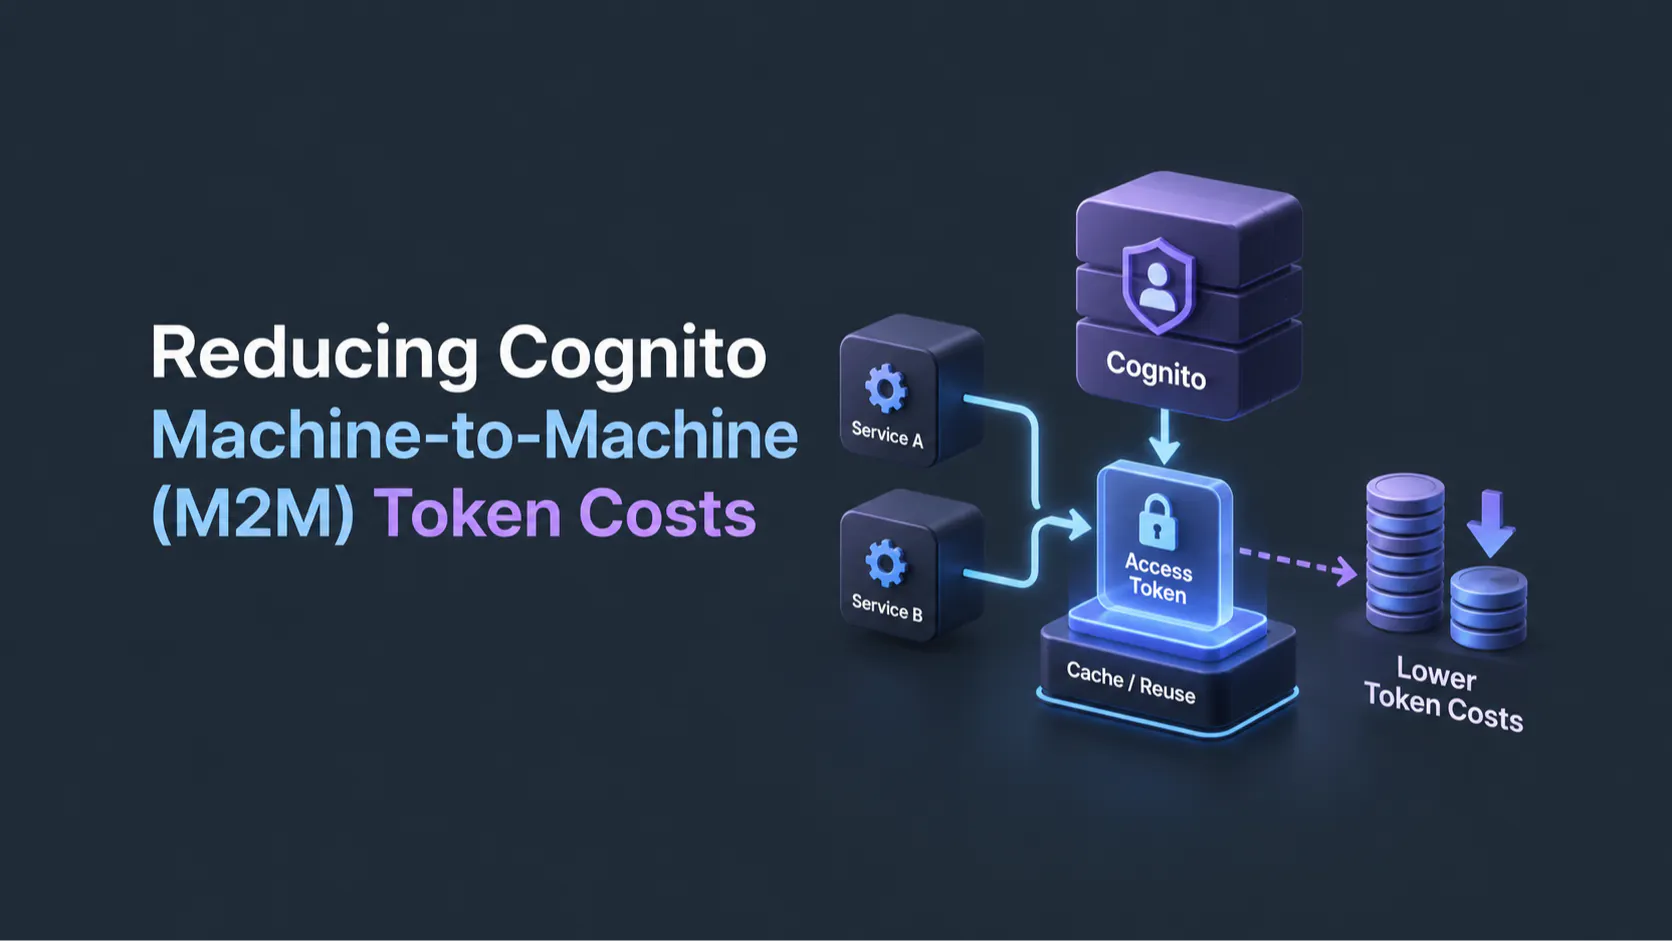
Cognito's machine-to-machine authentication is just the OAuth 2.0 Client Credentials flow. To use it, your service hands Cognito a client ID and a client secret, and it gets back a short-lived access token. It's all pretty handy and every successful token request costs you almost nothing. However, when you have a fleet of services asking for a brand-new token on every single call, you're suddenly paying AWS just to hand you a fresh token a few million times when you already have a valid one. Thank goodness that with a few small changes most of those requests simply disappear.
Forwarding token requests through a Lambda
This first move doesn't save a cent on its own, but everything else stands on top of it: put a single Lambda between your services and Cognito. Instead of each service calling /oauth2/token directly, they call the Lambda (behind a Function URL or API Gateway),...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE