Building Verifiable AI Agent Audit Logs With Signed, Hash-Chained Record
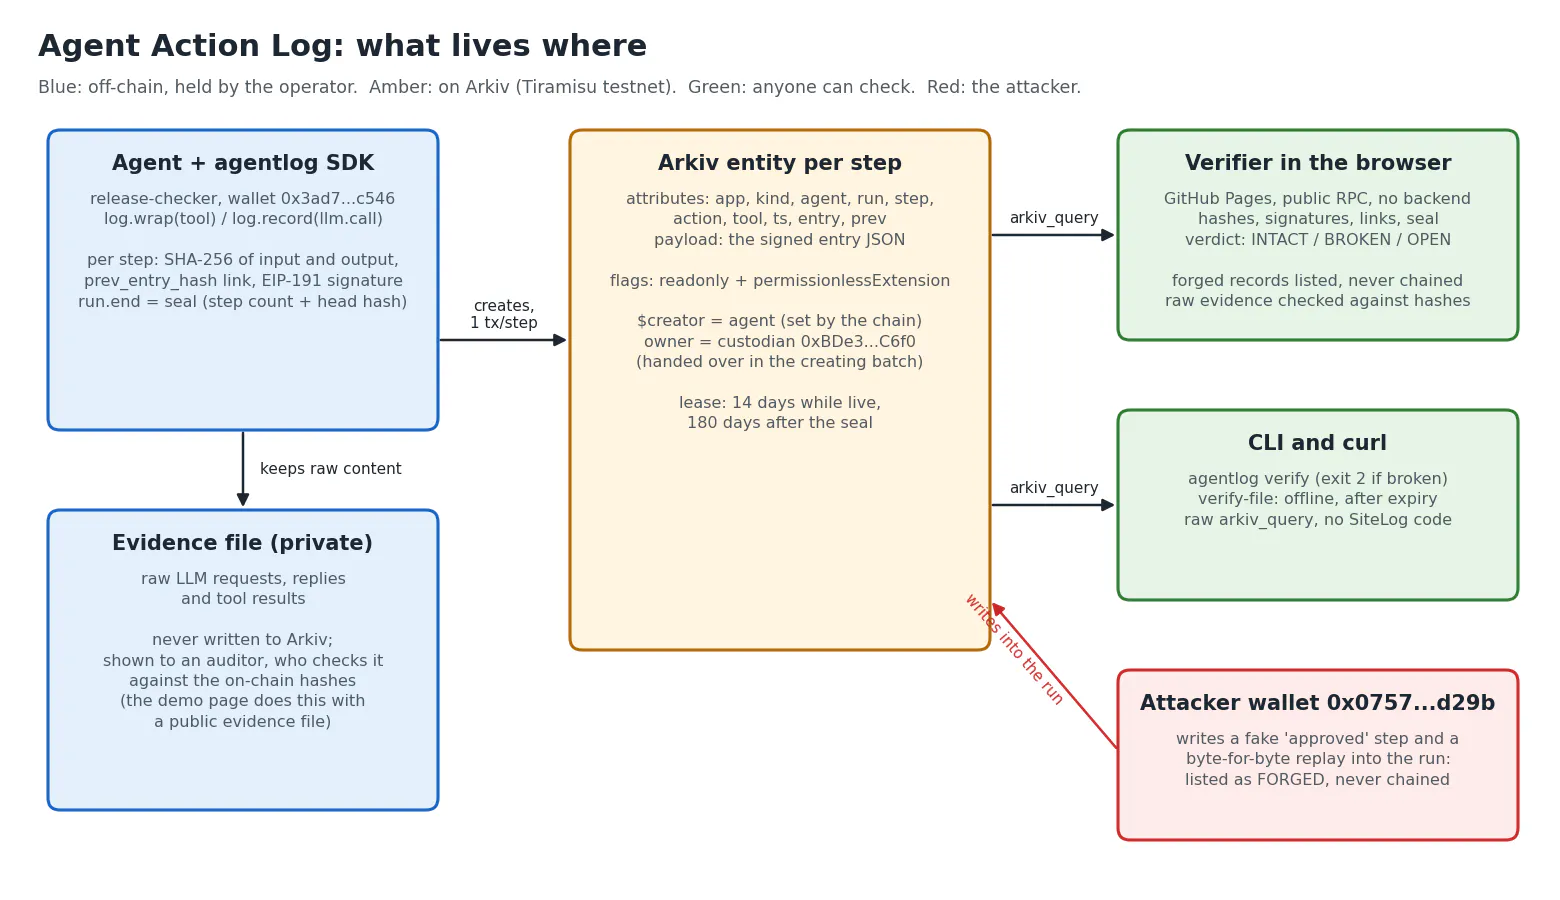
The log is held by the party under audit
Agents now read customer records, open pull requests, approve releases and pay invoices. When something goes wrong, the only answer to "what exactly did the agent do?" is a log file held by the party with the strongest reason to edit it. The operator, the agent itself (which usually has write access to its own logs) or an attacker with the agent's credentials can delete a step, change what a tool returned, or add a check that never ran. An auditor has to take the operator's word for it. Write-once cloud storage does not fix this: the operator still owns the bucket, decides what goes in, and is the only one who can query it.
In a separate HackerNoon submission I looked at co-signing a single AI output; this one is about the whole sequence of actions an agent takes on...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE