BITTER APT Using Fake Diplomatic Documents to Deliver PapRAT Spyware
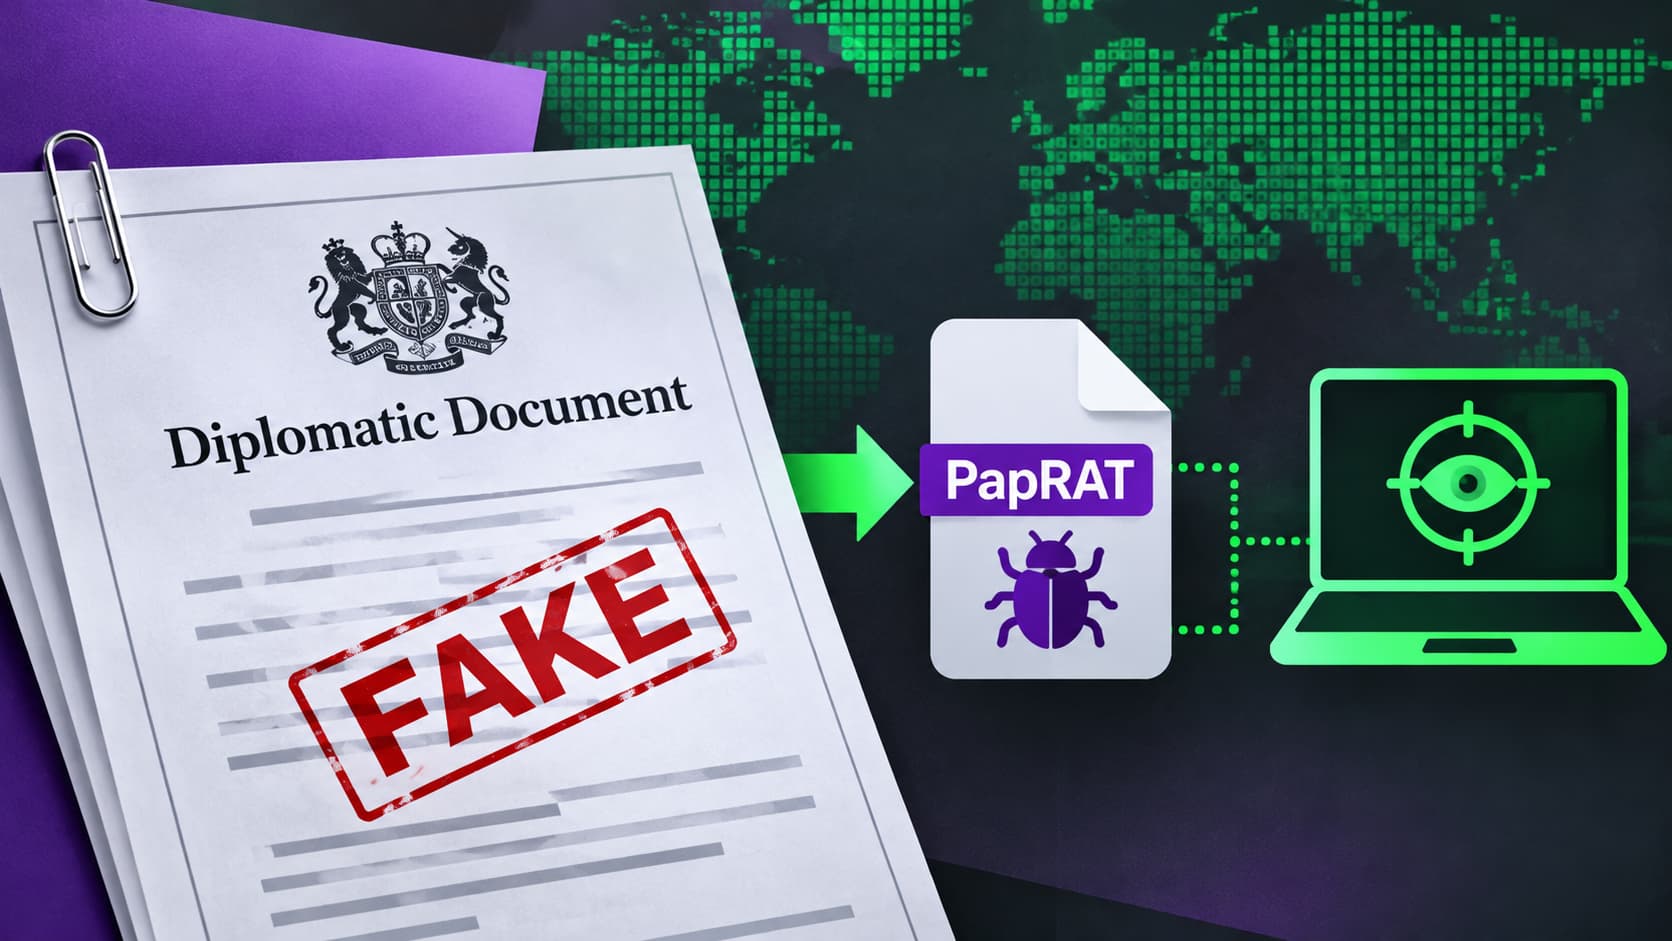
Fortinet’s FortiGuard Labs has detailed a cyberespionage campaign targeting South Asian organizations in government, energy, and engineering sectors. The researchers attribute the activity with high confidence to BITTER APT, a suspected South Asian group active since at least 2013.
Infection Chains Explained
FortiGuard Labs identified three chains BITTER uses to deliver a custom remote access trojan (RAT) called PapRAT to Windows systems, and noted that the attackers didn’t rely on exploiting any software vulnerability but focused on deception mostly.
In one chain, attackers used diplomatic- and military-themed LNK shortcuts to launch a script disguised as an icon file through ftp.exe, and relied on living-off-the-land (LotL) techniques. Using built-in Windows utilities such as ftp.exe and curl, along with PowerShell and scheduled tasks, attackers ran commands without initially dropping a conventional malware executable.
The script gathered system and antivirus information and sent the data to a command-and-control (C2) server...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE