

Azure Firewall Security: How Routing Decisions Can Bypass Inspection
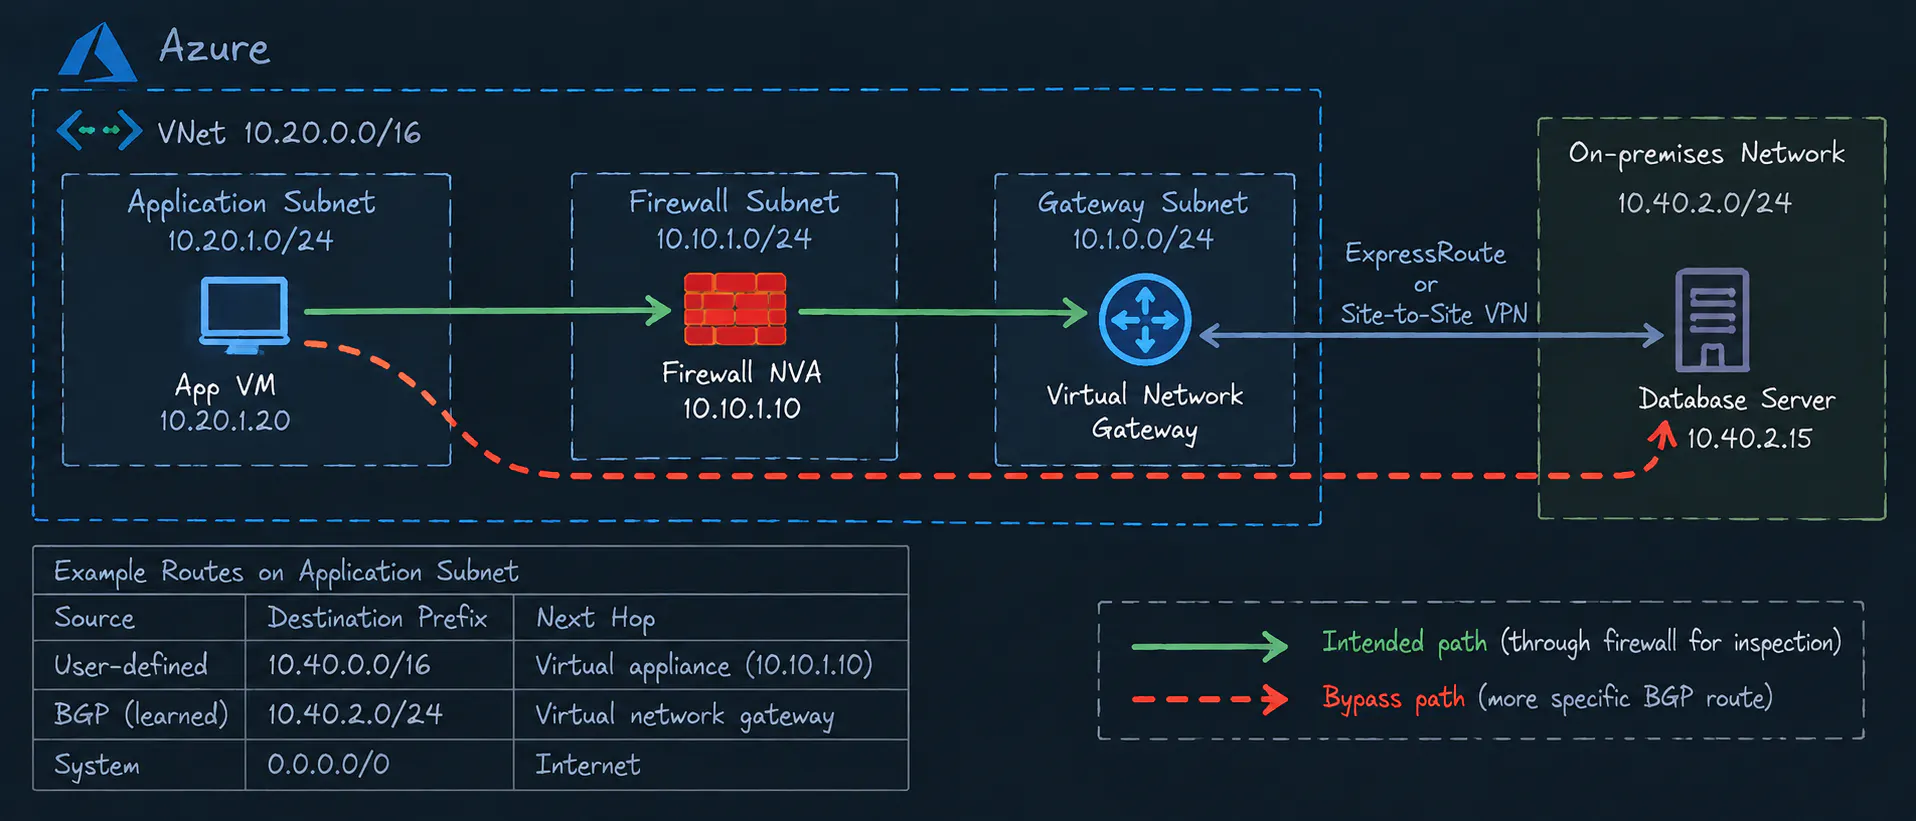
An engineering look at route selection, stateful firewalls, and practical troubleshooting in Microsoft Azure.
For cloud network and security engineers designing centralized inspection in Azure.
A firewall rule can be correct, logging can be on, and the appliance can be healthy, yet traffic may still reach its destination without ever passing through the inspection point. In Azure, routing and policy enforcement are separate layers: user-defined routes (UDRs), BGP-learned routes, virtual network peering, and managed connectivity services decide where packets go, and none of them consult your firewall policy. A firewall cannot inspect traffic it never receives.
The example below is a lab-style scenario with fictional addresses, built from publicly documented Azure behavior. The later sections cover return paths, Virtual WAN, and who is allowed to change routes.
1. How Azure chooses a route
Azure picks a route for outbound subnet traffic by longest prefix match, so a more specific route...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE


